
 Do Son
Synology restricts third-party drives in its 2025 Plus NAS series, limiting features like health reports. Learn about the new policy and workarounds.

Windows 11 update KB5055523 causes BSOD errors. Microsoft deploys Known Issue Rollback (KIR) to fix. Reboot device for faster resolution.

Microsoft will disable ActiveX controls in Office 365 & 2024 to enhance security. Users can re-enable manually, but it poses security risks.

Microsoft warns classic Outlook users of high CPU usage during text input. Temporary workaround via registry edit provided. Fix pending in future update

OpenAI launches o3 and o4-mini models, enhancing multimodal AI. GPT-5 announcement coming soon. Explore new capabilities and developer tools.

Google's 2024 Ads Safety Report details increased AI use to combat fraud. Millions of accounts suspended, billions of ads removed for policy violations.

OpenAI releases Codex CLI, an open-source AI programming assistant for terminals. Generate, edit, and execute code via natural language. API key required.

Anonymous claims 10TB cyberattack on Russia, exposing Kremlin-linked files, foreign assets, and data labeled “Donald Trump.”

CVE-2025-32433 in Erlang/OTP SSH server enables unauthenticated RCE. Patch now to prevent full system compromise across all affected versions.
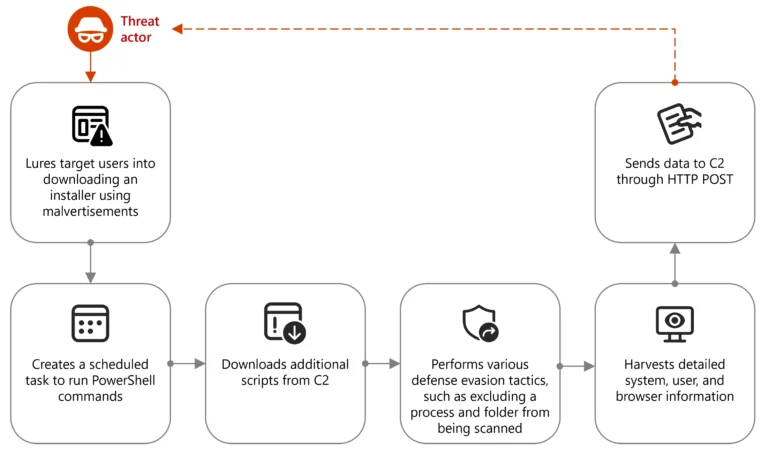
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

Malvertising campaign targets Onfido users via deceptive Google ads, using Evilginx to steal credentials.

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

Cyberattacks are surging against the energy sector, driven by geopolitical tensions. Ransomware, espionage, and supply chain attacks pose major threats.

Cisco patches CVE-2025-20236, an RCE flaw in Webex App exploitable via crafted links. Users urged to update to avoid command execution risks.

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025

Unprotected APIs exposed sensitive data of over 33,000 employees. CloudSEK's BeVigil discovered the security flaw

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.

Apple releases urgent patches for zero-day flaws (CVE-2025-31200, CVE-2025-31201) targeting iPhones. Update now to protect your devices from sophisticated attacks.

CVE-2025-24054 exploited to leak NTLM hashes via .library-ms files with near-zero user interaction. Patch now to avoid exposure.

CISA extends funding for the CVE program, ensuring no disruption to global vulnerability tracking and cybersecurity infrastructure.