
 cybernewswire
Palo Alto, California, 16th April 2025, CyberNewsWire

 Do Son
The CVE Foundation launches to ensure the future of the CVE Program after U.S. government funding ends for MITRE's operation.

4chan was hit by a cyberattack resulting in the leak of source code, user data, and admin info. The forum is currently inaccessible

Google will stop using country-code domains (ccTLDs), directing all searches to Google.com for localized results. Learn more.

Anthropic integrates Claude AI with Google Workspace, enabling AI analysis across Gmail, Docs, Calendar. Paid subscribers gain access.
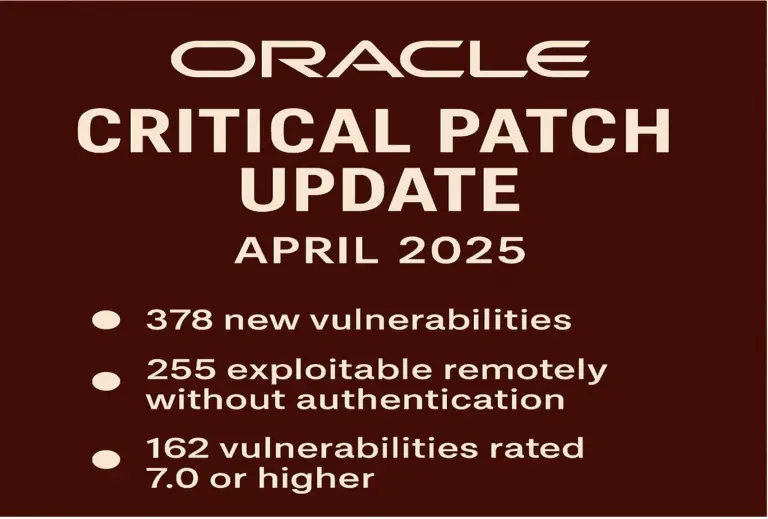
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

In today’s digital landscape, ISP proxies have become indispensable for businesses and individuals seeking reliable, high-speed, and...

OpenAI is reportedly developing a social network, potentially integrating ChatGPT. Learn about their plans, and the Altman/Musk rivalry behind it.

VSCode extension errors in Cursor? Learn why Microsoft's licensing restricts C/C++ & Remote SSH in non-Microsoft editors. Discover open-source alternatives

Ransomware attacks increasingly target SQL databases containing mission-critical information, posing existential threats to organizations. When databases are encrypted or corrupted,...

A curated list of the top cybersecurity tools for 2025, covering reconnaissance, wireless hacking, password cracking, forensics, and more.

Google Chrome 135 fixes critical CVE-2025-3619 and high CVE-2025-3620 flaws. Users urged to update now to avoid potential code execution threats.
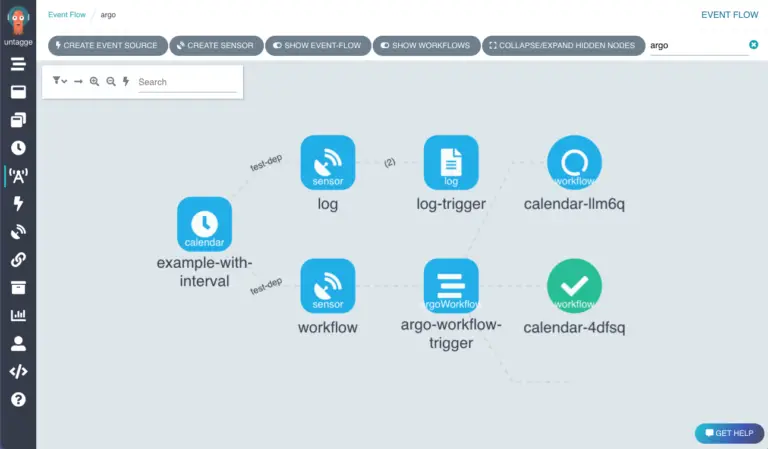
A critical vulnerability (CVE-2025-32445) in Argo Events allows users to gain privileged access to Kubernetes clusters. Upgrade to v1.9.6 to patch.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.

MITRE warns the CVE program may halt after April 16 as U.S. funding expires, threatening global cybersecurity and vulnerability tracking.

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.
A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.

Kandji's research uncovers PasivRobber, a sophisticated macOS malware suite targeting user data. Learn about its deceptive tactics and capabilities.

A malicious npm package, disguised as an Advcash integration, contains a reverse shell that triggers after successful payments, granting attackers server access.

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

iFAX Solutions discloses a critical remote code execution vulnerability (CVE-2025-1782) affecting HylaFAX and AvantFAX due to improper sanitization

Trend Micro uncovers BPFDoor backdoor used in cyberespionage across Asia and the Middle East, attributing it to the Red Menshen APT group