Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Synology NAS: Third-Party Drives Restricted in 2025 Plus Series Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Technology

Synology NAS: Third-Party Drives Restricted in 2025 Plus Series

Do Son April 17, 2025 0

Synology restricts third-party drives in its 2025 Plus NAS series, limiting features like health reports. Learn about the new policy and workarounds.

Windows 11 Update KB5055523 Causing BSOD Errors Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

Windows 11 Update KB5055523 Causing BSOD Errors

Do Son April 17, 2025 0

Windows 11 update KB5055523 causes BSOD errors. Microsoft deploys Known Issue Rollback (KIR) to fix. Reboot device for faster resolution.

Microsoft to Disable ActiveX Controls in Office 365 and 2024 Microsoft Patch Tuesday CVE-2026-20805 RasMan Crash Flaw, 0patch Micropatch ASP.NET Core, HTTP smuggling Windows kernel Rust ActiveX, Microsoft 365
  • Technology

Microsoft to Disable ActiveX Controls in Office 365 and 2024

Do Son April 17, 2025 0

Microsoft will disable ActiveX controls in Office 365 & 2024 to enhance security. Users can re-enable manually, but it poses security risks.

Microsoft Warns of High CPU Usage in Classic Outlook Exfil Out&Look Microsoft 365 Logging Gap Outlook Classic KB5074109 freeze, January 2026 POP3 PST bug Outlook Classic POP3 freeze, KB5074109 Windows 11 bug Outlook, CPU Usage Outlook lag Outlook Lite discontinued
  • Technology

Microsoft Warns of High CPU Usage in Classic Outlook

Do Son April 17, 2025 0

Microsoft warns classic Outlook users of high CPU usage during text input. Temporary workaround via registry edit provided. Fix pending in future update

OpenAI Unveils o3 & o4-mini Models, Announces GPT-5 Plans ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

OpenAI Unveils o3 & o4-mini Models, Announces GPT-5 Plans

Do Son April 17, 2025 0

OpenAI launches o3 and o4-mini models, enhancing multimodal AI. GPT-5 announcement coming soon. Explore new capabilities and developer tools.

Google Ads Safety Report: AI Drives Fraud Prevention CVE-2024-36383
  • Cybercriminals

Google Ads Safety Report: AI Drives Fraud Prevention

Do Son April 17, 2025 0

Google's 2024 Ads Safety Report details increased AI use to combat fraud. Millions of accounts suspended, billions of ads removed for policy violations.

OpenAI Launches Codex CLI: AI Programming Assistant for Terminals Codex CLI, OpenAI
  • Technology

OpenAI Launches Codex CLI: AI Programming Assistant for Terminals

Do Son April 17, 2025 0

OpenAI releases Codex CLI, an open-source AI programming assistant for terminals. Generate, edit, and execute code via natural language. API key required.

Anonymous Releases 10TB of Leaked Data Targeting Russia Anonymous, Data Leak
  • Cyber Security
  • Data Leak

Anonymous Releases 10TB of Leaked Data Targeting Russia

Do Son April 17, 2025 0

Anonymous claims 10TB cyberattack on Russia, exposing Kremlin-linked files, foreign assets, and data labeled “Donald Trump.”

Erlang/OTP CVE-2025-32433 (CVSS 10): Critical SSH Flaw Allows Unauthenticated RCE Erlang/OTP, remote code execution
  • Vulnerability

Erlang/OTP CVE-2025-32433 (CVSS 10): Critical SSH Flaw Allows Unauthenticated RCE

Do Son April 17, 2025 0

CVE-2025-32433 in Erlang/OTP SSH server enables unauthenticated RCE. Patch now to prevent full system compromise across all affected versions.
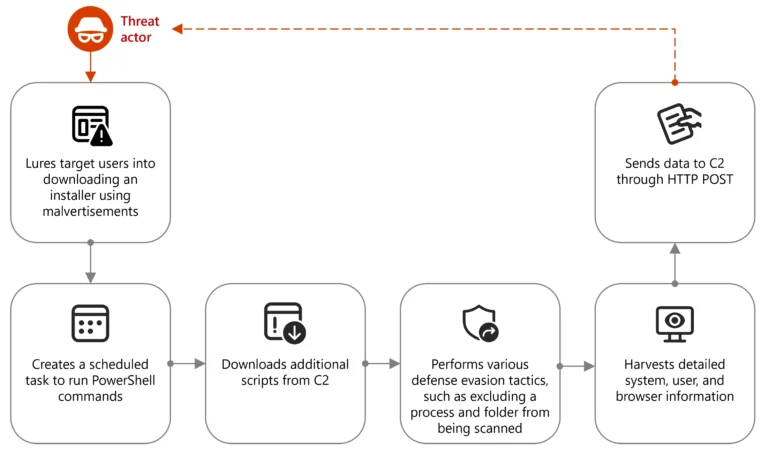
Node.js Misused in Malvertising Campaigns to Deliver Stealthy Malware Node.js malware, malvertising attacks
  • Malware

Node.js Misused in Malvertising Campaigns to Deliver Stealthy Malware

Do Son April 17, 2025 0

Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

Onfido Users Targeted in Google Ad Malvertising Campaign malver
  • Cybercriminals

Onfido Users Targeted in Google Ad Malvertising Campaign

Do Son April 17, 2025 0

Malvertising campaign targets Onfido users via deceptive Google ads, using Evilginx to steal credentials.

Novel Attack Uses Teams Phishing and Zero-Day TypeLib Hijacking Oracle EBS Zero-Day, GRACEFUL SPIDER Cracked Software, Supply Chain Attack Black Basta - NOVA stealer
  • Cybercriminals
  • Malware

Novel Attack Uses Teams Phishing and Zero-Day TypeLib Hijacking

Do Son April 17, 2025 0

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

Cyberattacks Surge Against Energy Sector Amid Geopolitical Tensions Energy Sector, Cyberattacks
  • Cyber Security

Cyberattacks Surge Against Energy Sector Amid Geopolitical Tensions

Do Son April 17, 2025 0

Cyberattacks are surging against the energy sector, driven by geopolitical tensions. Ransomware, espionage, and supply chain attacks pose major threats.

Cisco Patches CVE-2025-20236: Unauthenticated RCE Flaw in Webex App via Malicious Meeting Links Webex RCE, CVE-2025-20236
  • Vulnerability

Cisco Patches CVE-2025-20236: Unauthenticated RCE Flaw in Webex App via Malicious Meeting Links

Do Son April 17, 2025 0

Cisco patches CVE-2025-20236, an RCE flaw in Webex App exploitable via crafted links. Users urged to update to avoid command execution risks.

APT29 Targets European Diplomats with Wine-Themed Phishing APT29, Phishing Campaign
  • Cyber Security
  • Malware

APT29 Targets European Diplomats with Wine-Themed Phishing

Do Son April 17, 2025 0

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

CISA Alert: Actively Exploited SonicWall SMA100 Vulnerability SonicWall vulnerability, CVE-2021-20035 Vulnerability Exploitation
  • Vulnerability

CISA Alert: Actively Exploited SonicWall SMA100 Vulnerability

Do Son April 17, 2025 0

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025

Unprotected APIs Expose Data of 33,000 Employees API Security, Data Leak
  • Data Leak

Unprotected APIs Expose Data of 33,000 Employees

Do Son April 17, 2025 0

Unprotected APIs exposed sensitive data of over 33,000 employees. CloudSEK's BeVigil discovered the security flaw

LummaStealer: The Evolution of a Sophisticated MaaS LummaStealer, Malware-as-a-Service
  • Malware

LummaStealer: The Evolution of a Sophisticated MaaS

Do Son April 17, 2025 0

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

CrazyHunter Ransomware Targets Taiwan’s Critical Infrastructure CrazyHunter, Ransomware
  • Cybercriminals
  • Malware

CrazyHunter Ransomware Targets Taiwan’s Critical Infrastructure

Do Son April 17, 2025 0

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.

Urgent Apple Security Patch: Zero-Day Exploits Target iPhones Apple zero-day, iPhone exploit
  • Vulnerability

Urgent Apple Security Patch: Zero-Day Exploits Target iPhones

Do Son April 16, 2025 0

Apple releases urgent patches for zero-day flaws (CVE-2025-31200, CVE-2025-31201) targeting iPhones. Update now to protect your devices from sophisticated attacks.

CVE-2025-24054: Actively Exploited NTLM Hash Disclosure Vulnerability CVE-2025-24054, NTLM
  • Cybercriminals
  • Vulnerability

CVE-2025-24054: Actively Exploited NTLM Hash Disclosure Vulnerability

Do Son April 16, 2025 0

CVE-2025-24054 exploited to leak NTLM hashes via .library-ms files with near-zero user interaction. Patch now to avoid exposure.

CISA Extends CVE Program Funding to Prevent Critical Service Disruption CVE Program, CISA Funding
  • Technology
  • Vulnerability

CISA Extends CVE Program Funding to Prevent Critical Service Disruption

Do Son April 16, 2025 0

CISA extends funding for the CVE program, ensuring no disruption to global vulnerability tracking and cybersecurity infrastructure.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-89126CVSS 10.0
    SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89119CVSS 9.6
    SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89103CVSS 10.0
    SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76964CVSS 10.0
    SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76965CVSS 9.9
    SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality....
    📅 Updated: Nov 10, 2026
  • CVE-2026-120017CVSS 10.0
    SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain...
    📅 Updated: Nov 10, 2026
  • CVE-2026-109803CVSS 9.9
    SAP NetWeaver Knowledge Management (XML Forms) does not sufficiently restrict the selection of XSL transformations processed by the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-109795CVSS 9.9
    SAP NetWeaver does not perform necessary authorization checks and lacks sufficient input validation in certain remote-enabled functionality. An...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.