Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CISA Extends CVE Program Funding to Prevent Critical Service Disruption CVE Program, CISA Funding
  • Technology
  • Vulnerability

CISA Extends CVE Program Funding to Prevent Critical Service Disruption

Do Son April 16, 2025 0

CISA extends funding for the CVE program, ensuring no disruption to global vulnerability tracking and cybersecurity infrastructure.

SquareX to Uncover Data Splicing Attacks at BSides San Francisco, A Major DLP Flaw that Compromises Data Security of Millions Press_20250411_01_Data_Splicing_Attacks_Cybernews__1744621063uT70h2PuvA
  • Press Release

SquareX to Uncover Data Splicing Attacks at BSides San Francisco, A Major DLP Flaw that Compromises Data Security of Millions

cybernewswire April 16, 2025 0
Palo Alto, California, 16th April 2025, CyberNewsWire
Read More Read more about SquareX to Uncover Data Splicing Attacks at BSides San Francisco, A Major DLP Flaw that Compromises Data Security of Millions
CVE Foundation Launched to Secure Vulnerability Tracking CVE Foundation, CVE Program
  • Technology
  • Vulnerability

CVE Foundation Launched to Secure Vulnerability Tracking

Do Son April 16, 2025 0

The CVE Foundation launches to ensure the future of the CVE Program after U.S. government funding ends for MITRE's operation.

4chan Suffers Major Cyberattack, Sensitive Data Leaked 4chan hack 4chan data breach
  • Cybercriminals
  • Data Leak

4chan Suffers Major Cyberattack, Sensitive Data Leaked

Do Son April 16, 2025 0

4chan was hit by a cyberattack resulting in the leak of source code, user data, and admin info. The forum is currently inaccessible

Google to Unify Search Under Google.com Android ChromeOS Merger, Google OS Unification Google monopolistic dominance Google ccTLD
  • Technology

Google to Unify Search Under Google.com

Do Son April 16, 2025 0

Google will stop using country-code domains (ccTLDs), directing all searches to Google.com for localized results. Learn more.

Claude AI Integrates with Google Workspace Claude AI Google Workspace
  • Technology

Claude AI Integrates with Google Workspace

Do Son April 16, 2025 0

Anthropic integrates Claude AI with Google Workspace, enabling AI analysis across Gmail, Docs, Calendar. Paid subscribers gain access.
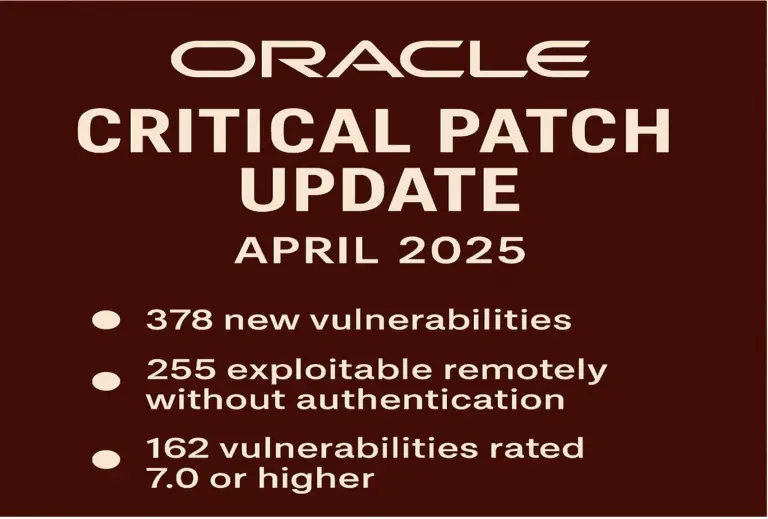
Oracle April 2025 CPU: 378 Security Patches Released Oracle CPU Oracle Patch Update
  • Vulnerability

Oracle April 2025 CPU: 378 Security Patches Released

Do Son April 16, 2025 0

Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

Top 6 ISP Proxies in 2025: The Definitive Guide to Performance and Security CVE-2023-49606
  • Technology

Top 6 ISP Proxies in 2025: The Definitive Guide to Performance and Security

Do Son April 16, 2025 0
In today’s digital landscape, ISP proxies have become indispensable for businesses and individuals seeking reliable, high-speed, and...
Read More Read more about Top 6 ISP Proxies in 2025: The Definitive Guide to Performance and Security
OpenAI’s “X” Rival: Social Network Plans Emerge OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

OpenAI’s “X” Rival: Social Network Plans Emerge

Do Son April 16, 2025 0

OpenAI is reportedly developing a social network, potentially integrating ChatGPT. Learn about their plans, and the Altman/Musk rivalry behind it.

VSCode Extension Errors in Cursor: Understanding Microsoft’s Restrictions VSCode Extensions Cursor Errors
  • Technology

VSCode Extension Errors in Cursor: Understanding Microsoft’s Restrictions

Do Son April 16, 2025 0

VSCode extension errors in Cursor? Learn why Microsoft's licensing restricts C/C++ & Remote SSH in non-Microsoft editors. Discover open-source alternatives

SQL Database Recovery After Ransomware Img_2025_04_15_05_21_44
  • Technique

SQL Database Recovery After Ransomware

Do Son April 16, 2025 0
Ransomware attacks increasingly target SQL databases containing mission-critical information, posing existential threats to organizations. When databases are encrypted or corrupted,...
Read More Read more about SQL Database Recovery After Ransomware
Top Cybersecurity Tools for 2025 Cybersecurity Tools Penetration Testing
  • Open Source Tool

Top Cybersecurity Tools for 2025

Do Son April 16, 2025 0

A curated list of the top cybersecurity tools for 2025, covering reconnaissance, wireless hacking, password cracking, forensics, and more.

Critical Chrome Security Update: Patch CVE-2025-3619 & CVE-2025-3620 Now! Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Vulnerability

Critical Chrome Security Update: Patch CVE-2025-3619 & CVE-2025-3620 Now!

Do Son April 16, 2025 0

Google Chrome 135 fixes critical CVE-2025-3619 and high CVE-2025-3620 flaws. Users urged to update now to avoid potential code execution threats.
Critical CVE-2025-32445 Vulnerability in Argo Events Scores CVSS 10 Argo Events Kubernetes Security
  • Vulnerability

Critical CVE-2025-32445 Vulnerability in Argo Events Scores CVSS 10

Do Son April 16, 2025 0

A critical vulnerability (CVE-2025-32445) in Argo Events allows users to gain privileged access to Kubernetes clusters. Upgrade to v1.9.6 to patch.

Waiting Thread Hijacking: A Stealthier Code Injection Technique Thread Hijacking Process Injection
  • Malware
  • Open Source Tool

Waiting Thread Hijacking: A Stealthier Code Injection Technique

Do Son April 16, 2025 0

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.

MITRE Warns of CVE Program Disruption as U.S. Contract Set to Expire CVE Program, MITRE
  • Technology
  • Vulnerability

MITRE Warns of CVE Program Disruption as U.S. Contract Set to Expire

Do Son April 16, 2025 0

MITRE warns the CVE program may halt after April 16 as U.S. funding expires, threatening global cybersecurity and vulnerability tracking.

Windows 11 Privilege Escalation Flaws Uncovered: CVE-2025-24076 and CVE-2025-24994 DLL Hijacking, CVE-2025-24076
  • Vulnerability

Windows 11 Privilege Escalation Flaws Uncovered: CVE-2025-24076 and CVE-2025-24994

Do Son April 16, 2025 0

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.
UNC5174: Chinese Threat Actor Deploys New VShell RAT in Campaign Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Cyber Security
  • Malware

UNC5174: Chinese Threat Actor Deploys New VShell RAT in Campaign

Do Son April 16, 2025 0

A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.

PasivRobber: In-Depth Analysis of Sophisticated macOS Malware GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Malware

PasivRobber: In-Depth Analysis of Sophisticated macOS Malware

Do Son April 16, 2025 0

Kandji's research uncovers PasivRobber, a sophisticated macOS malware suite targeting user data. Learn about its deceptive tactics and capabilities.

Malicious npm Package Installs Reverse Shell via Payment Success Magento Credit Card Stealer npm package reverse shell
  • Malware

Malicious npm Package Installs Reverse Shell via Payment Success

Do Son April 16, 2025 0

A malicious npm package, disguised as an Advcash integration, contains a reverse shell that triggers after successful payments, granting attackers server access.

Beware Fake PDF Converters: A Social Engineering Threat shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Malware

Beware Fake PDF Converters: A Social Engineering Threat

Do Son April 16, 2025 0

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

Critical RCE Vulnerability Affects HylaFAX and AvantFAX CVE-2024-52335 HylaFAX, AvantFAX vulnerability
  • Vulnerability

Critical RCE Vulnerability Affects HylaFAX and AvantFAX

Do Son April 16, 2025 0

iFAX Solutions discloses a critical remote code execution vulnerability (CVE-2025-1782) affecting HylaFAX and AvantFAX due to improper sanitization

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123218CVSS 9.8
    IBM Aspera Faspex 5.0.0 through 5.0.19 could allow an authorized user to craft a specific message to bypass...
    CISA KEV📅 Added to KEV: Nov 9, 2026📅 Updated: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-89126CVSS 10.0
    SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89119CVSS 9.6
    SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89103CVSS 10.0
    SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76964CVSS 10.0
    SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76965CVSS 9.9
    SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality....
    📅 Updated: Nov 10, 2026
  • CVE-2026-120017CVSS 10.0
    SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.