Skip to content
October 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
IBM Security Verify Directory Vulnerable to Critical Security Flaw – CVE-2024-51450 (CVSS 9.1) IBM API Connect, CVE-2025-13915 IBM Privilege Escalation, CVE-2025-36356 IBM Power Systems - CVE-2024-45656 CVE-2024-49814 and CVE-2024-51450 CVE-2024-56346 and CVE-2024-56347 CVE-2025-1302
  • Vulnerability

IBM Security Verify Directory Vulnerable to Critical Security Flaw – CVE-2024-51450 (CVSS 9.1)

Do Son February 7, 2025 0
Read More Read more about IBM Security Verify Directory Vulnerable to Critical Security Flaw – CVE-2024-51450 (CVSS 9.1)
AsyncRAT Rises Again: Malware Abuses Legitimate Services for Stealthy Delivery AsyncRAT Delivery
  • Malware

AsyncRAT Rises Again: Malware Abuses Legitimate Services for Stealthy Delivery

Do Son February 7, 2025 0
Read More Read more about AsyncRAT Rises Again: Malware Abuses Legitimate Services for Stealthy Delivery
CVE-2025-0994: Critical Vulnerability in Trimble Cityworks Exploited in the Wild CVE-2025-0994
  • Vulnerability

CVE-2025-0994: Critical Vulnerability in Trimble Cityworks Exploited in the Wild

Do Son February 7, 2025 0
Read More Read more about CVE-2025-0994: Critical Vulnerability in Trimble Cityworks Exploited in the Wild
Arm Drops NUVIA Lawsuit Against Qualcomm CVE-2023-4211 - Arm Lawsuit
  • Technology

Arm Drops NUVIA Lawsuit Against Qualcomm

Do Son February 7, 2025 0
Read More Read more about Arm Drops NUVIA Lawsuit Against Qualcomm
CVE-2024-21413 (CVSS 9.8): Critical Outlook Flaw Under Active Attack, PoC Available CVE-2024-21413 exploit
  • Vulnerability

CVE-2024-21413 (CVSS 9.8): Critical Outlook Flaw Under Active Attack, PoC Available

Do Son February 7, 2025 0
Read More Read more about CVE-2024-21413 (CVSS 9.8): Critical Outlook Flaw Under Active Attack, PoC Available
Google’s SynthID Now in Magic Editor: AI Image Detection SynthID Magic Editor
  • Technology

Google’s SynthID Now in Magic Editor: AI Image Detection

Do Son February 7, 2025 0
Read More Read more about Google’s SynthID Now in Magic Editor: AI Image Detection
MMS “VidSpam”: A New Bitcoin Scam Using Old Tech Crypto Drain Conspiracy, Malicious MobileConfig phone phishing Cryptocurrency Phishing
  • Cyber Security

MMS “VidSpam”: A New Bitcoin Scam Using Old Tech

Do Son February 7, 2025 0
Read More Read more about MMS “VidSpam”: A New Bitcoin Scam Using Old Tech
NETGEAR Patches Critical Security Vulnerabilities in WiFi Routers (CVE-2025-25246) and Access Points CVE-2022-48196 NETGEAR Security Vulnerabilities
  • Vulnerability

NETGEAR Patches Critical Security Vulnerabilities in WiFi Routers (CVE-2025-25246) and Access Points

Do Son February 6, 2025 0
Read More Read more about NETGEAR Patches Critical Security Vulnerabilities in WiFi Routers (CVE-2025-25246) and Access Points
Kimsuky Group Leverages RDP Wrapper for Persistent Cyber Espionage North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Cyber Security
  • Malware

Kimsuky Group Leverages RDP Wrapper for Persistent Cyber Espionage

Do Son February 6, 2025 0
Read More Read more about Kimsuky Group Leverages RDP Wrapper for Persistent Cyber Espionage
CVE-2024-9643 & CVE-2024-9644: Authentication Bypass in Four-Faith F3x36 Routers Puts Networks at Risk CVE-2024-9643 & CVE-2024-9644
  • Vulnerability

CVE-2024-9643 & CVE-2024-9644: Authentication Bypass in Four-Faith F3x36 Routers Puts Networks at Risk

Do Son February 6, 2025 0
Read More Read more about CVE-2024-9643 & CVE-2024-9644: Authentication Bypass in Four-Faith F3x36 Routers Puts Networks at Risk
Apache James Mail Server Hit by Double Denial-of-Service Vulnerabilities CVE-2024-45626 and CVE-2024-37358
  • Vulnerability

Apache James Mail Server Hit by Double Denial-of-Service Vulnerabilities

Do Son February 6, 2025 0
Read More Read more about Apache James Mail Server Hit by Double Denial-of-Service Vulnerabilities
BADBOX Botnet: Pre-installed Malware Targets Android Devices Android BADBOX Botnet
  • Malware

BADBOX Botnet: Pre-installed Malware Targets Android Devices

Do Son February 6, 2025 0
Read More Read more about BADBOX Botnet: Pre-installed Malware Targets Android Devices
HPE Aruba Networking Issues Security Updates for ClearPass Policy Manager CVE-2024-26305 _ CVE-2025-23058 Aruba 5G Core Open Redirect
  • Vulnerability

HPE Aruba Networking Issues Security Updates for ClearPass Policy Manager

Do Son February 6, 2025 0
Read More Read more about HPE Aruba Networking Issues Security Updates for ClearPass Policy Manager
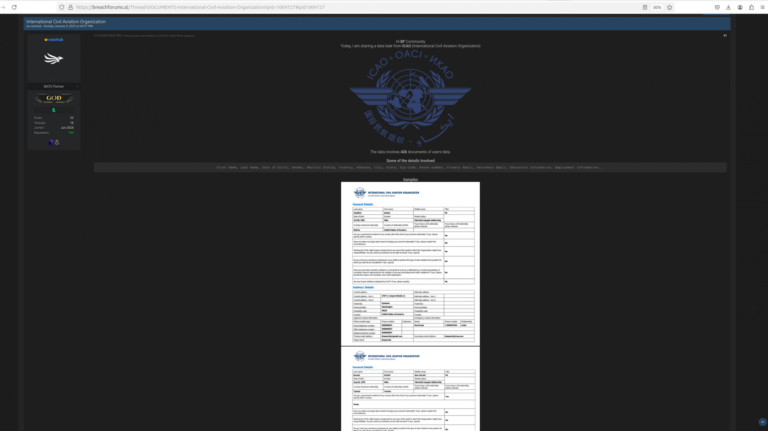
Cyberespionage Targets Aviation: ICAO and ACAO Breached Cyberespionage
  • Data Leak

Cyberespionage Targets Aviation: ICAO and ACAO Breached

Do Son February 6, 2025 0
Read More Read more about Cyberespionage Targets Aviation: ICAO and ACAO Breached
Vitest Vulnerability Exposes Developers to Remote Code Execution – CVE-2025-24964 (CVSS 9.7) CVE-2025-24964
  • Vulnerability

Vitest Vulnerability Exposes Developers to Remote Code Execution – CVE-2025-24964 (CVSS 9.7)

Do Son February 6, 2025 0
Read More Read more about Vitest Vulnerability Exposes Developers to Remote Code Execution – CVE-2025-24964 (CVSS 9.7)
Threat Actors Continue to Exploit Legitimate RMM Tool ScreenConnect KongTuke Microsoft Teams Phishing ModeloRAT Initial Access Broker CVE-2024-38193 - Lazarus Group Threat Actors ScreenConnect
  • Cyber Security

Threat Actors Continue to Exploit Legitimate RMM Tool ScreenConnect

Do Son February 6, 2025 0
Read More Read more about Threat Actors Continue to Exploit Legitimate RMM Tool ScreenConnect
ValleyRAT Returns: Silver Fox APT Deploys New Delivery Techniques for Multi-Stage Attacks DriverFixer0428, Contagious Interview Cache Smuggling, ClickFix Evasion North Korean Cyber Espionage
  • Malware

ValleyRAT Returns: Silver Fox APT Deploys New Delivery Techniques for Multi-Stage Attacks

Do Son February 6, 2025 0
Read More Read more about ValleyRAT Returns: Silver Fox APT Deploys New Delivery Techniques for Multi-Stage Attacks
GreenSpot APT Phishes 163.com Users with Spoofed Domains Oracle EBS Zero-Day, GRACEFUL SPIDER Cracked Software, Supply Chain Attack Black Basta - NOVA stealer
  • Cyber Security

GreenSpot APT Phishes 163.com Users with Spoofed Domains

Do Son February 6, 2025 0
Read More Read more about GreenSpot APT Phishes 163.com Users with Spoofed Domains
Windows 10 ESU Program: A Lifeline for Holdouts, But at What Cost? Windows 10 MSMQ Bug, KB5071546 Write Permissions Windows 10 Lawsuit Windows 10 ESU, Free Security Updates Windows 10 ESU program
  • Technology
  • Windows

Windows 10 ESU Program: A Lifeline for Holdouts, But at What Cost?

Do Son February 6, 2025 0
Read More Read more about Windows 10 ESU Program: A Lifeline for Holdouts, But at What Cost?
Gemini 2.0 Unleashed: Pro, Flash-Lite, & More Google Gemini, audio files Gemini AI, Google AI Google Gemini 2.0 Flash Thinking iOS
  • Technology

Gemini 2.0 Unleashed: Pro, Flash-Lite, & More

Do Son February 6, 2025 0
Read More Read more about Gemini 2.0 Unleashed: Pro, Flash-Lite, & More
Arch Linux on WSL 2: Microsoft Confirms Official Support Arch Linux WSL2
  • Linux
  • Vulnerability

Arch Linux on WSL 2: Microsoft Confirms Official Support

Do Son February 5, 2025 0
Read More Read more about Arch Linux on WSL 2: Microsoft Confirms Official Support
CVE-2025-20124 (CVSS 9.9) & CVE-2025-20125 (CVSS 9.1): Cisco Patches Critical Flaws in Identity Services Engine CVE-2025-20124 CVE-2025-20125
  • Vulnerability

CVE-2025-20124 (CVSS 9.9) & CVE-2025-20125 (CVSS 9.1): Cisco Patches Critical Flaws in Identity Services Engine

Do Son February 5, 2025 0
Read More Read more about CVE-2025-20124 (CVSS 9.9) & CVE-2025-20125 (CVSS 9.1): Cisco Patches Critical Flaws in Identity Services Engine
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-104286CVSS 9.8
    An improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiMail 8.0.0 through...
    CISA KEV📅 Added to KEV: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-15340CVSS 9.8
    lwIP SMTP client does not check the size of inputs, potentially allowing a buffer overflow.
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-16516CVSS 9.0
    wolfSSH does not validate that the ECDSA curve identifier in a KEXDH_REPLY host key blob matches the algorithm...
    📅 Updated: Oct 7, 2026
  • CVE-2026-14911CVSS 9.3
    Improper Neutralization of Input During Web Page Generation (“Cross-site Scripting”) in ASUS router modules allows a remote attacker...
    📅 Updated: Oct 7, 2026
  • CVE-2026-19386CVSS 9.3
    A stack-based buffer overflow in the ASUS router modules allows an authenticated nearby user to execute arbitrary code...
    📅 Updated: Oct 7, 2026
  • CVE-2026-105324CVSS 9.2
    An HTTP header injection vulnerability in start-page-loader.cgi of ADM allows an unauthenticated remote attacker to read arbitrary files...
    📅 Updated: Oct 7, 2026
  • CVE-2026-93674CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.2 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 7, 2026
  • CVE-2026-104334CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.2 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.