 Do Son
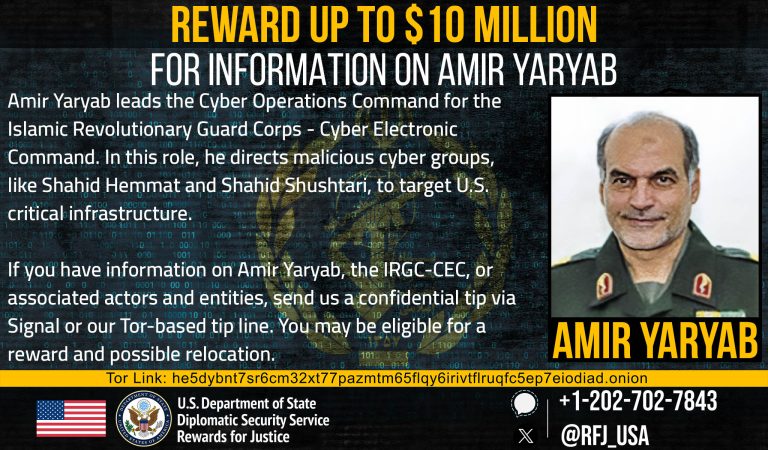
The US offers a $10 million reward for Amir Yaryab, an IRGC cyber commander linked to CyberAv3ngers attacks on critical water infrastructure.
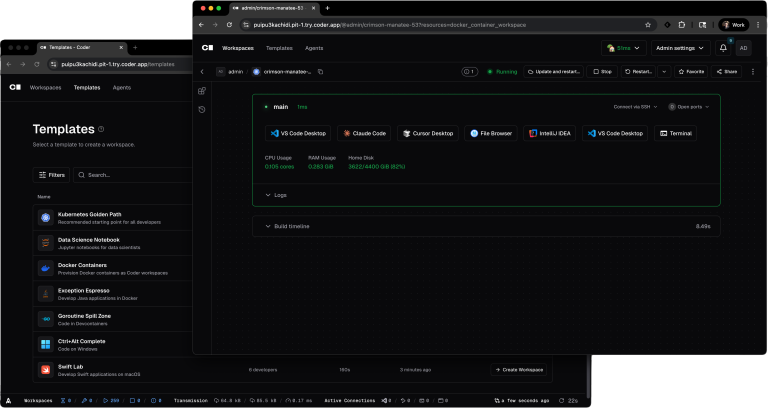
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
Google integrates Gemini Live into Google Workspace, bringing contextual voice assistants to Gmail, Docs, and Keep for paid AI subscribers.
An ASUS Control Center vulnerability, CVE-2026-75754 (CVSS 10), gives unauthenticated attackers a root shell. Update to v3.1.0.9 now.
Most AI security tools ship with one approve button. You click it and the action runs. You...
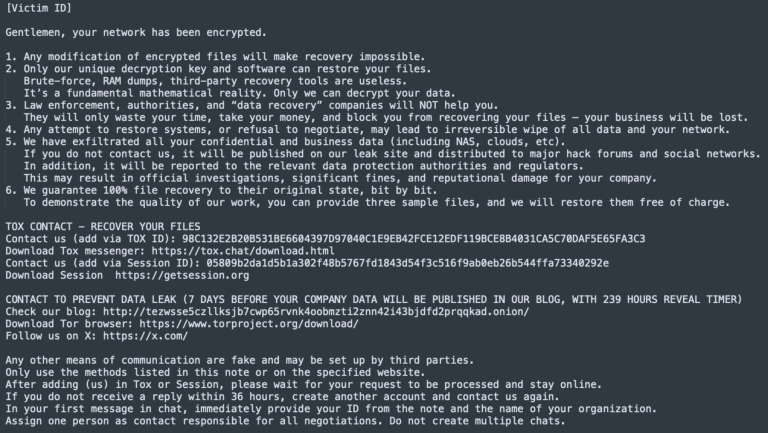
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
The Trezor data breach at shipping partner ShipMonk exposed about 80,000 customers' order data. Wallets are safe, but phishing risk is high.
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
The Toy Ghouls backdoor hides C2 traffic in HiveMQ MQTT and Element messenger. See how the Bearlyfy group's custom malware works.
Datadog uncovered an AWS password spraying campaign targeting cloud environments. Protect your accounts against this AWS password spraying activity now.
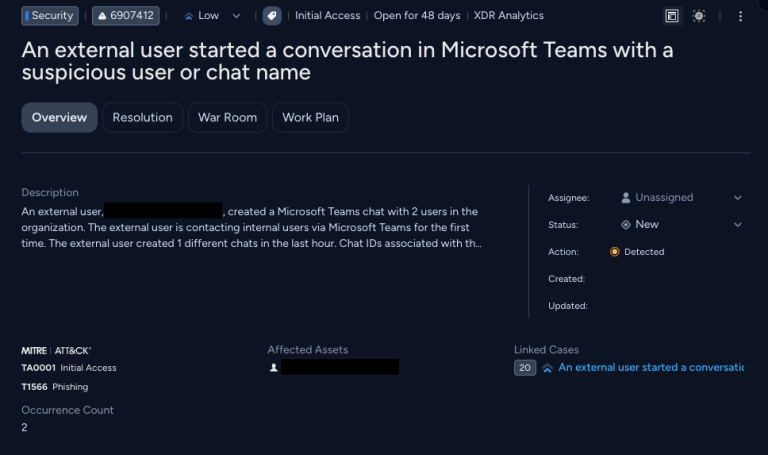
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.
Apache released version 1.21.0 to patch critical Apache Allura security vulnerabilities. Update now to protect against XSS, SSRF, and data exposure flaws.
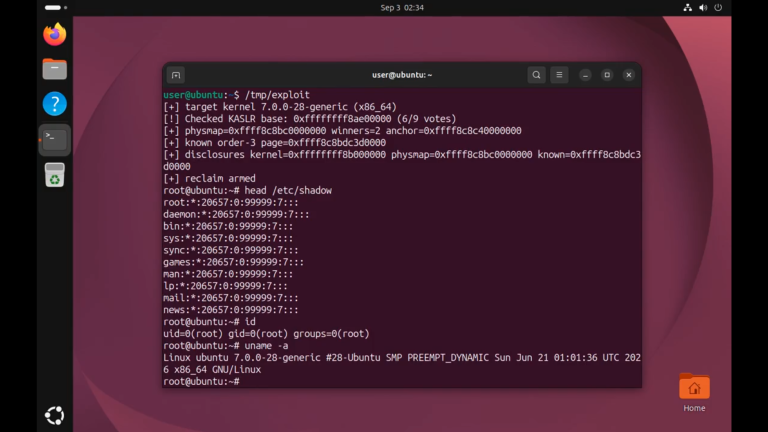
Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
Discover the new GPT-6 Astra Codex pricing policy. OpenAI now removes multiplier penalties for contexts exceeding 272K, offering flat rates up to 1M tokens.
A TP-Link Archer AX55 vulnerability (CVE-2026-18167) risks remote code execution via EasyMesh buffer overflow. Update to build 20260527 now.
Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
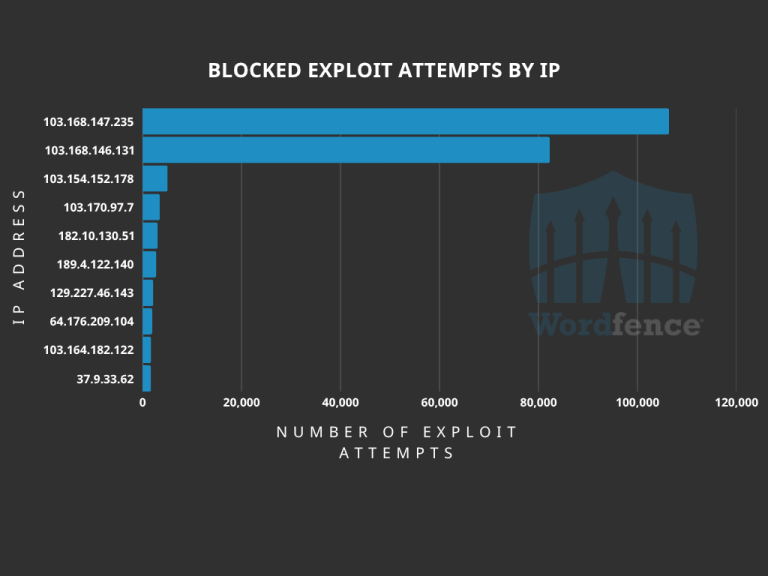
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
A critical WHMCS security update fixes CVE-2026-67399 and CVE-2026-67398. Apply the patch now to prevent remote code execution and data leaks.
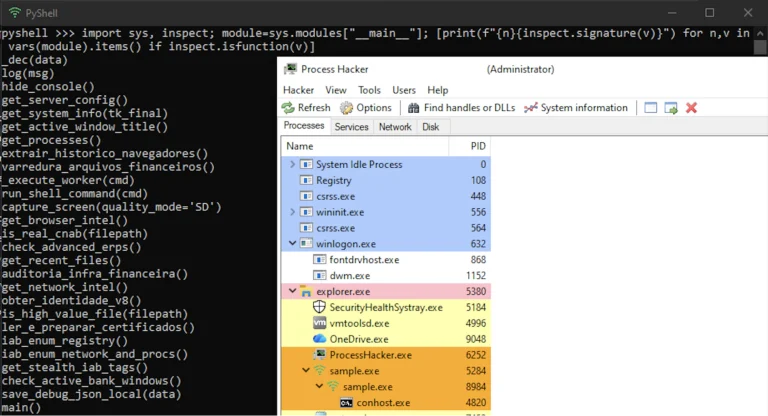
Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.
SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.