Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Optimizing QA Efforts with Risk-Based Testing Techniques devops-3155972_1280
  • Technique

Optimizing QA Efforts with Risk-Based Testing Techniques

Do Son February 10, 2025 0
As the complexity of software development continues to grow, ensuring a product’s stability and reliability under tight...
Read More Read more about Optimizing QA Efforts with Risk-Based Testing Techniques
Microsoft Integrates AI Agents into GitHub Copilot Copilot Edits - Project Padawan
  • Technology

Microsoft Integrates AI Agents into GitHub Copilot

Do Son February 10, 2025 0

Discover how Microsoft's GitHub Copilot revolutionizes software development with agent-based automation tools and Codebase Copilot Edits.

Cloudflare R2 Outage Explained: Accidental Shutdown Cloudflare layoffs 2026 AI bot traffic surge Content Signals Policy, AI Content Usage Cloudflare, Certificate Misissuance Salesforce, supply chain attack DDoS attack, Cloudflare Perplexity AI, Web Scraping Pay Per Crawl Cloudflare abuse R2 outage HTTP Cloudflare Blocking
  • Technology

Cloudflare R2 Outage Explained: Accidental Shutdown

Do Son February 10, 2025 0

Discover the details of the Cloudflare R2 outage, its impact on website content loading, and the root cause of the disruption.

PlayStation Network Down: Players Get 5-Day Extension PlayStation Network outage Sony Russia, business exit
  • Technology

PlayStation Network Down: Players Get 5-Day Extension

Do Son February 10, 2025 0

Learn about the recent PlayStation Network outage and its impact on players. Explore the disruptions and compensation offered by Sony.

Meta Sued for Training AI with 81.7TB of Copyrighted Data Meta Horizon Worlds Quest shutdown Meta AI, Child Safety Meta Robotics, Android of Robotics Meta AI, Llama 4.X Meta, AI regulation Meta AI, Data Center Impact Meta AI, Superintelligence Meta Copyrighted Data AI chatbot
  • Technology

Meta Sued for Training AI with 81.7TB of Copyrighted Data

Do Son February 9, 2025 0

The class-action lawsuit against Meta: allegations of copyright infringement and unfair competition in the use of copyrighted materials for AI training.

Meta’s Brain2Qwerty: Turning Brainwaves into Text with 80% Accuracy Brain2Qwerty
  • Technology

Meta’s Brain2Qwerty: Turning Brainwaves into Text with 80% Accuracy

Do Son February 9, 2025 0

Unlock the power of brain activity with Meta's Brain2Qwerty. Read about the technology that enables communication for those with speech loss.
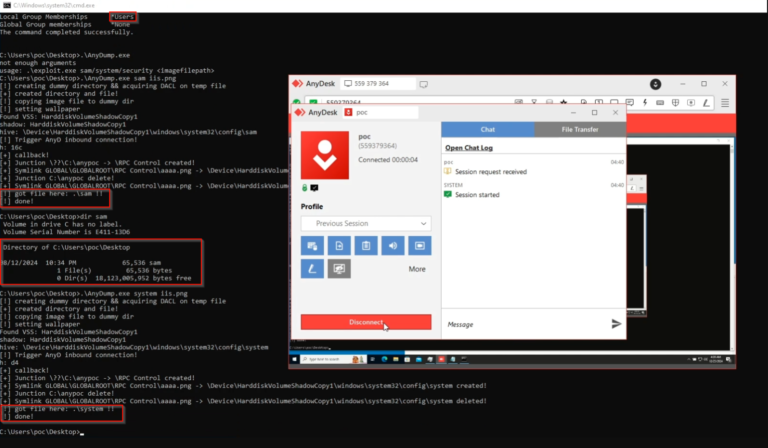
AnyDesk Exploit Alert: CVE-2024-12754 Enables Privilege Escalation—PoC Available CVE-2024-12754 PoC
  • Vulnerability

AnyDesk Exploit Alert: CVE-2024-12754 Enables Privilege Escalation—PoC Available

Do Son February 9, 2025 0

Discover the security flaw, CVE-2024-12754, found in AnyDesk. Find out how this vulnerability could grant unauthorized access and complete control of a system.

CVE-2025-25064 (CVSS 9.8): Critical SQL Injection Bug in Zimbra Collaboration Zimbra 10.1.16 Zimbra Security Update Zimbra LFI, CVE-2025-68645 CVE-2025-25065 & CVE-2025-25064
  • Vulnerability

CVE-2025-25064 (CVSS 9.8): Critical SQL Injection Bug in Zimbra Collaboration

Do Son February 9, 2025 0

Protect your business from Zimbra Collaboration vulnerabilities. Learn about the recently discovered CVE-2025-25064 SQL injection vulnerability and its potential impact.

Hackers Exploit Google Tag Manager to Steal Credit Card Data from Magento Sites Google Tag Manager Skimmer
  • Malware

Hackers Exploit Google Tag Manager to Steal Credit Card Data from Magento Sites

Do Son February 9, 2025 0

Discover the importance of securing your website from credit card skimming attacks. Explore an incident with Google Tag Manager and learn how to stay safe.

CVE-2025-0674 (CVSS 9.8) & CVE-2025-0675: CISA Warns of Critical Elber Flaws – PoC Available, No Patch CVE-2025-0674 (CVSS 9.8) & CVE-2025-0675
  • Vulnerability

CVE-2025-0674 (CVSS 9.8) & CVE-2025-0675: CISA Warns of Critical Elber Flaws – PoC Available, No Patch

Do Son February 9, 2025 0

Critical vulnerabilities in Elber communications equipment: Learn about the urgent warning from CISA and the potential risks of CVE-2025-0674 and CVE-2025-0675.

Threat Actors Exploit SimpleHelp Vulnerabilities to Deploy Sliver Backdoor Quest KACE Vulnerability CVE-2025-32975 FortiGate SSO Bypass, Active Exploitation GoAnywhere RCE, Storm-1175 Cisco VPN RCE, ASA Zero-Day TinyColor Supply Chain Attack SK Telecom, data breach Erlang/OTP RCE, OT Network Security Ivanti CSA Attacks WordPress RCE, Theme Vulnerability
  • Cyber Security
  • Vulnerability

Threat Actors Exploit SimpleHelp Vulnerabilities to Deploy Sliver Backdoor

Do Son February 9, 2025 0

Field Effect reveals a cyberattack that used newly discovered SimpleHelp RMM software vulnerabilities to deploy the Sliver backdoor and establish persistence mechanisms.

CVE-2024-48510 (CVSS 9.8): Critical Flaw in ABB Drive Composer Enables File System Access ABB T-MAC Plus vulnerabilities terminal system flaws ABB OPTIMAX Vulnerability CVE-2025-14510 ABB Edgenius Auth Bypass, Critical RCE ABB, ASPECT BMS CVE-2024-48841, CVE-2024-48849, and CVE-2024-48852 CVE-2024-48510
  • Vulnerability

CVE-2024-48510 (CVSS 9.8): Critical Flaw in ABB Drive Composer Enables File System Access

Do Son February 9, 2025 0

Discover the critical path traversal vulnerability (CVE-2024-48510) in ABB Drive Composer software. Find out the potential consequences and security risks.

Publicly Disclosed ASP.NET Machine Keys Used in Code Injection Attacks ViewState code injection attacks
  • Cyber Security

Publicly Disclosed ASP.NET Machine Keys Used in Code Injection Attacks

Do Son February 9, 2025 0

Discover the dangers of code injection attacks in web applications. Explore the vulnerability of ViewState and how to prevent remote code execution.
CVE-2025-0896 (CVSS 9.8): Orthanc DICOM Server Flaw Exposes Medical Images to Unauthorized Access CVE-2025-0896
  • Vulnerability

CVE-2025-0896 (CVSS 9.8): Orthanc DICOM Server Flaw Exposes Medical Images to Unauthorized Access

Do Son February 9, 2025 0

Discover the CVE-2025-0896 flaw in Orthanc, a popular DICOM server, which could allow unauthorized access to medical images and patient data.

Abyss Locker Ransomware: Inside the Stealthy Network Intrusions and Destructive Attacks INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Malware
  • Vulnerability

Abyss Locker Ransomware: Inside the Stealthy Network Intrusions and Destructive Attacks

Do Son February 9, 2025 0

Get insights into the cyber onslaught of Abyss Locker. Sygnia's report uncovers their calculated attacks and the methods they use to cripple organizations.

Massive Indian Mobile Banking Heist Uncovered: FatBoyPanel’s Trojan Network Exposes 50,000 Users’ Data FatBoyPanel
  • Data Leak
  • Malware

Massive Indian Mobile Banking Heist Uncovered: FatBoyPanel’s Trojan Network Exposes 50,000 Users’ Data

Do Son February 9, 2025 0

Uncover the shocking details of the FatBoyPanel mobile banking malware operation in India. Find out how threat actors compromised sensitive financial and personal data.

CVE-2025-24786 (CVSS 10) & CVE-2025-24787: Critical WhoDB Vulnerabilities CVE-2025-24786 & CVE-2025-24787
  • Vulnerability

CVE-2025-24786 (CVSS 10) & CVE-2025-24787: Critical WhoDB Vulnerabilities

Do Son February 9, 2025 0

Critical security vulnerabilities discovered in WhoDB - CVE-2025-24786 (CVSS 10.0) and CVE-2025-24787 (CVSS 8.6). Protect your sensitive data and system files.

Flesh Stealer Malware Targets Browsers and Cryptocurrency Wallets Flesh Stealer
  • Malware

Flesh Stealer Malware Targets Browsers and Cryptocurrency Wallets

Do Son February 9, 2025 0

Discover Flesh Stealer, a sophisticated malware designed to steal sensitive information from web browsers and cryptocurrency wallets.

Sophos Uncovers Rising Threat of SVG-Based Phishing Attacks SVG Phishing Attacks
  • Cyber Security

Sophos Uncovers Rising Threat of SVG-Based Phishing Attacks

Do Son February 8, 2025 0

Beware of SVG phishing attacks. Learn how attackers are using SVG files to bypass anti-spam protections and distribute malicious links.
CVE-2024-51547 (CVSS 9.8): Hard-Coded Credentials in ABB ASPECT CVE-2024-51547
  • Vulnerability

CVE-2024-51547 (CVSS 9.8): Hard-Coded Credentials in ABB ASPECT

Do Son February 8, 2025 0

Stay informed about the critical hard-coded credentials vulnerability (CVE-2024-51547) in ABB's ASPECT Energy Management System and the potential risks it poses.

Malicious Cisco AnyConnect Ads Target Users with NetSupport RAT shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Malware

Malicious Cisco AnyConnect Ads Target Users with NetSupport RAT

Do Son February 8, 2025 0

Beware of a new malvertising campaign using fake Cisco AnyConnect installers. Learn how attackers are distributing the NetSupport RAT Trojan.

Lazarus Group Lures Victims with Fake LinkedIn Job Offers, Warns Bitdefender North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Cyber Security

Lazarus Group Lures Victims with Fake LinkedIn Job Offers, Warns Bitdefender

Do Son February 7, 2025 0

Beware of cyber espionage on LinkedIn! Lazarus Group targets professionals with fake job offers and sophisticated malware.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.