Skip to content
September 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security

Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth

Do Son November 21, 2024 0
Read More Read more about Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth
Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Cyber Security
  • Vulnerability

Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled

Do Son November 21, 2024 0
Read More Read more about Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled
CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Vulnerability

CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved

Do Son November 21, 2024 0
Read More Read more about CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved
Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security

Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report

Do Son November 21, 2024 0
Read More Read more about Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report
Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure Volt Typhoon APT group
  • Cyber Security
  • Vulnerability

Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure

Do Son November 21, 2024 0
Read More Read more about Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure
CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability

CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs

Do Son November 21, 2024 0
Read More Read more about CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs
Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack APT Bitter - Sync-Scheduler
  • Cyber Security

Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack

Do Son November 21, 2024 0
Read More Read more about Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack
MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem C2 interaction with an infected system
  • Malware

MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem

Do Son November 21, 2024 0
Read More Read more about MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem
Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation ahost.exe DLL Sideloading Signed Application Abuse PS1Bot, malware ransomware attacks bill
  • Malware

Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation

Do Son November 21, 2024 0
Read More Read more about Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation
Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability

Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning

Do Son November 21, 2024 0
Read More Read more about Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning
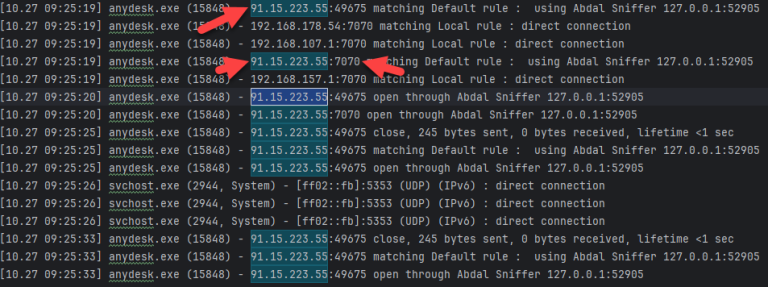
CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published CVE-2024-52940
  • Vulnerability

CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published

Do Son November 21, 2024 0
Read More Read more about CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published
PDFFlex: Analyzing PUA Persistence and Evasion Techniques PUA Persistence
  • Malware

PDFFlex: Analyzing PUA Persistence and Evasion Techniques

Do Son November 21, 2024 0
Read More Read more about PDFFlex: Analyzing PUA Persistence and Evasion Techniques
CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution Ingress-Nginx Vulnerability Kubernetes RCE Vulnerability CVE-2025-9708 Kubernetes Security, Image Builder Vulnerability CVE-2024-10220 - OPA Gatekeeper Bypass
  • Vulnerability

CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution

Do Son November 20, 2024 0
Read More Read more about CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution
Phishing Scheme Nets Millions in Cryptocurrency, Five Charged StrelaStealer malware attacks - Phishing Scheme
  • Cyber Security

Phishing Scheme Nets Millions in Cryptocurrency, Five Charged

Do Son November 20, 2024 0
Read More Read more about Phishing Scheme Nets Millions in Cryptocurrency, Five Charged
CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director CVE-2024-42450 - Versa Director
  • Vulnerability

CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director

Do Son November 20, 2024 0
Read More Read more about CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director
Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech Earth Kasha - LODEINFO
  • Cyber Security
  • Malware

Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech

Do Son November 20, 2024 0
Read More Read more about Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech
2024 CWE Top 25: Critical Software Weaknesses Revealed 2024 CWE Top 25
  • Vulnerability

2024 CWE Top 25: Critical Software Weaknesses Revealed

Do Son November 20, 2024 0
Read More Read more about 2024 CWE Top 25: Critical Software Weaknesses Revealed
WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts Apple Foldable, iPhone Fold WorkflowKit, CVE-2024-27821 Zero-Days
  • Vulnerability

WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts

Do Son November 20, 2024 0
Read More Read more about WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts
FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Malware

FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol

Do Son November 20, 2024 0
Read More Read more about FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol
LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms PromptMink Campaign AI Agent Deception LIMINAL PANDA UNC1549 DLL Hijacking, VDI Breakout
  • Cyber Security

LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms

Do Son November 20, 2024 0
Read More Read more about LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms
Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution Veritas Enterprise Vault server CVE-2025-27816
  • Vulnerability

Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution

Do Son November 20, 2024 0
Read More Read more about Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution
New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming Exploited VMware
  • Cyber Security

New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming

Do Son November 20, 2024 0
Read More Read more about New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-94130CVSS 9.3
    Joomla Extension - joomlaboat.com - Unauthenticated SQL injection in YouTube Gallery extension < 5.7.3 - An SQL injection...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97161CVSS 9.2
    Joomla Extension - lomart.fr - Various path traversal / file access vectors in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-97163CVSS 10.0
    Joomla Extension - lomart.fr - Unauthenticated remote code installation in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-94132CVSS 9.5
    Joomla Extension - acymailing.com - Remote Code Execution vulnerability in mailbox action feature in AcyMailing Enterprise extension <...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97160CVSS 9.4
    Joomla Extension - lomart.fr - Authenticated, privileged PHP command injection in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-100835CVSS 9.1
    Contrast before 1.16.0 is susceptible to remote attestation relay attacks. Contrast accepted any TEE attestation report that verified...
    📅 Updated: Sep 27, 2026
  • CVE-2026-100721CVSS 9.5
    vm2 before 3.12.2 contains an authorization bypass in the NodeVM external-module resolver. When an embedder configures `require.external` with...
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.