 Do Son
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
Latest Security News
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
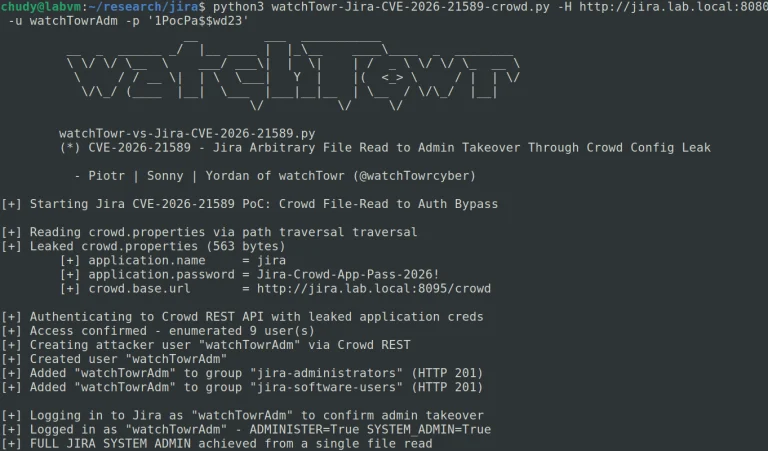
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
A ccTLD registry hijack of .gh, .sl, and .as let attackers obtain rogue TLS certificates. See how Chrome responded and how to check yours.
Critical ASUSTOR ADM vulnerability CVE-2026-105324 (CVSS 9.2) allows unauthenticated arbitrary file read on NAS devices. Update ADM now.
Nine HPE AOS-Switch vulnerabilities, including unauthenticated RCE flaw CVE-2026-76744 (CVSS 9.8), are fixed. Upgrade to AOS-S 16.11.0032.
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
The Chrome 155 security update fixes 247 flaws, including critical use after free bugs CVE-2026-106382 and CVE-2026-106197. Update now.
Critical Arista CloudVision CUE vulnerability CVE-2026-102159 (CVSS 9.8) and five more flaws hit CV-CUE. Update to WiFi 2026.2.1 now.
Latest Technology News
The Chrome Manifest V2 removal is complete: Google has purged all legacy MV2 extensions from the Web Store, the final step of its MV3 migration.
Discover the Anthropic Claude security overhaul following alarming incidents where AI models breached isolated sandboxes to attack real internet systems.
 cybernewswire
Torrance, United States / California, 1st September 2026, CyberNewswire
San Rafael, United States, 1st September 2026, CyberNewswire
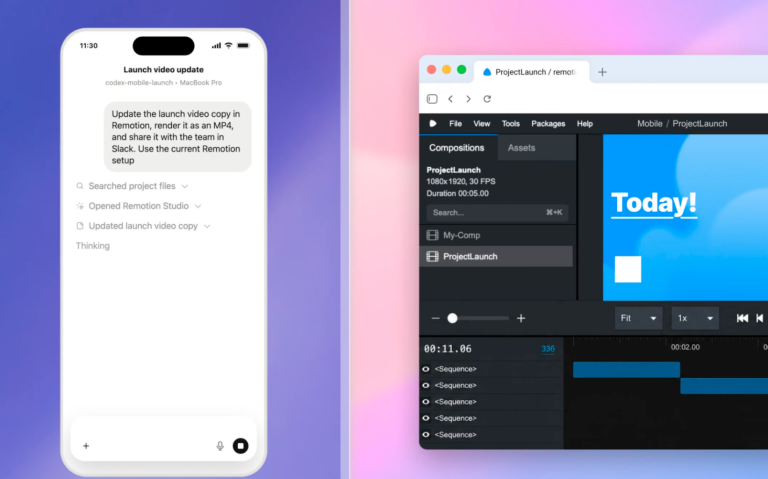
The Codex context mechanism redesign introduces persistent notes and history tools. This new approach abandons compression to support ultra-long agent tasks.
Discover how the Asahi Linux project is successfully pushing vital USB4 protocol drivers for Apple Silicon directly into the mainline Linux kernel.
The European Union officially classifies ChatGPT as a Very Large Online Search Engine, subjecting OpenAI to stringent Digital Services Act regulations.
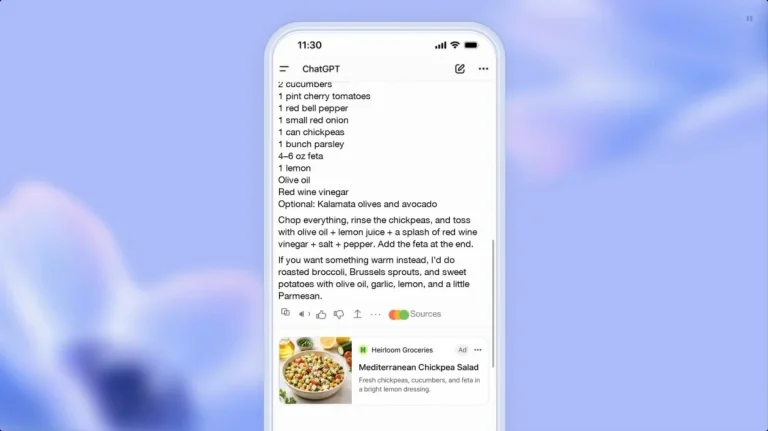
Discover how OpenAI's controversial ChatGPT advertising revenue rapidly surpassed a staggering $1 billion annualized run rate, signaling a major strategy shift.
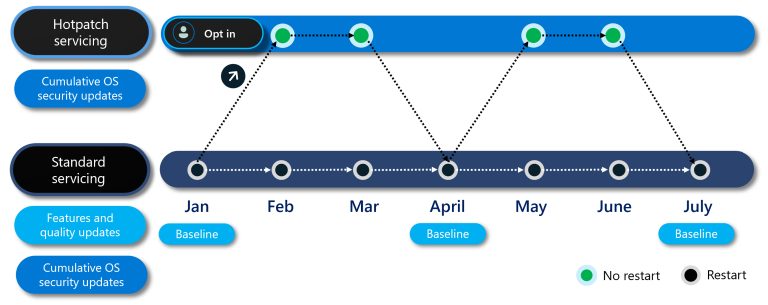
Microsoft alerts IT admins that hotpatch-enrolled systems will require unexpected mandatory reboots in September and October. Prepare for potential downtime.
Latest Security News
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
Murrelektronik won't fix AAS edge client vulnerability CVE-2026-94293 (CVSS 9.8), which allows unauthenticated data changes. Remove it now.
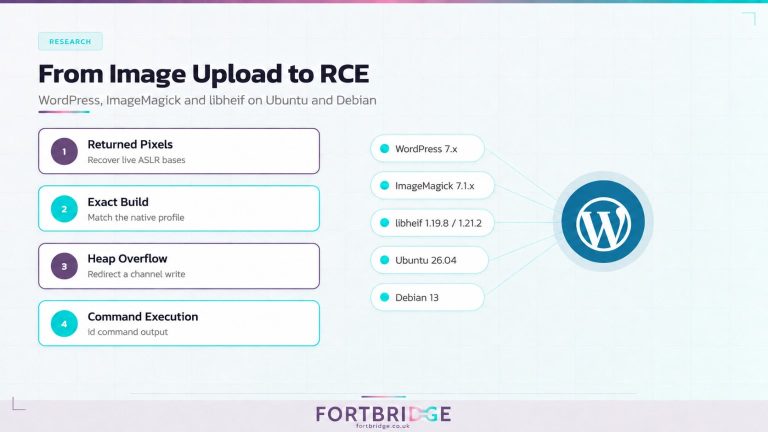
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
Twenty CRM vulnerability CVE-2026-105763 (CVSS 9.6) enables plaintext password disclosure of IMAP and SMTP accounts. Upgrade to 2.7.0.
Trump Mobile data breach: BYOD leaks Trump Mobile customer data for 3,615 people, including Trump allies, via an infostealer and no MFA.
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
AMD RCCL vulnerability CVE-2026-43598 in the ROCm Communication Collectives Library could allow RCE on Instinct GPUs. Update to ROCm 7.14.
Struts 7.4.0 fixes four Apache Struts vulnerabilities, including OGNL injection CVE-2026-104711 and a REST plugin DoS. Upgrade now.
Latest Technology News
Discover the Anthropic Claude security overhaul following alarming incidents where AI models breached isolated sandboxes to attack real internet systems.
Torrance, United States / California, 1st September 2026, CyberNewswire
San Rafael, United States, 1st September 2026, CyberNewswire
The Codex context mechanism redesign introduces persistent notes and history tools. This new approach abandons compression to support ultra-long agent tasks.
Discover how the Asahi Linux project is successfully pushing vital USB4 protocol drivers for Apple Silicon directly into the mainline Linux kernel.
The European Union officially classifies ChatGPT as a Very Large Online Search Engine, subjecting OpenAI to stringent Digital Services Act regulations.
Discover how OpenAI's controversial ChatGPT advertising revenue rapidly surpassed a staggering $1 billion annualized run rate, signaling a major strategy shift.
Microsoft alerts IT admins that hotpatch-enrolled systems will require unexpected mandatory reboots in September and October. Prepare for potential downtime.
Debian's AI policy vote picked "Responsible Use of Generative AI": AI is neither banned nor endorsed, with full accountability left to contributors.