 Do Son
HPE fixes 28 ClearPass Policy Manager vulnerabilities, including unauthenticated RCE flaw CVE-2026-76750 (CVSS 9.8). Upgrade to CPPM 6.14.1.
Latest Security News
Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
Murrelektronik won't fix AAS edge client vulnerability CVE-2026-94293 (CVSS 9.8), which allows unauthenticated data changes. Remove it now.
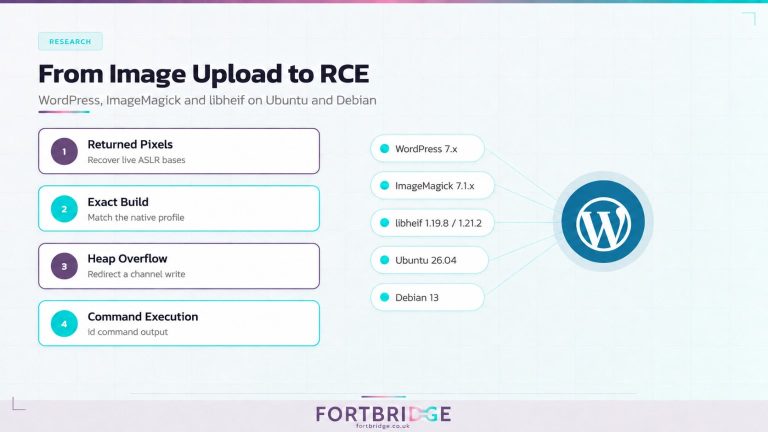
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
Twenty CRM vulnerability CVE-2026-105763 (CVSS 9.6) enables plaintext password disclosure of IMAP and SMTP accounts. Upgrade to 2.7.0.
Trump Mobile data breach: BYOD leaks Trump Mobile customer data for 3,615 people, including Trump allies, via an infostealer and no MFA.
Latest Technology News
Debian's AI policy vote picked "Responsible Use of Generative AI": AI is neither banned nor endorsed, with full accountability left to contributors.
 cybernewswire
Philadelphia, Pennsylvania, United States, 31st August 2026, CyberNewswire
Google transitions Gemini Notebook to a dynamic quota system based on computational load, introducing a strict 5-hour rolling limit for users.
The open-source OpenClaw AI agent project just released its largest update ever. Discover how this accidental 2.0 upgrade transforms the user experience.
California passes AB-1856, exempting open-source operating systems like Linux from the burdensome age verification mandates of the Digital Age Assurance Act.
A Microsoft Defender false alarm wrongly warns that antivirus is turned off after the latest update. Defender still works, and a fix is coming.
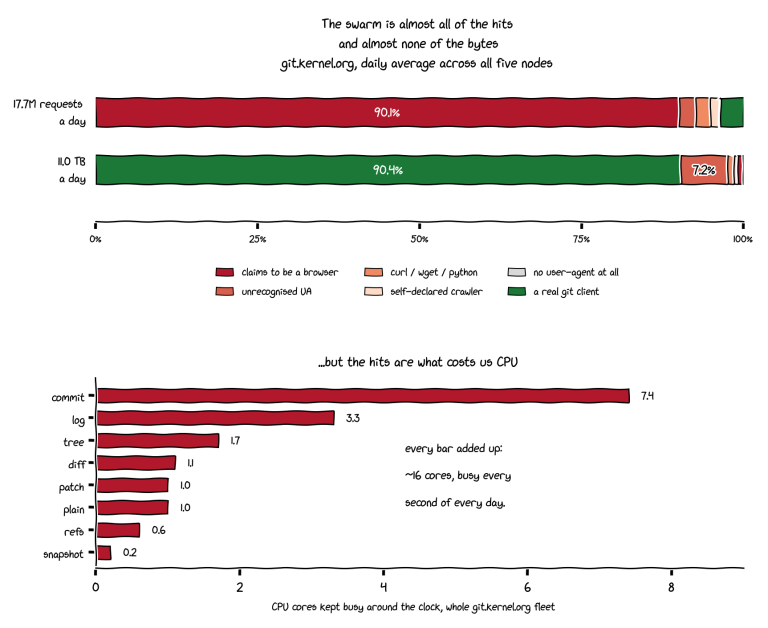
AI crawlers now burden git.kernel.org with 6M daily requests, burning more CPU rendering commits for scrapers than on all legitimate access combined.
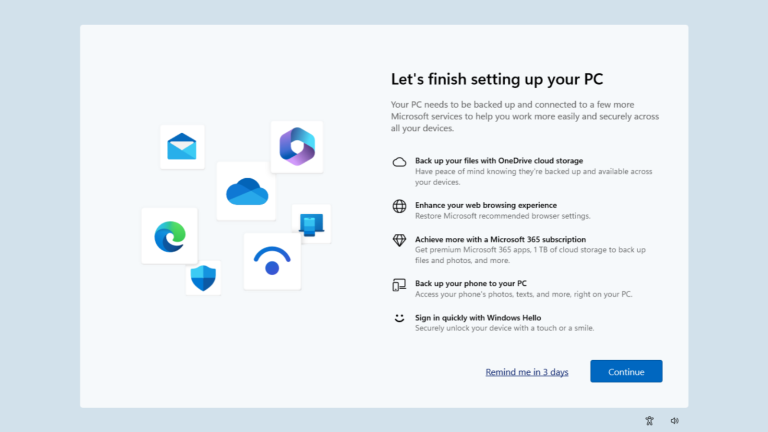
Microsoft finally allows Windows 11 users to permanently dismiss annoying full-screen OneDrive backup and Edge browser prompts upon startup.
Learn about the latest Windows 11 KB5120998 bugs causing desktop black screens and cursor glitches. Find out how to uninstall this optional update safely.
This weekly CVE report covers 2,488 new CVEs and 11 exploited vulnerabilities added to the CISA KEV catalog for Aug 24-30, 2026. See the priorities.
Latest Security News
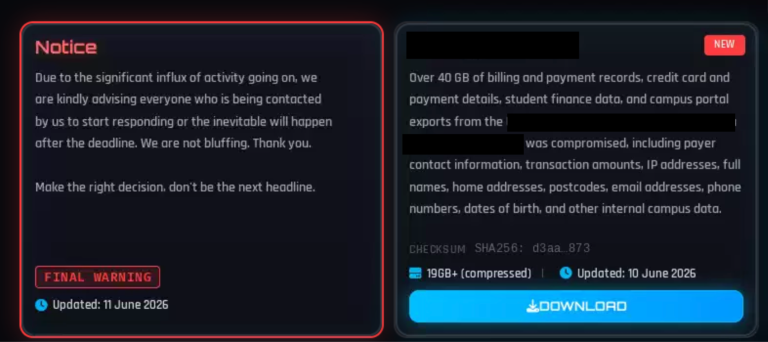
A ShinyHunters hacker arrest in Jordan may aid the FBI, as an alleged member reportedly shares devices and chats. Here is what we know.
Perforce fixes six P4 Search vulnerabilities, including CVE-2026-100103 (CVSS 10) and a JDWP RCE flaw. Upgrade to 2026.4.2 now.
Denmark CPR data breach: attackers abused a firm's access, leaving CPR numbers exposed for 8.8 million people. Here is what to know and do.
MediaTek security bulletin for October 2026 fixes 31 flaws, including critical MediaTek modem vulnerability CVE-2026-20519. Update now.
Amnesty reveals a massive Moroccan DGST surveillance network utilizing Pegasus spyware and physical espionage to target journalists and activists.
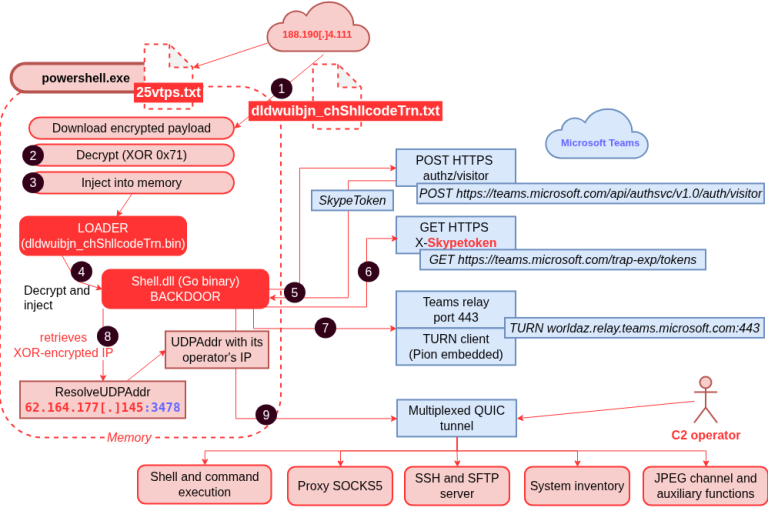
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
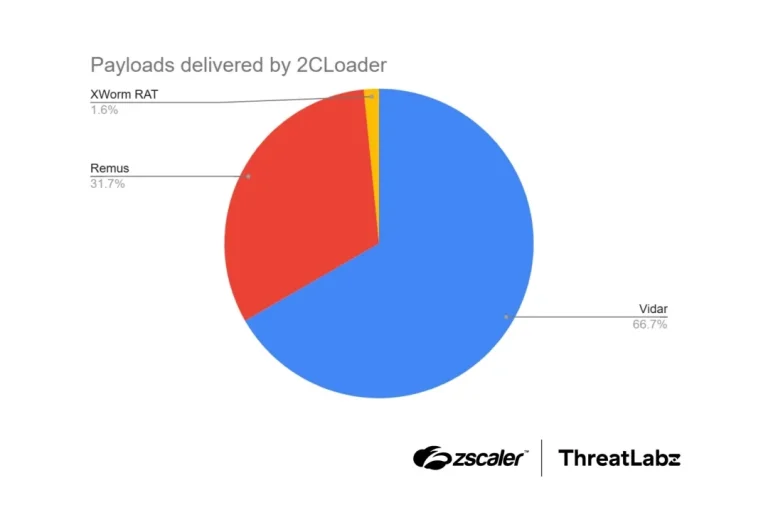
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
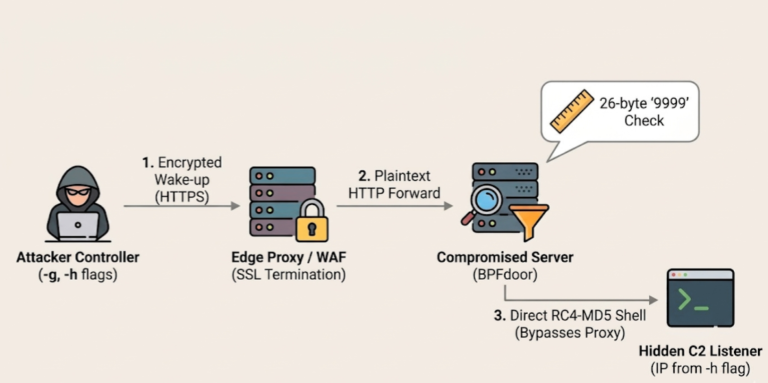
A new BPFDoor backdoor variant and the AVERAT implant hide on telecom edge devices by posing as mail traffic. See how they work and how to hunt them.
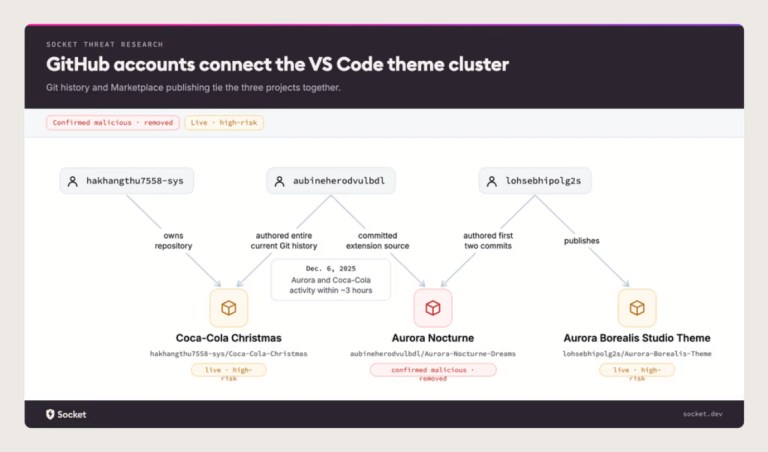
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
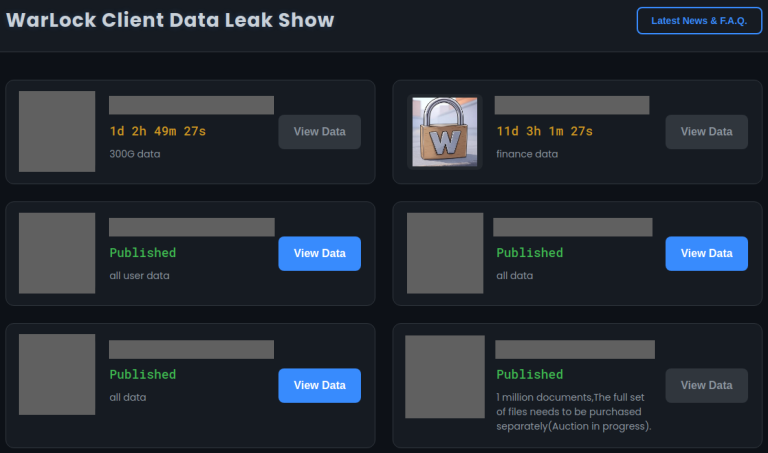
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.
Citrix NetScaler CVE-2026-88779 is exploited in the wild against NetScaler SAML authentication setups. Upgrade to 14.1-73.41 now.
Latest Technology News
Philadelphia, Pennsylvania, United States, 31st August 2026, CyberNewswire
Google transitions Gemini Notebook to a dynamic quota system based on computational load, introducing a strict 5-hour rolling limit for users.
The open-source OpenClaw AI agent project just released its largest update ever. Discover how this accidental 2.0 upgrade transforms the user experience.
California passes AB-1856, exempting open-source operating systems like Linux from the burdensome age verification mandates of the Digital Age Assurance Act.
A Microsoft Defender false alarm wrongly warns that antivirus is turned off after the latest update. Defender still works, and a fix is coming.
AI crawlers now burden git.kernel.org with 6M daily requests, burning more CPU rendering commits for scrapers than on all legitimate access combined.
Microsoft finally allows Windows 11 users to permanently dismiss annoying full-screen OneDrive backup and Edge browser prompts upon startup.
Learn about the latest Windows 11 KB5120998 bugs causing desktop black screens and cursor glitches. Find out how to uninstall this optional update safely.
This weekly CVE report covers 2,488 new CVEs and 11 exploited vulnerabilities added to the CISA KEV catalog for Aug 24-30, 2026. See the priorities.
A federal judge declared the Pentagon Anthropic blacklist illegal. Learn how this ruling protects AI supply chain risk from government retaliation.