Skip to content
September 24, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Cloudflare Blocks Critical WordPress wp2shell Vulnerability Cloudflare firewall blocking the critical WordPress wp2shell vulnerability and RCE attacks
  • Vulnerability Report

Cloudflare Blocks Critical WordPress wp2shell Vulnerability

Do Son July 18, 2026 0
Read More Read more about Cloudflare Blocks Critical WordPress wp2shell Vulnerability
Microsoft Ends OneDrive Support for Windows 10 Microsoft ending OneDrive updates and support for Windows 10 lifecycle
  • Technology

Microsoft Ends OneDrive Support for Windows 10

Do Son July 18, 2026 0
Read More Read more about Microsoft Ends OneDrive Support for Windows 10
Ubuntu Pro Client Flaw CVE-2026-11386 Allows Arbitrary Code Execution With Root Privileges Ubuntu Pro Client vulnerability CVE-2026-11386 APT source injection arbitrary code execution root privileges
  • Vulnerability Report

Ubuntu Pro Client Flaw CVE-2026-11386 Allows Arbitrary Code Execution With Root Privileges

Do Son July 18, 2026 0
Read More Read more about Ubuntu Pro Client Flaw CVE-2026-11386 Allows Arbitrary Code Execution With Root Privileges
WordPress Pre-Auth RCE CVE-2026-63030: Vulnerability Details and PoC Exploit Code Now Public WordPress pre-auth RCE CVE-2026-63030 REST batch route confusion SQL injection public PoC
  • Vulnerability Report

WordPress Pre-Auth RCE CVE-2026-63030: Vulnerability Details and PoC Exploit Code Now Public

Do Son July 18, 2026 0
Read More Read more about WordPress Pre-Auth RCE CVE-2026-63030: Vulnerability Details and PoC Exploit Code Now Public
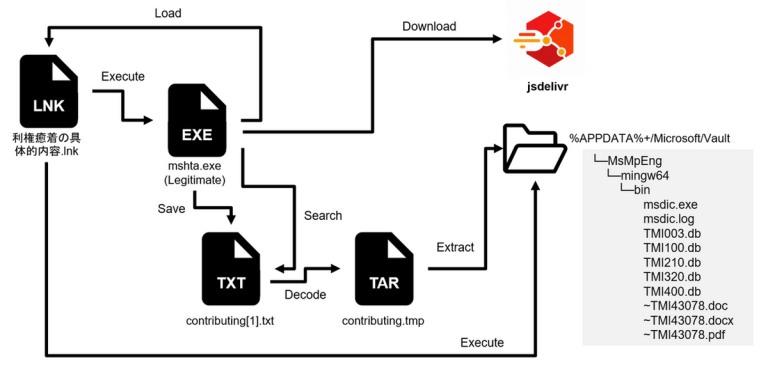
APT-C-60 Attacks Target Japan With SpyGlace Malware APT-C-60 attacks on Japan using LNK files and legitimate services to deploy SpyGlace malware
  • Cybercriminals

APT-C-60 Attacks Target Japan With SpyGlace Malware

Do Son July 18, 2026 0
Read More Read more about APT-C-60 Attacks Target Japan With SpyGlace Malware
CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation cheapsslweb-ssl-provider
  • Technique

CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation

Do Son July 18, 2026 0
Read More Read more about CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation
Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions certera-ssl-provider
  • Technique

Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions

Do Son July 18, 2026 0
Read More Read more about Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions
GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins GoldPickaxe banking Trojan stealing biometric data and lock screen credentials from an Android phone
  • Malware

GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins

Do Son July 17, 2026 0
Read More Read more about GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins
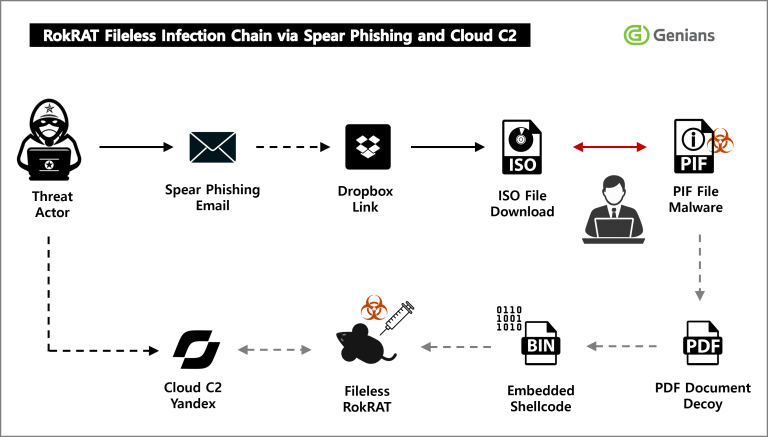
RokRAT Malware Hides in Fake PDF Files to Spy on Academics APT37 RokRAT malware delivered via fake PDF in Operation Capsule Vault spear-phishing
  • Malware

RokRAT Malware Hides in Fake PDF Files to Spy on Academics

Do Son July 17, 2026 0
Read More Read more about RokRAT Malware Hides in Fake PDF Files to Spy on Academics
CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace Kyverno vulnerability CVE-2026-54523 privilege escalation to admin in any namespace including kube-system
  • Vulnerability Report

CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace

Do Son July 17, 2026 0
Read More Read more about CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace
Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges Citrix Secure Access vulnerability CVE-2026-53565 privilege escalation illustration
  • Vulnerability Report

Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges

Do Son July 17, 2026 0
Read More Read more about Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges
Misconfigured Server Exposes Three AiTM Phishing Operators Open directory exposing three AiTM phishing operators using Evilginx MFA bypass tooling
  • Cybercriminals

Misconfigured Server Exposes Three AiTM Phishing Operators

Do Son July 17, 2026 0
Read More Read more about Misconfigured Server Exposes Three AiTM Phishing Operators
292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users Fake GitHub repositories BoryptGrab infostealer attack chain diagram
  • Malware

292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users

Do Son July 17, 2026 0
Read More Read more about 292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users
EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA Google DMA ruling opening Android to third-party AI assistants and search data sharing
  • Technology

EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA

Do Son July 17, 2026 0
Read More Read more about EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA
Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution Gemini Notebook rebrand of NotebookLM with native code execution
  • Technology

Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution

Do Son July 17, 2026 0
Read More Read more about Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution
Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network Chrome security update 150.0.7871.128 critical use-after-free vulnerabilities CameraCapture GPU Network
  • Vulnerability Report

Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network

Do Son July 17, 2026 0
Read More Read more about Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network
Supply Chain Trojan Targets Software Developers Through Project Files Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Malware

Supply Chain Trojan Targets Software Developers Through Project Files

Do Son July 17, 2026 0
Read More Read more about Supply Chain Trojan Targets Software Developers Through Project Files
CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras TP-Link Kasa vulnerability CVE-2026-9770 information disclosure flaw on EC70 and EC71 cameras
  • Vulnerability Report

CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras

Do Son July 17, 2026 0
Read More Read more about CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras
CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation CISA KEV catalog adds three actively exploited FortiSandbox and SharePoint vulnerabilities
  • Vulnerability Report

CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation

Do Son July 17, 2026 0
Read More Read more about CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation
7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data 7-Zip vulnerability CVE-2026-14266 XZ decompression heap buffer overflow remote code execution
  • Vulnerability Report

7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data

Do Son July 16, 2026 0
Read More Read more about 7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data
Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed Grok Build open source release on GitHub with data sharing disabled
  • Technology

Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed

Do Son July 16, 2026 0
Read More Read more about Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed
CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI Red Hat OpenShift AI blind SSRF flaw CVE-2026-15378 in guardrails-detectors component
  • Vulnerability Report

CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI

Do Son July 16, 2026 0
Read More Read more about CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93952CVSS 10.0
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-32996CVSS 7.3
    A vulnerability in Veeam Agent for Microsoft Windows allows for Local Privilege Escalation.
    Admin intel📅 Updated: Sep 22, 2026
  • CVE-2026-7273CVSS 8.8
    A stack-based buffer overflow vulnerability in the CGI program of Zyxel GS1900-48HPv2 firmware versions through 2.90(ABTQ.1)C0 could allow a...
    CISA KEV📅 Added to KEV: Sep 21, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-97360CVSS 10.0
    HFS2 version 2.4.0 and earlier contains an unauthenticated arbitrary file access vulnerability that allows unauthenticated attackers to read,...
    📅 Updated: Sep 24, 2026
  • CVE-2026-97359CVSS 10.0
    HFS2 version 2.4.0 and earlier contains a template injection vulnerability in the multipart upload handler that allows unauthenticated...
    📅 Updated: Sep 24, 2026
  • CVE-2026-88405CVSS 9.8
    A remote code execution (RCE) vulnerability in the RemoteRegisterFunctionService function (/remote/remote-register-function.service.ts) of Univer v1.0.0-alpha.2 allows attackers to execute...
    📅 Updated: Sep 24, 2026
  • CVE-2026-78312CVSS 9.1
    Path Traversal in DIAEnergie. This issue affects DIAEnergie: before 1.11.00.022.
    📅 Updated: Sep 24, 2026
  • CVE-2026-67827CVSS 9.8
    Incorrect Access Control in the HTTP API module in ZLMediaKit commit 9fd5152 allows remote attackers to achieve Remote...
    📅 Updated: Sep 24, 2026
  • CVE-2026-78308CVSS 9.8
    Improper Authentication vulnerability in DIAEnergie allows Authentication Bypass. This issue affects DIAEnergie: before 1.11.00.022.
    📅 Updated: Sep 24, 2026
  • CVE-2026-36469CVSS 9.1
    CuteNews v.2.1.2 is vulnerable to Server-Side Request Forgery (SSRF) in core/modules/media.php -- upload_from_inet (Media Manager's "Upload by URL"...
    📅 Updated: Sep 24, 2026
  • CVE-2026-19072CVSS 9.9
    Velociraptor stores the compiled VQL in the hunt object internally to avoid having to recompile the artifacts for...
    📅 Updated: Sep 24, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.