
 Do Son
Researchers at Proofpoint Threat Research have identified a previously unknown cyber-espionage group, dubbed UNK_SmudgedSerpent, which has been...
Latest news

Google has released a Stable Channel Update for Chrome Desktop (version 142.0.7444.134/.135) for Windows, macOS, and Linux...

The Cybersecurity and Infrastructure Security Agency (CISA) has issued a critical advisory detailing three vulnerabilities in the...

In collaboration with the Georgian CERT, researchers from Bitdefender have uncovered a new wave of cyber-espionage activity...

NVIDIA has released an important software security update for the NVIDIA App on Windows systems, addressing a...

The JPCERT/CC Incident Response Group, led by malware analyst Yuma, has published a detailed report on a...

The Cybersecurity and Infrastructure Security Agency (CISA) has issued an advisory warning about a critical vulnerability affecting...

OpenAI’s popular AI-powered video generation tool, Sora, has officially launched its Android version on November 4, 2025,...

There have long been rumors suggesting that Apple is preparing to launch a more affordable line of...

Earlier, a technology company attempted to send NVIDIA AI accelerator cards into space, conducting tests powered by...

CVE-2024-32962, carries the highest severity score of 10 on the Common Vulnerability Scoring System (CVSS), indicating its critical nature
Dropbox has confirmed a security breach within its Dropbox Sign (formerly HelloSign) service, exposing customer data

Interestingly, there is a noted overlap between Cuttlefish and a previously identified malware cluster known as HiatusRat

Security researchers at SentinelOne have identified new Adload variants that successfully evade Apple's detection mechanisms.

Dirty Stream exploits path traversal vulnerabilities when applications share data using Android's ContentProvider components

HPE Aruba Networking announced a comprehensive update to its ArubaOS software, targeting multiple critical vulnerabilities

Goldoon botnet is ruthlessly exploiting a CVE-2015-2051 vulnerability in D-Link devices to commandeer them for malicious activities

TargetCompany ransomware group is actively deploying Mallox ransomware alongside other malicious tools to exploit vulnerable database servers.

CVE-2024-29010 & CVE-2024-29011 could be exploited by attackers to gain unauthorized access to sensitive data and bypass authentication mechanisms

Cisco Talos have unveiled a coordinated threat actor campaign dubbed "ArcaneDoor," targeting government-owned network devices globally

A comprehensive report has uncovered the money laundering tactics employed by the North Korean hacking collective, Lazarus Group

CVE-2024-27790 could have potentially enabled attackers to gain access to records they should not have been authorized to see or modify.
CISA added a recently patched Microsoft vulnerability (CVE-2024-29988) to its Known Exploited Vulnerabilities (KEV) catalog

Security researchers at Zscaler have uncovered a new anti-analysis feature in recent iterations of the Zloader malware

CVE-2024-2912 vulnerability lies in the way the software handles data, allowing attackers to run arbitrary code on servers running BentoML

Wpeeper is a backdoor Trojan with typical features such as collecting sensitive information from devices, managing files and directories

IBM has announced its definitive agreement to acquire HashiCorp Inc., a leader in multi-cloud infrastructure automation

In the latest wave of tech-sector layoffs, Google has made significant cuts to teams working on key development tools like Flutter, Python

A serious security vulnerability (CVE-2024-32656) foun in Ant Media Server, a popular streaming solution used by thousands of organizations
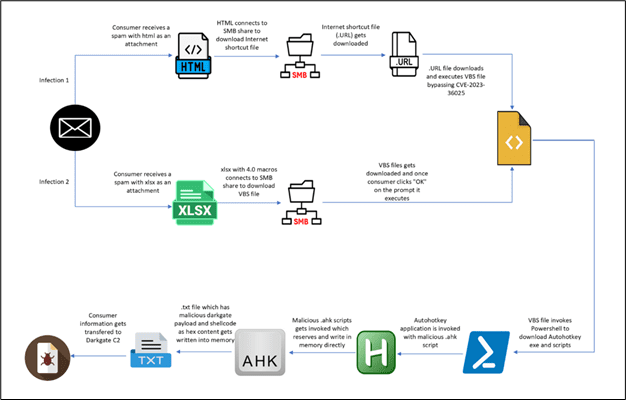
DarkGate, identified as a Remote Access Trojan (RAT), poses a formidable threat due to its array of functionalities including data theft

Researchers from HiddenLayer have discovered a significant vulnerability in the R programming language, tracked as CVE-2024-27322

Threat research team has identified a sophisticated new Remote Access Trojan (RAT) targeting Android devices