
 Do Son
Elon Musk’s social media platform X (formerly Twitter) has announced that it will permanently retire the old...
Latest news

Tech giant Amazon is reportedly preparing for another massive round of layoffs, with plans to cut as...

Extensions are an essential component of modern browsers, enabling a wide range of functionalities such as ad...

In January 2025, the Python Software Foundation (PSF) submitted a proposal to the U.S. National Science Foundation...

Earlier, several media outlets misinterpreted and selectively quoted statements from Google’s Security Team, claiming that the data...

In its latest analysis covering the second half of 2025, researchers from Cisco Talos have revealed that...

Researchers at Kaspersky uncovered a sophisticated espionage campaign exploiting a zero-day vulnerability in Google Chrome and delivering...

Security researchers have disclosed a high-severity vulnerability, tracked as CVE-2025-10680 (CVSS 8.8), affecting OpenVPN 2.7_alpha1 through 2.7_beta1...

Cybersecurity experts at Doctor Web have identified a highly sophisticated Android backdoor hiding in maliciously modified versions...

Security researchers at Lab52 have uncovered a new campaign by the Lazarus Group, in which threat actors...

Introduction In the realm of DNS (Domain Name System) configurations, the debate between Anycast and Unicast has...

Mitel has issued a critical security patch to address a vulnerability (CVE-2024-28815) in its InAttend and CMG products

CVE-2024-23334 in the popular Python web framework aiohttp has swiftly landed on the radar of notorious ransomware operators, ShadowSyndicate

CVE-2024-27307 poses a serious security risk & could allow attackers to remotely execute malicious code within apps that rely on the library

Apache ZooKeeper, a widely used coordination service for distributed applications, has a serious security flaw, tracked as CVE-2024-23944

Phoenix Contact has issued an urgent security alert regarding multiple critical vulnerabilities discovered within the firmware of CHARX SEC
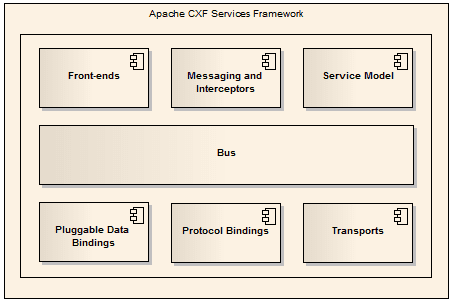
A Server-Side Request Forgery (SSRF) vulnerability, tracked as CVE-2024-28752, has been discovered in versions before 4.0.4, 3.6.3, and 3.5.8

ELVIA INFOTECH operate a 'Malware-as-a-Service' (MaaS) model, essentially providing ready-made phishing scams and malware to criminals

A severe security flaw (CVE-2024-0670, CVSS 8.8) has been exposed in Checkmk, a popular IT monitoring solution utilized by organizations

Pirated UltraEdit app harbored a secret: an unsigned third-party library, libConfigurer64.dylib, designed to usher in additional payloads surreptitiously

The popular Spring Framework has received a crucial security update. This patch addresses a high-severity flaw designated CVE-2024-22259

The most severe aspect of this advisory is that CVE-2024-0799 and CVE-2024-0800 can be chained together with devastating consequences
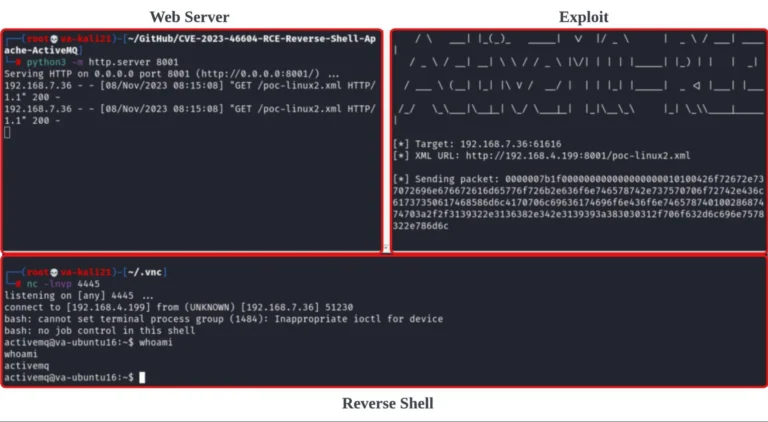
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researcher Tom Wedgbury has released a proof-of-concept (PoC) exploit, demonstrating how CVE-2024-25153 (CVSS 9.8) can be weaponized

A serious cross-site scripting (XSS) vulnerability (CVE-2024-28175, CVSS 9.0) has been discovered in Argo CD

A critical vulnerability (CVE-2024-27102) in Wings, the core component of the popular open-source Pterodactyl game server management panel

ZDI have dissected a complex DarkGate malware campaign targeting users through a 0-day flaw in Microsoft Windows SmartScreen (CVE-2024-21412)

two vulnerabilities (CVE-2024-23672 and CVE-2024-24549) could leave your servers open to crippling denial-of-service attacks.

Popular text editing software used by millions across China has become the latest target in a sophisticated cyberattack

The CVE-2024-27135 vulnerability also affects the Pulsar Broker under certain configurations, affecting versions from 2.4.0 to 3.2.0

The Xehook Stealer goes beyond traditional password and credit card theft, posing an exceptionally broad threat.

FortiOS & FortiProxy: Critical Risks (CVE-2023-42789, CVE-2023-42790) These carry the highest severity ratings (9.8 and 8.1)