
 Do Son
Google’s Threat Intelligence Group (GTIG) has uncovered a major post-exposure evolution in the operations of COLDRIVER—a Russian...
Latest news

Security researcher Jordan Jay has published an extensive technical breakdown of CVE-2025-24990, a high-severity Elevation of Privilege...

The WSO2 project has released urgent security advisories addressing two critical access control vulnerabilities—CVE-2025-9804 and CVE-2025-10611—that affect...

 cybernewswire
Wilmington, Delaware, 21st October 2025, CyberNewsWire

Computers are essential tools in both personal and professional life, handling everything from work and communication to...

Dylan Field, CEO of the design tools company Figma, has publicly stated that artificial intelligence does not...

According to the latest reports, OpenAI is introducing a new service called “ChatGPT Login,” which allows users...

JPCERT/CC and the developer MOTEX Inc. have issued an urgent advisory for a critical remote code execution...

TP-Link Systems has released a new firmware update addressing four high- and critical-severity vulnerabilities in its popular...
For many years, Apple has allowed users to quickly launch the Camera app with a simple swipe...

CVE-2024-21410 flaw offers remote, unauthenticated threat actors a pathway to privilege escalation through NTLM relay attacks.

Dubbed the "TicTacToe Dropper," this malware has demonstrated the sophistication and adaptability of modern cyber threats.

Dubbed the #MonikerLink bug, CVE-2024-21413 (CVSS 9.8) exploits a particular way Outlook processes hyperlinks

In the ever-evolving landscape of digital security, the GitHub Enterprise Server (GHES) has emerged as a cornerstone...

Revenge RAT sets its nefarious plan into motion, executing a series of malicious activities aimed at compromising system integrity
The vulnerabilities, identified as CVE-2023-20576, CVE-2023-20577, CVE-2023-20579, and CVE-2023-20587, carry a 'High' severity rating

The report delves into a specific threat actor, dubbed TropiCracked, whose nefarious exploits have targeted over 800 YouTube accounts

Armed with a diverse arsenal of malware, including the notorious AppleSeed and AlphaSeed strains, Kimsuky's tactics have evolved
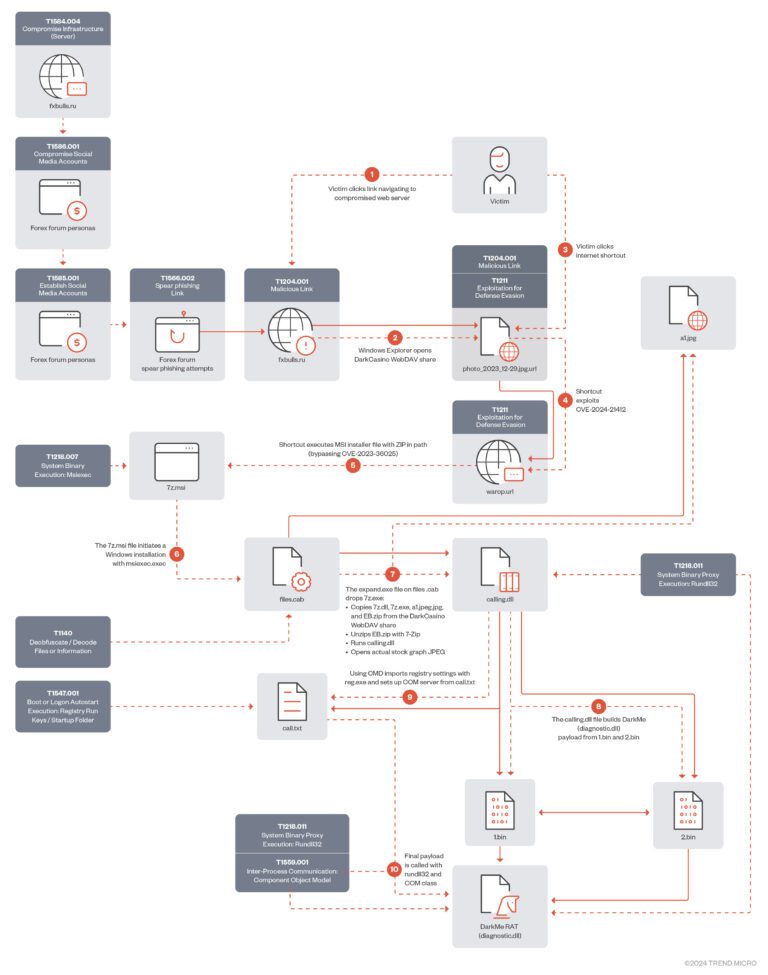
This flaw, exploited by Water Hydra, served as a linchpin in a complex 0-day attack chain, leading to a bypass of Defender SmartScreen

One notable aspect of CharmingCypress's tactics is their use of unusual social-engineering tactics in their phishing campaigns

two of these were 'zero-days' (CVE-2024-21351 and CVE-2024-21412), meaning hackers have already been exploiting them in the wild!
CVE-2024-24691 (CVSS score 9.6) could allow hackers to escalate their privileges, potentially gaining control of vulnerable systems
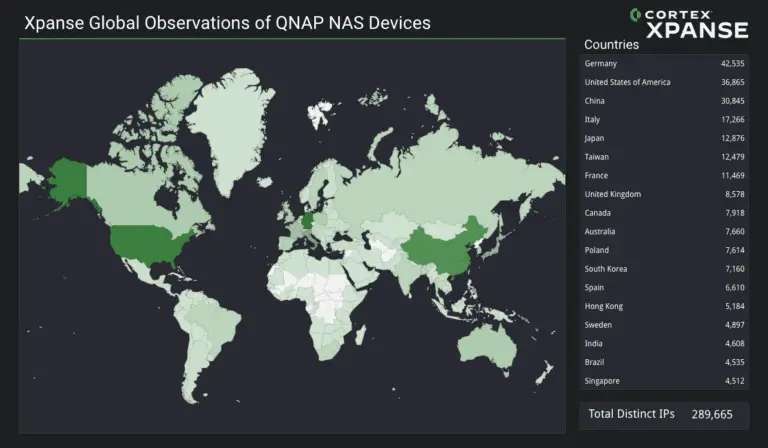
A severe zero-day vulnerability (CVE-2023-50358) has been discovered in QNAP Network Attached Storage (NAS) devices

Bumblebee malware, known for its complexity and versatility, was initially a favored payload by cybercriminals from its inception

The second "Hot News" patch targets a serious flaw (CVE-2024-22131, CVSS score 9.1) in the SAP Application Basis (ABA) layer

Industrial control systems (ICS) silently orchestrate the vital processes behind our modern world. These intricate networks of...

Introduction In today’s world of online applications, it’s important to keep our sensitive information safe, follow the...

Pikabot employs an arsenal of anti-analysis techniques, including string obfuscation, insertion of junk instructions, and anti-debug methods.
CVE-2024-25108 reveals that authorization checks within Pixelfed were insufficiently stringent, granting attackers unauthorized access

A formidable malware known as Glupteba has been lurking, evolving, and spreading its tentacles across the globe
CISA has sounded the alarm on a significant 'actively exploited' flaw in Roundcube Webmail (CVE-2023-43770)

Introduction In today’s digital age, more and more data is moving to the cloud. From personal photos...