
 Do Son
X—formerly known as Twitter—has announced the launch of a new experimental feature that changes how links open...
Latest news

According to Bloomberg journalist Mark Gurman in his latest Power On newsletter, Apple’s internal engineers have expressed...

In today’s digital age, businesses depend heavily on technology to operate efficiently, but that reliance also introduces...

The developers of Squid, the widely used open-source caching proxy for web traffic acceleration, have disclosed and...

Cybersecurity researchers at Koi Security have discovered the world’s first self-propagating malware targeting VS Code extensions on...

Researchers at SEQRITE Labs have uncovered a targeted spear-phishing campaign aimed at organizations in Russia’s automobile and...

A new joint analysis by Mandiant Threat Defense and Google Threat Intelligence Group (GTIG) has exposed a...

A new analysis from Socket has exposed a large-scale spamware operation abusing Google’s Chrome Web Store and...

FortiGuard Labs has uncovered a sophisticated cross-regional campaign that has gradually expanded from China to Taiwan, Japan,...

A new report from NTT Security Japan has spotlighted an evolved malware family known as OtterCandy, attributed...

ClamAV's developers issued critical patches addressing two vulnerabilities (CVE-2024-20328 & CVE-2024-20290) within the library
CVE-2024-20254 and CVE-2024-20255 affect devices with default configurations, amplifying the potential reach of the attacks

Raspberry Robin operates within a vast malware ecosystem, serving as an initial access broker for further malicious deployments

Glassy of EagleCloud, who found CVE-2024-20931, also provides technical details on the vulnerability, and publishes PoC code

The ramifications of falling victim to the XPhase Clipper campaign are dire, with users facing the prospect of substantial financial losses

Introduction Embracing microservices provides significant advantages for businesses and their development. They make applications more scalable, robust,...

Many of Iran's initial cyber forays consisted of repurposing old data breaches and overstating the effectiveness of their attacks

initially disclosed in a security advisory update on September 5, 2023, this vulnerability carries a chilling CVSS score of 8.8

CVE-2023-7216 could allow a remote, unauthenticated attacker to orchestrate a scenario where an unsuspecting user

A new, sophisticated attack campaign, dubbed STEADY#URSA, has emerged, casting a long shadow over the cybersecurity defenses of Ukraine's military

Assigned a CVSS score of 9.8, CVE-2024-23917 falls into the critical category, signaling a high risk of exploitability and impact

In November 2023, a new and sinister threat emerged: ResumeLooters, a malicious gang that set its sights...

APT-K-47 has quickly garnered attention for its sophisticated cyber-attack techniques, which bear similarities to other notorious APT groups
CVE-2023-6989 allowed for the inclusion of PHP files on a server by an unauthenticated attacker, leading to the execution of arbitrary PHP code

The vulnerabilities, encompassing a range of out-of-bounds write issues (CVE-2023-6229 through CVE-2023-6234 and CVE-2024-0244)

CVE-2024-0031 stands out for its potential to allow attackers to execute malicious code remotely on a victim's device
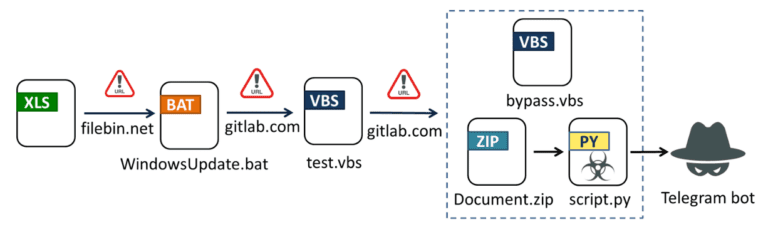
Discover how it retrieves script.py (the info-stealer), Document.zip (Python 3.11 with required libraries), and bypass.vbs (the Python executor)

CVE-2024-23108 and CVE-2024-23109 could potentially allow remote, unauthenticated attackers to execute unauthorized commands

Nevada Ransomware, identified by Resecurity’s threat research and intelligence team, is rapidly gaining notoriety for its advanced...

CVE-2024-1143 has been rated with the maximum severity score of 10.0, classifying it as Critical—the highest level of urgency.

ESET has uncovered a startling revelation: a series of Android espionage apps bundled with the VajraSpy remote access trojan (RAT)

A researcher has published a proof-of-concept (PoC) tool for a kernel vulnerability, CVE-2024-23208 remedied in iOS 17.3