
 Do Son
Years ago, Google introduced website notifications to its Chrome browser, allowing sites to use an API to...
Latest news

Apple employs various methods — including the collection of anonymized data — to detect potential security threats....

The CERT Coordination Center (CERT/CC) has issued a warning regarding a critical supply chain vulnerability — CVE-2025-11577...

Elastic has released urgent security updates for Elastic Cloud Enterprise (ECE) to patch a critical vulnerability (CVE-2025-37729)...

A research team from ETH Zurich has disclosed a critical vulnerability — CVE-2025-0033, dubbed RMPocalypse — that...

Seqrite Threat Research Labs has uncovered a targeted phishing campaign in Spanish designed to trick Colombian users...

The Socket Threat Research Team has uncovered a growing trend among malicious package developers: leveraging Discord webhooks...

A newly formed cybercrime consortium known as Scattered Lapsus$ Hunters (SLSH) — also dubbed the “Trinity of...
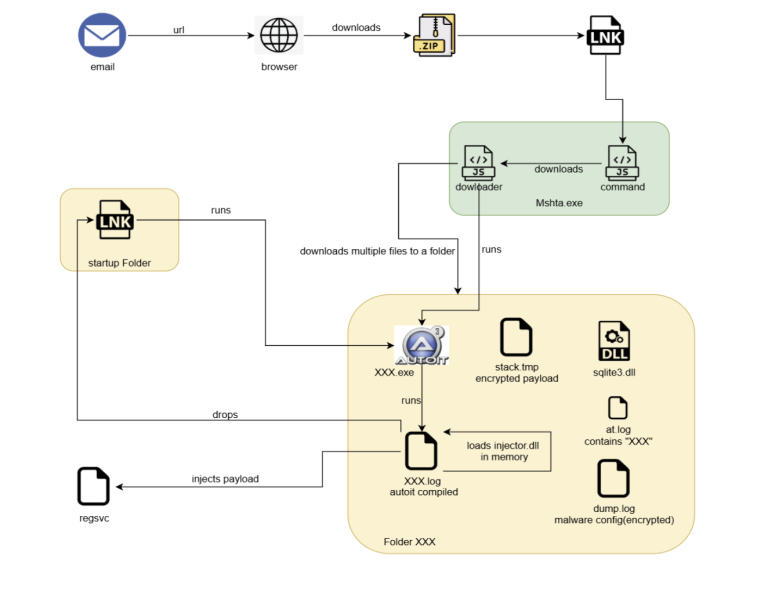
The McAfee Threat Research team has uncovered a new and sophisticated Astaroth malware campaign — using GitHub...

The long-rumored foldable iPhone — tentatively referred to as the iPhone Fold — has yet to be...

Kimsuky, has unleashed a sophisticated spearphishing campaign, targeting hundreds of influential individuals globally

Tagged with an 'important' severity rating, CVE-2023-51784 is a Remote Code Execution (RCE) vulnerability in Apache InLong Manager

GXC Team has enhanced its capabilities for automated operations, targeted social engineering, and bypassing cybersecurity measures

The Python community has recently faced a new threat: three new malicious PyPI packages that deploy CoinMiner on Linux devices

At the heart of the UAC-0050 threat group's arsenal is RemcosRAT, a malware for remote surveillance and control.

With a CVSS score of 8.6, this vulnerability exposes a chink in the armor of many websites, leaving them vulnerable to unauthenticated attacks

Advent of scheduled task tampering as a persistence mechanism underscores the need for continuous evolution in threat-hunting

PoC code has been released for iOS and macOS vulnerability, CVE-2023-41974, that can be chained to take full control of a mobile device

Both vulnerabilities, identified as CVE-2023-48419 and CVE-2023-6339, carry the maximum severity rating with a CVSSv3 score of 10.

The first vulnerability addressed by the patches is CVE-2023-48418, carrying the highest severity rating with a CVSSv3 score of 10

Classified as critical, CVE-2023-4677 allows attackers to execute arbitrary commands on all connected agents, leading to mass compromise.
The agency recently added two significant vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog

PoC code has been released for a zero-day iOS vulnerability (CVE-2023-32434) that can be chained to take full control of a mobile device.

CVE-2023-33025 (CVSS 9.8): This vulnerability, rooted in memory corruption during non-standard SDP bodies in VOLTE calls

Security researchers from xlab-qianxin detected Mirai.TBOT, a variant of the original Mirai, operates with distinct characteristics

Their research has refined the classic DLL Search Order Hijacking technique, leveraging executables in the trusted WinSxS folder of Windows OS

Deepin-Compressor, the default archive manager for the Deepin Linux OS, has been identified as having a path traversal flaw- CVE-2023-50255

PoC exploit code has been made available for a recently disclosed flaw, CVE-2023-50226 (CVSS 7.8), impacting Parallels Desktop

A recent discovery has cast a shadow over its robustness – the CVE-2023-7163 vulnerability, a critical flaw with a maximum CVSSv3 score of 10

These actors have been utilizing the ms-appinstaller protocol handler as a vector for malware, potentially leading to ransomware distribution

A moderate severity flaw, this vulnerability lurked in the shadows of Apache OpenOffice and LibreOffice, where embedded content

CVE-2023-49299 security vulnerability allows an authenticated user to execute arbitrary, unsandboxed JavaScript on the server.