
 Do Son
As generative AI applications continue to expand, the Massachusetts Institute of Technology’s (MIT) Computer Science and Artificial...
Latest news

The latest version of Copilot on Windows (version 1.25095.161.0) introduces a new feature called “Connector,” which can...

According to a report from Bloomberg News, Apple is expected to unveil two to three new products...

With the official launch of AirPods Pro 3 last month, the market had widely anticipated that Apple...
OpenAI Wins Reprieve: Court Vacates Order Forcing Indefinite Preservation of All ChatGPT Output Data

OpenAI Wins Reprieve: Court Vacates Order Forcing Indefinite Preservation of All ChatGPT Output Data
A U.S. federal court has issued a new ruling in The New York Times’ copyright infringement lawsuit...

Apple has quietly confirmed on its official support page that it has formally discontinued updates and removed...

Several years ago, Microsoft announced that it would officially end technical support for Windows 10 on October...

Finding a genuine software key within your budget can be difficult. A high regular price combined with...

Since the first half of the year, the Mozilla Foundation has been testing a new feature called...

The successor to the CM system, LineageOS, has recently released version 23.0, developed on Android 16. This...

Ateam Inc., disclosed that 935,779 personal data records stored in their cloud service were accessible over the Internet.

Panasonic Avionics Corporation, revealed that they suffered a cyberattack at the end of 2022, which may have led to the leak of personal information

Central to Kimsuky's operations is AppleSeed, a backdoor malware that facilitates remote system control. It can execute commands

In the firmware versions v3.3 and earlier of the ioLogik E1200 Series, a menacing vulnerability was lurking, codenamed CVE-2023-5961

Recent revelations from Palo Alto Networks have cast a spotlight on two specific vulnerabilities within Google Kubernetes Engine

The cybercriminal community in the shadowy realms of the Dark Web orchestrated their chilling celebration - "Leaksmas."

CVE-2023-41990 was addressed with improved handling of caches. This issue is fixed in tvOS 16.3, iOS 16.3 and iPadOS 16.3

Carbanak malware, previously utilized for stealing banking data, is now employed by the cybercriminal group FIN7 for remote control
NASA has released the edition of a guide on best practices for cybersecurity in space, as announced in a press release on the website

JaskaGO malware checks whether it is operating on a virtual machine, and if so, performs a harmless task, like pinging Google, to avoid detection

This flaw, identified as CVE-2023-47565 and rated with a concerning CVSS v3 score of 8.0, reveals a significant gap in network security

CVE-2023-45741 allows an authenticated remote attacker to exploit the router by injecting arbitrary commands into the operating system

CVE-2023-51467 enables pre-authentication RCE, allowing attackers to bypass authentication mechanisms and directly perform SSRF attacks

In the vast expanse of the digital ocean, a new wave of cyber attacks has emerged, targeting the seemingly unassuming Linux SSH servers.

PhantomControl, a chameleon in the digital world, has previously been associated with the Blind Eagle threat actors

Barracuda Networks has faced a formidable challenge with the discovery of two zero-day vulnerabilities, CVE-2023-7102 and CVE-2023-7101

As UAC-0050 adapts and refines its tactics, utilizing services of a Malaysian provider and the autonomous system AS44477 for hosting

Doctor Web's virus activity review revealed an 18.09% decrease in overall threats compared to October, with unique threats also diminishing by 13.79%
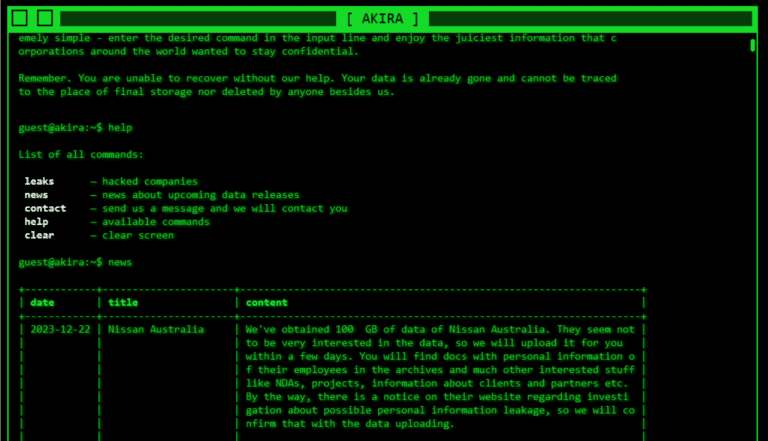
The ransomware group Akira has declared responsibility for the recent cyberattack on the systems of Nissan in Australia and New Zealand

Dubbed Operation RusticWeb, this campaign, uncovered in October 2023, demonstrates a nuanced approach to cyber espionage.

An emerging Iranian hacking group named Cyber Toufan recently disclosed stolen data from 49 Israeli companies.

In the dynamic realm of cybersecurity, the discovery of RetSpill marks a significant evolution in Linux kernel exploitation