
 Do Son
A critical-severity vulnerability has been disclosed in Happy DOM, a popular JavaScript package used to emulate web...
Latest news

The Zero Day Initiative (ZDI) has published details of two critical vulnerabilities in the popular open-source compression...

The Socket Threat Research Team has sounded the alarm on an escalating wave of malicious npm activity...
China’s State Administration for Market Regulation (SAMR) recently announced the launch of an antitrust investigation into U.S....

OpenAI’s newly launched short-video platform “Sora,” which enables users to generate audiovisual content directly through AI, has...
Microsoft Finally Fixes Windows 11 Bug Causing PCs to Auto-Restart Instead of ‘Update and Shut Down’

Microsoft Finally Fixes Windows 11 Bug Causing PCs to Auto-Restart Instead of ‘Update and Shut Down’
Windows 11 users are likely familiar with the system’s habit of prompting a restart after automatically installing...

The notorious Israeli commercial spyware developer NSO Group has confirmed that it has been acquired by a...

Socket’s Threat Research Team has uncovered a massive supply-chain abuse campaign leveraging npm’s public registry and unpkg.com’s...

 cybernewswire

Security researcher Chino Kafuu details a flaw buried deep within the Transport Layer Security (TLS) subsystem of...

A member of the notorious international hacking collective Lapsus$ was apprehended in the United Kingdom at the tender age of 18
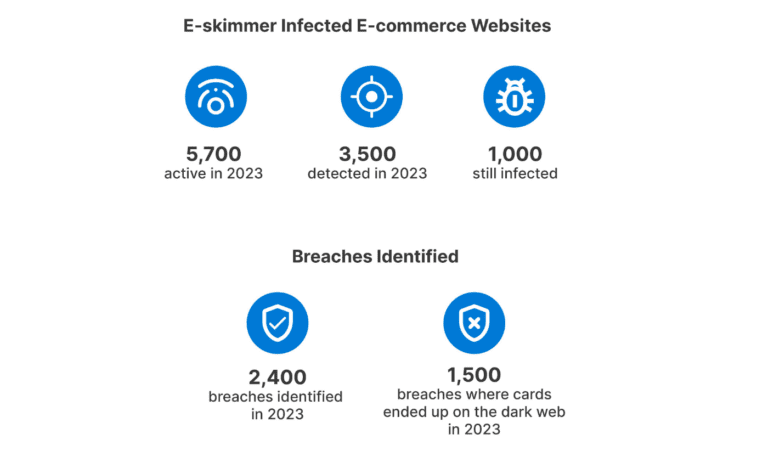
The 2023 Payment Fraud Intelligence Report unveils a concerning resurgence in the payment fraud landscape.

In the ever-evolving landscape of cyber threats, MageCart malware emerges as a formidable foe, especially for WordPress users

Akira ransomware group exemplifies the evolving nature of cyber threats. Their ability to adapt tactics, from encryption-based ransomware

Cisco Talos's in-depth analysis unveils the stealth and persistence of Intellexa's infamous Predator spyware

In 2024, the cyber threat landscape is not just a technical challenge; it is a test of our collective resilience and adaptability.

MetaStealer found its way into systems primarily through malspam and cracked software distributed via hijacked YouTube accounts.

The X.Org Server and XWayland have released updates to address two significant vulnerabilities: CVE-2023-6377 and CVE-2023-6478

Proof-of-concept (PoC) exploit code has been published for a Windows kernel vulnerability tracked as CVE-2023-36424.

A new predator lurks - sophisticated threat actors using malicious JavaScript to steal sensitive information

In an era where mobile banking has become the norm, a new threat looms large, especially in India's banking sector - Android phishing.

One of the most alarming aspects of CVE-2023-7024 is that it had been actively exploited in the wild before its discovery.

Identified as CVE-2023-48738 and rated 9.3 on the CVSS scale, this vulnerability was a ticking time bomb in the Porto theme's code.

Magecart, the perpetual phantom haunting e-commerce, continued its reign of terror by exploiting unpatched websites to steal credit card data

a malicious software distribution campaign they uncovered, which uses JavaScript web injections to steal banking data from 40 banks

Neurosurgical Associates of New Jersey announced a security breach wherein an unauthorized malicious actor accessed the email of one of the employees

A staggering 26,447 vulnerabilities were disclosed in 2023, surpassing 2022's total by over 1,500 CVEs.

The discovery of CVE-2023-50917 serves as a stark reminder of the importance of cybersecurity in the realm of smart home automation

In light of a CVE-2023-50164 vulnerability discovered in Apache Struts, Cisco Systems has elucidated the impact on its products.

Unauthenticated attackers can exploit the CVE-2023-6750 (CVSS 9.8) flaw to download database backups made with the plugin.

Tagged as CVE-2023-43826 (CVSS score of 7.5), this security flaw in Apache Guacamole represents a significant threat

The U.S. Department of Justice has announced the FBI's successful infiltration into the infrastructure of the ransomware group ALPHV