
 Do Son
Microsoft Threat Intelligence has issued a warning about a financially motivated campaign conducted by a threat actor...
Latest news

A critical authentication bypass vulnerability has been discovered in Better Auth, a popular framework-agnostic authentication and authorization...

Trend Micro’s Threat Research team has uncovered a serious cloud credential exposure involving Axis Communications, a leading...

Researchers from Kandji’s Threat Intelligence team uncovered a malware campaign targeting macOS users through spoofed Homebrew installer...

GreyNoise Intelligence has issued an alert about a massive coordinated botnet operation targeting Remote Desktop Protocol (RDP)...

The eSentire Threat Response Unit (TRU) identified a new Rust-based backdoor—dubbed ChaosBot—deployed inside a financial services organization’s...

DomainTools Threat Intelligence has exposed a sprawling cybercrime operation that uses a single infrastructure to power multiple...

Between July and August 2025, global security teams have observed a resurgence in Akira ransomware incidents targeting...

Apple has announced a major overhaul of its Security Bounty vulnerability reward program, set to take effect...

The UK Competition and Markets Authority (CMA) has formally designated Google as holding a “Strategic Market Status”...

PhantomControl, a chameleon in the digital world, has previously been associated with the Blind Eagle threat actors

Barracuda Networks has faced a formidable challenge with the discovery of two zero-day vulnerabilities, CVE-2023-7102 and CVE-2023-7101

As UAC-0050 adapts and refines its tactics, utilizing services of a Malaysian provider and the autonomous system AS44477 for hosting

Doctor Web's virus activity review revealed an 18.09% decrease in overall threats compared to October, with unique threats also diminishing by 13.79%
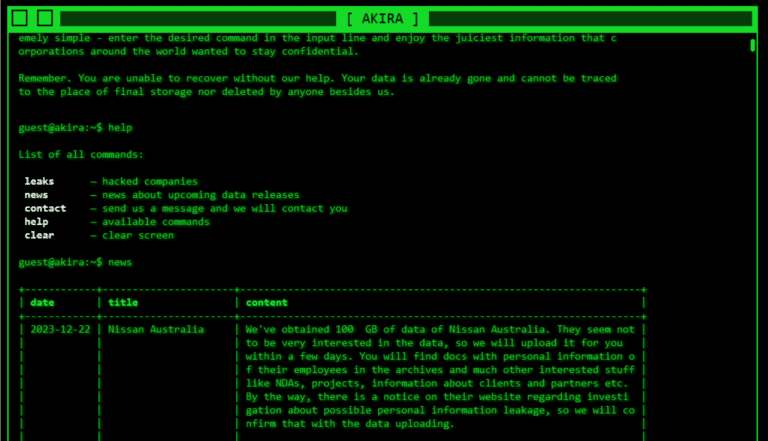
The ransomware group Akira has declared responsibility for the recent cyberattack on the systems of Nissan in Australia and New Zealand

Dubbed Operation RusticWeb, this campaign, uncovered in October 2023, demonstrates a nuanced approach to cyber espionage.

An emerging Iranian hacking group named Cyber Toufan recently disclosed stolen data from 49 Israeli companies.

In the dynamic realm of cybersecurity, the discovery of RetSpill marks a significant evolution in Linux kernel exploitation

Storage virtualization is revolutionizing how businesses used to manage and store their ever-growing data. Put simply, it...

CVE-2023-51443, with a CVSS score of 7.5, exposes FreeSWITCH to DoS attacks during the delicate handshake phase of the DTLS protocol

The campaign unfolded stealthily, leveraging the relatively new Nim programming language to construct a malicious backdoor

Europol undertook a concerted effort to notify 443 online retailers about the compromise of their customers' payment card data
At present, Ubisoft is reluctant to disclose detailed information about this data breach. Several days have elapsed since the incident

A new attack technique named SMTP Smuggling has emerged, threatening the integrity of email communication worldwide.

CVE-2023-51713 exposes a dangerous out-of-bounds buffer read issue in ProFTPD's make_ftp_cmd. This flaw affects version before 1.3.8a

Cyber threat actor UAC-0099 has been actively targeting Ukraine since mid-2022, according to insights from the Deep Instinct Threat Lab

CVE-2023-51385 security vulnerability, with a CVSS score of 9.8, threatened the very core of its secure channel operations.

Tracked as CVE-2023-50254 and scoring a concerning 8.2 on the CVSS scale, this is classified as a file overwrite vulnerability.

Android/Xamalicious has been embedded in about 25 different apps, some of which were distributed on Google Play since mid-2020

Researchers issued CVE-2023-42465 for SUDO for this vulnerability. This flaw classified as critical has been found in sudo up to 1.9.14.

ThreatFabric detected "Chameleon," a banking trojan first identified in early 2023. This malicious entity, thriving in the digital ecosystem

BattleRoyal cluster is notable for its diverse attack chains designed to deliver malware efficiently. DarkGate serves as the gateway