Skip to content
October 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Hackers are actively exploiting BleedingPipe vulnerability in Minecraft mods BleedingPipe vulnerability
  • Vulnerability

Hackers are actively exploiting BleedingPipe vulnerability in Minecraft mods

Do Son August 1, 2023 0
Last Saturday, researchers from the Minecraft security community, MMPA, issued a reminder to gamers via a blog...
Read More Read more about Hackers are actively exploiting BleedingPipe vulnerability in Minecraft mods
CVE-2023-31710: TP-Link Archer AX21 Router Vulnerable to Remote Code Execution CVE-2023-31710
  • Vulnerability

CVE-2023-31710: TP-Link Archer AX21 Router Vulnerable to Remote Code Execution

Do Son August 1, 2023 0
TP-Link has patched a critical vulnerability in its Archer AX21 router that could allow attackers to execute...
Read More Read more about CVE-2023-31710: TP-Link Archer AX21 Router Vulnerable to Remote Code Execution
CISA Adds Ivanti Endpoint Manager Mobile Flaw (CVE-2023-35081) to its KEV Catalog CVE-2023-35081 & CVE-2024-11639
  • Vulnerability

CISA Adds Ivanti Endpoint Manager Mobile Flaw (CVE-2023-35081) to its KEV Catalog

Do Son August 1, 2023 0
Recently, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) cast a spotlight on a particularly disconcerting issue...
Read More Read more about CISA Adds Ivanti Endpoint Manager Mobile Flaw (CVE-2023-35081) to its KEV Catalog
Trojanized MS Visual Studio targeting developers is spreading Trojanized MS Visual Studio
  • Malware

Trojanized MS Visual Studio targeting developers is spreading

Do Son July 31, 2023 0
Microsoft’s Visual Studio, a popular Integrated Development Environment (IDE), is a favored tool amongst developers for creating...
Read More Read more about Trojanized MS Visual Studio targeting developers is spreading
Researchers Disclose MikroTik RouterOS Security Flaw, Putting Hundreds of Thousands of Devices at Risk CVE-2023-30799
  • Vulnerability

Researchers Disclose MikroTik RouterOS Security Flaw, Putting Hundreds of Thousands of Devices at Risk

Do Son July 31, 2023 0
Recently, VulnCheck unveiled in a report a critical privilege escalation vulnerability (CVE-2023-30799, CVSS score 9.1) present within...
Read More Read more about Researchers Disclose MikroTik RouterOS Security Flaw, Putting Hundreds of Thousands of Devices at Risk
Android patches take a long time to reach users’ devices, weakening Android security Android security
  • News

Android patches take a long time to reach users’ devices, weakening Android security

Do Son July 31, 2023 0
Google’s security team recently published a year review of 0-day vulnerabilities exploited in 2022. These reports are...
Read More Read more about Android patches take a long time to reach users’ devices, weakening Android security
CVE-2022-27595 & CVE-2022-27600: Two high-severity flaws in QVPN and QNAP Systems QNAP QVR Pro Vulnerability CVE-2026-22898 CVE-2022-27595 - CVE-2024-48860 & CVE-2024-48861
  • Vulnerability

CVE-2022-27595 & CVE-2022-27600: Two high-severity flaws in QVPN and QNAP Systems

Do Son July 30, 2023 0
QNAP has recently released security advisories for two vulnerabilities that affect the QVPN Device Client for Windows...
Read More Read more about CVE-2022-27595 & CVE-2022-27600: Two high-severity flaws in QVPN and QNAP Systems
Researcher releases PoC exploit for MobileIron zero-day bug (CVE-2023-35078) CVE-2023-35078 PoC
  • Vulnerability

Researcher releases PoC exploit for MobileIron zero-day bug (CVE-2023-35078)

Do Son July 29, 2023 0
A specter is haunting the world of mobile device management – the specter of a zero-day authentication...
Read More Read more about Researcher releases PoC exploit for MobileIron zero-day bug (CVE-2023-35078)
CVE-2023-38646: Remote Command Execution Vulnerability in Metabase CVE-2023-38646
  • Vulnerability

CVE-2023-38646: Remote Command Execution Vulnerability in Metabase

Do Son July 26, 2023 0
In the realm of business intelligence, the open-source tool Metabase has marked its presence with its seamless...
Read More Read more about CVE-2023-38646: Remote Command Execution Vulnerability in Metabase
CVE-2023-37895: A Critical Remote Code Execution in Apache Jackrabbit Apache Jackrabbit, JNDI injection CVE-2023-37895 Apache Jackrabbit, XXE Vulnerability
  • Vulnerability

CVE-2023-37895: A Critical Remote Code Execution in Apache Jackrabbit

Do Son July 26, 2023 0
A critical security vulnerability, identified as CVE-2023-37895, has been discovered in Apache Jackrabbit, an open-source content repository...
Read More Read more about CVE-2023-37895: A Critical Remote Code Execution in Apache Jackrabbit
CVE-2023-38647: Critical Deserialization Vulnerability in Apache Helix Workflow and REST CVE-2023-38647
  • Vulnerability

CVE-2023-38647: Critical Deserialization Vulnerability in Apache Helix Workflow and REST

Do Son July 26, 2023 0
In the dynamic world of cyber security, threats are continually evolving and vulnerabilities are regularly exposed. The...
Read More Read more about CVE-2023-38647: Critical Deserialization Vulnerability in Apache Helix Workflow and REST
Exploring the Mysterious Realm of Free VPNs: An Epic Quest for Cyber Sovereignty and Beyond! India VPN
  • Technique

Exploring the Mysterious Realm of Free VPNs: An Epic Quest for Cyber Sovereignty and Beyond!

Do Son July 25, 2023 0
Introduction Prepare to traverse, valiant souls of the digital domain! Behold the mesmerizing tapestry of the virtual...
Read More Read more about Exploring the Mysterious Realm of Free VPNs: An Epic Quest for Cyber Sovereignty and Beyond!
CVE-2023-26045: NodeBB Forum Software Remote Code Execution Flaw CVE-2023-26045
  • Vulnerability

CVE-2023-26045: NodeBB Forum Software Remote Code Execution Flaw

Do Son July 25, 2023 0
Bulletin board platforms form the heart of our digital forums, acting as arenas for interaction, discussion, and...
Read More Read more about CVE-2023-26045: NodeBB Forum Software Remote Code Execution Flaw
How to Make a Tutorial Video by Using iTop Screen Recorder Screenshot_20230725-083955_Trình chạy Pixel
  • Technique

How to Make a Tutorial Video by Using iTop Screen Recorder

Do Son July 24, 2023 0
In today’s rapidly evolving digital landscape, tutorial videos have become a universal and essential source of knowledge...
Read More Read more about How to Make a Tutorial Video by Using iTop Screen Recorder
CVE-2023-34478: Apache Shiro Path Traversal Vulnerability CVE-2023-34478
  • Vulnerability

CVE-2023-34478: Apache Shiro Path Traversal Vulnerability

Do Son July 24, 2023 0
A critical vulnerability has been identified in Apache Shiro. This security loophole tracked as CVE-2023-34478, can result...
Read More Read more about CVE-2023-34478: Apache Shiro Path Traversal Vulnerability
CVE-2023-38606 & CVE-2023-37450: Apple Addresses Actively Exploited 0-Day Flaws CVE-2023-38606
  • Vulnerability

CVE-2023-38606 & CVE-2023-37450: Apple Addresses Actively Exploited 0-Day Flaws

Do Son July 24, 2023 0
Two critical zero-day vulnerabilities have recently made headlines, threatening the digital security of Apple devices around the...
Read More Read more about CVE-2023-38606 & CVE-2023-37450: Apple Addresses Actively Exploited 0-Day Flaws
Learning Path: Artificial Intelligence Machine Learning (AIML) Engineer Roadmap tech-AI
  • Technique

Learning Path: Artificial Intelligence Machine Learning (AIML) Engineer Roadmap

Do Son July 24, 2023 0
Artificial Intelligence and Machine Learning are making the world go round, and they have transformed how people...
Read More Read more about Learning Path: Artificial Intelligence Machine Learning (AIML) Engineer Roadmap
Going Digital: How You Can Succeed With This tech-mac
  • Technique

Going Digital: How You Can Succeed With This

Do Son July 24, 2023 0
For many companies, the transition to digital working practices has been a steady process that has taken...
Read More Read more about Going Digital: How You Can Succeed With This
CVE-2023-20593: Critical Flaw Discovered in AMD Ryzen 2 and EPYC Processors CVE-2023-20593
  • Vulnerability

CVE-2023-20593: Critical Flaw Discovered in AMD Ryzen 2 and EPYC Processors

Do Son July 24, 2023 0
Cybersecurity threats continue to evolve, and processors are not spared. One recent vulnerability making headlines is CVE-2023-20593,...
Read More Read more about CVE-2023-20593: Critical Flaw Discovered in AMD Ryzen 2 and EPYC Processors
CVE-2023-34966: high-severity vulnerability in Samba critical Samba vulnerabilities remote code execution flaws CVE-2023-34966
  • Vulnerability

CVE-2023-34966: high-severity vulnerability in Samba

Do Son July 24, 2023 0
Samba, a popular freeware implementation of the Server Message Block (SMB) protocol, has released software updates to...
Read More Read more about CVE-2023-34966: high-severity vulnerability in Samba
Multi-Layered Security and Fine-Grained Access Control WordPress Hardening - Access Control
  • Technique

Multi-Layered Security and Fine-Grained Access Control

Mikhail Baranov July 21, 2023 0
Key Takeaways Fine-Grained Access Control: Learn how to apply permissions to specific users via capability-based tokens, which...
Read More Read more about Multi-Layered Security and Fine-Grained Access Control
How an Attacker Took Control of an Active Directory Domain Using CVE-2022-26923 CVE-2022-26923
  • Vulnerability

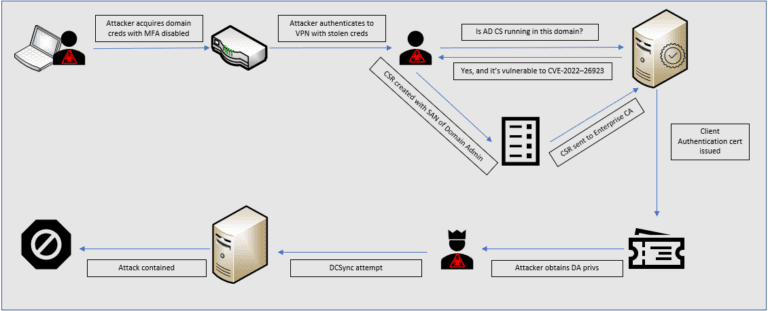
How an Attacker Took Control of an Active Directory Domain Using CVE-2022-26923

Do Son July 21, 2023 0
In June 2023, IBM Security X-Force responded to an incident where a client had received alerts from...
Read More Read more about How an Attacker Took Control of an Active Directory Domain Using CVE-2022-26923
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100800CVSS 9.6
    Sandbox escape due to use-after-free in the Disability Access APIs component. This vulnerability was fixed in Firefox ESR...
    📅 Updated: Oct 19, 2026
  • CVE-2026-102503CVSS 9.3
    Missing Authentication for Critical Function (CWE-306) and Missing Authorization (CWE-862) in the /libp2p-http ingress server (StartIngressServer in cmd/sam-node/node.go)...
    📅 Updated: Oct 19, 2026
  • CVE-2026-103091CVSS 9.3
    Missing Authorization (CWE-862) and Initialization of a Resource with an Insecure Default (CWE-1188) in the MCP proxy (HandleStreamPassThrough...
    📅 Updated: Oct 19, 2026
  • CVE-2026-100804CVSS 9.6
    Sandbox escape due to use-after-free in the Preferences: Backend component. This vulnerability was fixed in Thunderbird 157 and...
    📅 Updated: Oct 19, 2026
  • CVE-2026-100788CVSS 9.8
    Invalid pointer in the JavaScript: WebAssembly component. This vulnerability was fixed in Firefox ESR 153.4, Thunderbird 157, Thunderbird...
    📅 Updated: Oct 19, 2026
  • CVE-2026-112377CVSS 9.1
    CCC Attestation SIG attested-tls-poc through commit 731ca82 fails to bind early attestation Evidence to the TLS connection, allowing...
    📅 Updated: Oct 19, 2026
  • CVE-2026-66788CVSS 9.9
    A flaw was found in Lighthouse. A remote attacker, by compromising a spoke cluster, can exploit a vulnerability...
    📅 Updated: Oct 19, 2026
  • CVE-2026-111406CVSS 9.9
    Unrestricted Upload of File with Dangerous Type vulnerability in PT Norther Lights Production MapSVG mapsvg-lite-interactive-vector-maps allows Upload a...
    📅 Updated: Oct 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.