Skip to content
October 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Atlassian Confluence and Bamboo Remote Code Execution Vulnerabilities CVE-2023-22508 Atlassian Bamboo Vulnerability CVE-2026-21570
  • Vulnerability

Atlassian Confluence and Bamboo Remote Code Execution Vulnerabilities

Do Son July 21, 2023 0
Atlassian has released security advisories for three vulnerabilities in Confluence Data Center & Server and Bamboo Data...
Read More Read more about Atlassian Confluence and Bamboo Remote Code Execution Vulnerabilities
PoC released for critical CloudPanel CVE-2023-35885 vulnerability CVE-2023-35885 PoC
  • Vulnerability

PoC released for critical CloudPanel CVE-2023-35885 vulnerability

Do Son July 21, 2023 0
CloudPanel is a free and modern server control panel that allows users to configure and manage their...
Read More Read more about PoC released for critical CloudPanel CVE-2023-35885 vulnerability
Smart Contract Security Demystified: Uncovering The Intricacies Screenshot_20230721-181028_Trình chạy Pixel
  • Technique

Smart Contract Security Demystified: Uncovering The Intricacies

Do Son July 21, 2023 0
In the ever-evolving landscape of technology, smart contracts are a powerful force in driving countless applications forward....
Read More Read more about Smart Contract Security Demystified: Uncovering The Intricacies
CVE-2023-38408: OpenSSH Remote Code Execution Vulnerability OpenSSH 10.3 Patch SSH Command Injection CVE-2023-38408 OpenSSH Vulnerability CVE-2026-3497
  • Vulnerability

CVE-2023-38408: OpenSSH Remote Code Execution Vulnerability

Do Son July 19, 2023 0
On July 19, 2023, the world’s most widely used implementation of Secure Shell protocol rolled out an...
Read More Read more about CVE-2023-38408: OpenSSH Remote Code Execution Vulnerability
AVrecon RAT hidden in SOHO routers infected 70,000 devices in 20 countries in two years AVrecon malware
  • Malware

AVrecon RAT hidden in SOHO routers infected 70,000 devices in 20 countries in two years

Do Son July 19, 2023 0
Recently, telecommunications giant Lumen’s Black Lotus Labs proclaimed in a blog post that it had uncovered a...
Read More Read more about AVrecon RAT hidden in SOHO routers infected 70,000 devices in 20 countries in two years
Administrator of BreachForums pleads guilty and faces up to 30 years in prison BreachForums Administrator
  • Cyber Security

Administrator of BreachForums pleads guilty and faces up to 30 years in prison

Do Son July 19, 2023 0
This week, Conor Brian Fitzpatrick, a renowned former administrator of the infamous cybercrime forum BreachForums, conceded to...
Read More Read more about Administrator of BreachForums pleads guilty and faces up to 30 years in prison
U.S. launches smart device security standards program – U.S. Cyber Trust Mark U.S. Cyber Trust Mark
  • News

U.S. launches smart device security standards program – U.S. Cyber Trust Mark

Do Son July 19, 2023 0
Recently, the United States has unveiled a proposal for a smart device security standard, coined as the...
Read More Read more about U.S. launches smart device security standards program – U.S. Cyber Trust Mark
CVE-2023-3765: Critical flaw in open source machine learning development MLflow CVE-2023-3765
  • Vulnerability

CVE-2023-3765: Critical flaw in open source machine learning development MLflow

Do Son July 19, 2023 0
MLflow is a popular platform for machine learning development. It allows users to track experiments, package code...
Read More Read more about CVE-2023-3765: Critical flaw in open source machine learning development MLflow
CVE-2023-3519: Critical Zero-Day Vulnerability in Citrix ADC and Gateway CVE-2023-3519
  • Vulnerability

CVE-2023-3519: Critical Zero-Day Vulnerability in Citrix ADC and Gateway

Do Son July 18, 2023 0
Today, Citrix, the well-regarded networking solutions provider, shook the cyber security world with a cautionary announcement: they...
Read More Read more about CVE-2023-3519: Critical Zero-Day Vulnerability in Citrix ADC and Gateway
Freemius WordPress SDK used by 7M sites is vulnerable to XSS attack (CVE-2023-33999) CVE-2023-33999
  • Vulnerability

Freemius WordPress SDK used by 7M sites is vulnerable to XSS attack (CVE-2023-33999)

Do Son July 18, 2023 0
Security analysts at Patchstack have discovered that the popular plugin is vulnerable to CVE-2023-33999. This security vulnerability...
Read More Read more about Freemius WordPress SDK used by 7M sites is vulnerable to XSS attack (CVE-2023-33999)
Spring Security fixes two high-severity flaws – CVE-2023-34034 & CVE-2023-34035 CVE-2023-34034
  • Vulnerability

Spring Security fixes two high-severity flaws – CVE-2023-34034 & CVE-2023-34035

Do Son July 18, 2023 0
Spring Security, with its robust authentication and access-control framework, has earned its stripes as the standard-bearer for...
Read More Read more about Spring Security fixes two high-severity flaws – CVE-2023-34034 & CVE-2023-34035
CISA Adds Office 0-Day Flaw (CVE-2023-36884) to its KEV Catalog CVE-2023-36884
  • Vulnerability

CISA Adds Office 0-Day Flaw (CVE-2023-36884) to its KEV Catalog

Do Son July 18, 2023 0
In an increasingly connected world, the specter of cyber threats looms large, underscoring the importance of maintaining...
Read More Read more about CISA Adds Office 0-Day Flaw (CVE-2023-36884) to its KEV Catalog
CVE-2023-37266: CasaOS Vulnerability Could Allow Attackers to Take Control CVE-2023-37266
  • Vulnerability

CVE-2023-37266: CasaOS Vulnerability Could Allow Attackers to Take Control

Do Son July 17, 2023 0
A security vulnerability has been discovered in CasaOS, an open-source home server system. The vulnerability, which has...
Read More Read more about CVE-2023-37266: CasaOS Vulnerability Could Allow Attackers to Take Control
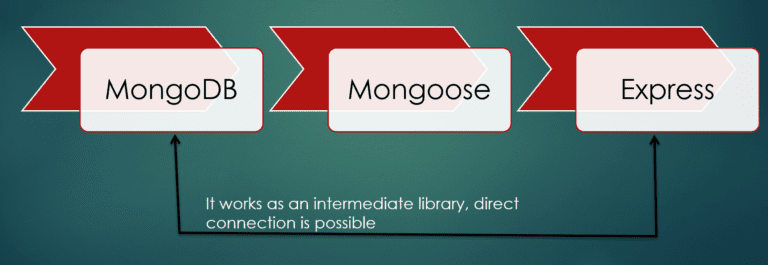
CVE-2023-3696: Critical Prototype Pollution Vulnerability in Mongoose CVE-2023-3696
  • Vulnerability

CVE-2023-3696: Critical Prototype Pollution Vulnerability in Mongoose

Do Son July 17, 2023 0
A piercing siren echoes in the realm of cybersecurity as a severe security flaw, branded as CVE-2023-3696,...
Read More Read more about CVE-2023-3696: Critical Prototype Pollution Vulnerability in Mongoose
CVE-2023-37466: Critical Sandbox Escape Vulnerabilities in VM2 Library CVE-2023-37466
  • Vulnerability

CVE-2023-37466: Critical Sandbox Escape Vulnerabilities in VM2 Library

Do Son July 14, 2023 0
In the realm of cybersecurity, nothing reverberates more fiercely than the clamor of security vulnerabilities surfacing. This...
Read More Read more about CVE-2023-37466: Critical Sandbox Escape Vulnerabilities in VM2 Library
CVE-2023-38198 vulnerability in ACME Shell scrip has exploited in the wild in June 2023 CVE-2023-38198
  • Vulnerability

CVE-2023-38198 vulnerability in ACME Shell scrip has exploited in the wild in June 2023

Do Son July 13, 2023 0
In the continually evolving world of cybersecurity, a recent discovery has brought attention to a significant vulnerability...
Read More Read more about CVE-2023-38198 vulnerability in ACME Shell scrip has exploited in the wild in June 2023
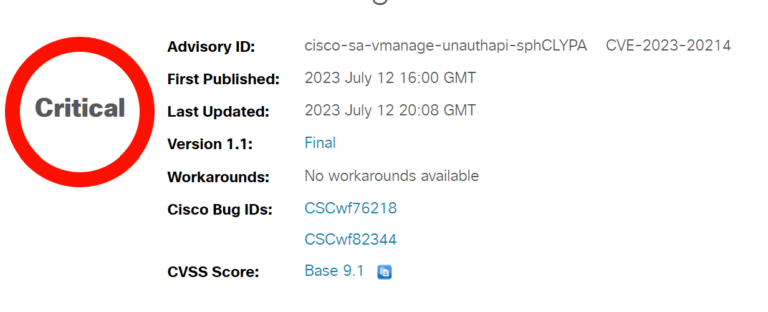
CVE-2023-20214: Cisco SD-WAN vManage Unauthenticated REST API Access Vulnerability CVE-2023-20214
  • Vulnerability

CVE-2023-20214: Cisco SD-WAN vManage Unauthenticated REST API Access Vulnerability

Do Son July 13, 2023 0
Cisco released security updates to address a critical severity vulnerability found in the Cisco SD-WAN vManage software....
Read More Read more about CVE-2023-20214: Cisco SD-WAN vManage Unauthenticated REST API Access Vulnerability
Cracking Power BI: Techniques and Tools for Creating Tables from Existing Data tech-wo
  • Technique

Cracking Power BI: Techniques and Tools for Creating Tables from Existing Data

Do Son July 12, 2023 0
Power BI, Microsoft’s powerful business intelligence tool, empowers users to transform raw data into actionable insights. One...
Read More Read more about Cracking Power BI: Techniques and Tools for Creating Tables from Existing Data
CVE-2023-37582: Apache RocketMQ Remote Code Execution Flaw CVE-2023-37582
  • Vulnerability

CVE-2023-37582: Apache RocketMQ Remote Code Execution Flaw

Do Son July 12, 2023 0
The realm of cyberspace is as vast and complex as the cosmos itself, with intricate systems and...
Read More Read more about CVE-2023-37582: Apache RocketMQ Remote Code Execution Flaw
CVE-2023-33308: Fortinet Patches Critical RCE Vulnerability in FortiOS/FortiProxy CVE-2023-33308
  • Vulnerability

CVE-2023-33308: Fortinet Patches Critical RCE Vulnerability in FortiOS/FortiProxy

Do Son July 12, 2023 0
The digital world we inhabit today is akin to a fortress, a citadel that guards the vast...
Read More Read more about CVE-2023-33308: Fortinet Patches Critical RCE Vulnerability in FortiOS/FortiProxy
Zoom Patches High-Risk Flaws on Windows Platforms and its Client SDK Zoom Rooms LPE, Downgrade Protection Bypass Zoom High-Risk Flaws Zoom security updates
  • Vulnerability

Zoom Patches High-Risk Flaws on Windows Platforms and its Client SDK

Do Son July 12, 2023 0
In a world heavily reliant on digital communications, we’re all surfers riding the wave of technology. One...
Read More Read more about Zoom Patches High-Risk Flaws on Windows Platforms and its Client SDK
CVE-2023-24492: Remote Code Execution in Citrix Secure Access client for Ubuntu CVE-2023-24492
  • Vulnerability

CVE-2023-24492: Remote Code Execution in Citrix Secure Access client for Ubuntu

Do Son July 12, 2023 0
In an era where digital threats persistently test the fortresses of our digital world, our shields must...
Read More Read more about CVE-2023-24492: Remote Code Execution in Citrix Secure Access client for Ubuntu
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100800CVSS 9.6
    Sandbox escape due to use-after-free in the Disability Access APIs component. This vulnerability was fixed in Firefox ESR...
    📅 Updated: Oct 19, 2026
  • CVE-2026-102503CVSS 9.3
    Missing Authentication for Critical Function (CWE-306) and Missing Authorization (CWE-862) in the /libp2p-http ingress server (StartIngressServer in cmd/sam-node/node.go)...
    📅 Updated: Oct 19, 2026
  • CVE-2026-103091CVSS 9.3
    Missing Authorization (CWE-862) and Initialization of a Resource with an Insecure Default (CWE-1188) in the MCP proxy (HandleStreamPassThrough...
    📅 Updated: Oct 19, 2026
  • CVE-2026-100804CVSS 9.6
    Sandbox escape due to use-after-free in the Preferences: Backend component. This vulnerability was fixed in Thunderbird 157 and...
    📅 Updated: Oct 19, 2026
  • CVE-2026-100788CVSS 9.8
    Invalid pointer in the JavaScript: WebAssembly component. This vulnerability was fixed in Firefox ESR 153.4, Thunderbird 157, Thunderbird...
    📅 Updated: Oct 19, 2026
  • CVE-2026-112377CVSS 9.1
    CCC Attestation SIG attested-tls-poc through commit 731ca82 fails to bind early attestation Evidence to the TLS connection, allowing...
    📅 Updated: Oct 19, 2026
  • CVE-2026-66788CVSS 9.9
    A flaw was found in Lighthouse. A remote attacker, by compromising a spoke cluster, can exploit a vulnerability...
    📅 Updated: Oct 19, 2026
  • CVE-2026-111406CVSS 9.9
    Unrestricted Upload of File with Dangerous Type vulnerability in PT Norther Lights Production MapSVG mapsvg-lite-interactive-vector-maps allows Upload a...
    📅 Updated: Oct 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.