
 Do Son
At the Snapdragon Summit 2025 in Hawaii, Qualcomm officially unveiled two new PC-class processors—Snapdragon X2 Elite Extreme...
Latest news

At the Snapdragon Summit 2025 in Hawaii, Qualcomm unveiled its next-generation flagship mobile computing platform—the Snapdragon 8...

The Google Chrome development team has recently released a public preview of the Chrome DevTools Model Context...

 cybernewswire
Luxembourg, Luxembourg, 25th September 2025, CyberNewsWire

Cisco has issued a security advisory warning of a critical flaw in its IOS and IOS XE...

Researchers at K7 Security Labs have uncovered a new wave of Windows shortcut (.LNK) malware that exploits...

Security researcher Puja Srivastava from Sucuri uncovered two malicious files designed to guarantee persistent attacker access by...

With Moldova’s nationwide elections approaching on September 28, 2025, researchers at Silent Push have uncovered a Russian-linked...

The Python Package Index (PyPI) is once again the target of a phishing campaign aimed at maintainers,...

VDE CERT has issued a security advisory disclosing two vulnerabilities in WAGO Device Sphere and WAGO Solution...
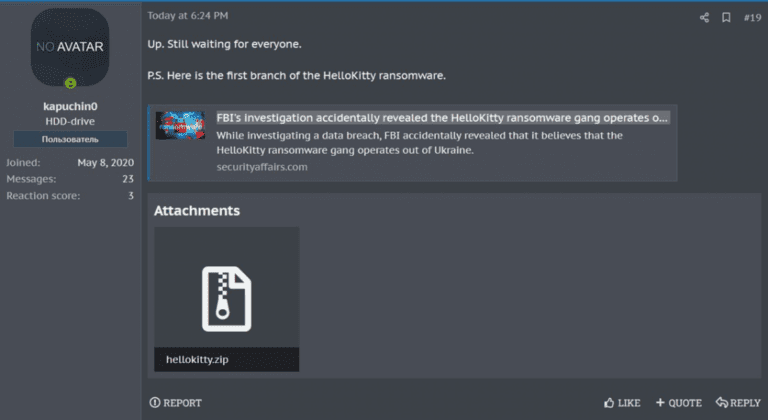
3xp0rt discovered that the full source code of the inaugural version of the HelloKitty ransomware has been unveiled on cybercrime forums

Microsoft relegated VBScript to the Windows Client Deprecated Features list, a catalog of functions that will no longer undergo development

VBA script initiates a series of actions, creating a directory, downloading an AutoIt3 executable, and preparing the ground for the DarkGate malware

Hackers can exploit CVE-2023-43641, to execute malicious code by harnessing Tracker Miners' automatic indexer

Google's research division has unveiled v8CTF, a Capture the Flag (CTF) challenge tailored specifically for its V8 JavaScript engine

Researchers from Cybernews have identified at least 165 exposed networked RTSP cameras in Israel and 29 in Palestine, accessible to anyone

The CVE-2023-44981 vulnerability in Apache ZooKeeper is a critical vulnerability that could allow an arbitrary endpoint

CISA has added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation in the wild

PoC exploit code for CVE-2023-22515 was released, which facilitates unauthorized access to Confluence Server and Data Center instances

Basic vulnerability scanning to see if web servers may be vulnerable to CVE-2023-44487. The tool checks if a web server accepts HTTP/2 requests

Dragović released a PoC exploit code for the CVE-2023-36723 vulnerability. The exploit code abuses a bug in the Container Manager Service

In one audacious instance, an attacker dispatched an astonishing 398 million requests within a singular second
These patches have now been extended to iOS/iPadOS 16, with the latest iteration being iOS/iPadOS 16.7.1 (20H30).

CVE-2023-45648 vulnerability turns particularly sinister behind a reverse proxy, paving the way for request smuggling.

FortiWLM counterpart, the CVE-2023-34992 vulnerability allows for remote unauthenticated OS command injections

The CVE-2023-21709 vulnerability (CVSS score of 9.8) exposes Exchange servers to privilege escalation attacks.

One of the Message Queuing vulnerabilities that was patched in October Patch Tuesday (CVE-2023-35349) has a CVSS severity score of 9.8/10

The vulnerability, designated as CVE-2023-4966, has been assigned a CVSS score of 9.4, indicating its high severity.

Home security has evolved significantly over the years. Once limited to locks, alarms, and maybe a guard...

Leading internet giants, Cloudflare, Google, and Amazon AWS, have announced the discovery of a zero-day flaw, the "HTTP/2 Rapid Reset" attack

VLC media player contains two security vulnerabilities that could be exploited by attackers to take control of users' computers.

Human Security revealed a staggering 74,000 globally distributed Android devices exhibiting traces of the Badbox malware