Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
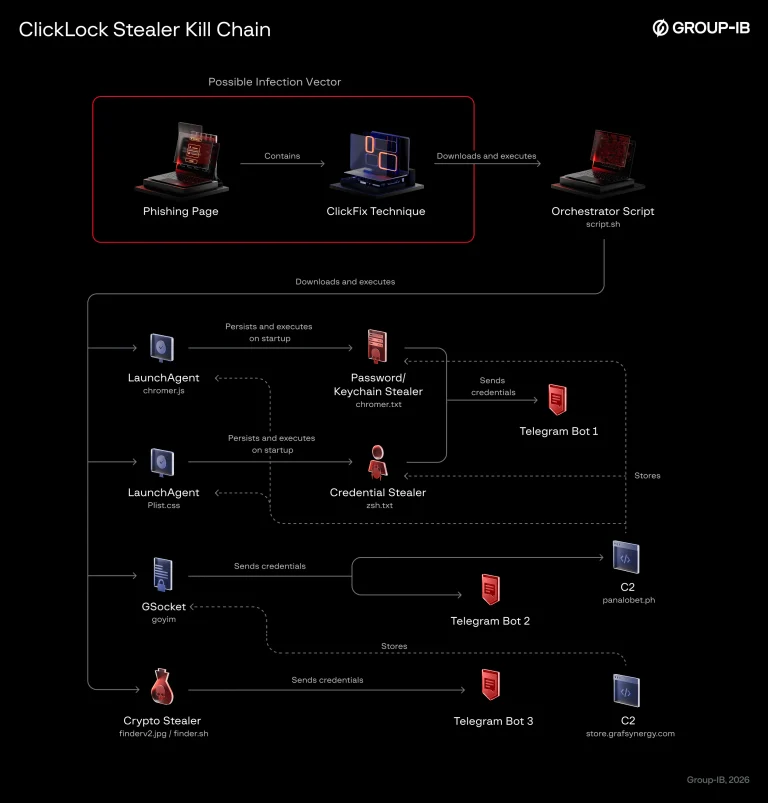
ClickLock Stealer Locks macOS Screens Until Victims Hand Over Their Password ClickLock Stealer macOS malware fake Cloudflare ClickFix Terminal prompt stealing passwords
  • Malware

ClickLock Stealer Locks macOS Screens Until Victims Hand Over Their Password

Do Son July 21, 2026 0

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.
White House Launches GOLD EAGLE Initiative to Speed Vulnerability Patching GOLD EAGLE initiative dashboard for U.S. cybersecurity vulnerability coordination
  • Technology

White House Launches GOLD EAGLE Initiative to Speed Vulnerability Patching

Do Son July 21, 2026 0

The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
Qilin Ransomware Deployed via Palo Alto GlobalProtect Flaw CVE-2026-0257 Qilin ransomware attack chain starting with a Palo Alto GlobalProtect CVE-2026-0257 authentication bypass
  • Cybercriminals

Qilin Ransomware Deployed via Palo Alto GlobalProtect Flaw CVE-2026-0257

Do Son July 21, 2026 0

Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
Linux Kernel Publishes 440 CVE Advisories in 24 Hours as AI Accelerates Bug Hunting 440 Linux kernel CVEs published in 24 hours amid AI-driven vulnerability discovery
  • Linux

Linux Kernel Publishes 440 CVE Advisories in 24 Hours as AI Accelerates Bug Hunting

Do Son July 21, 2026 0

Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.
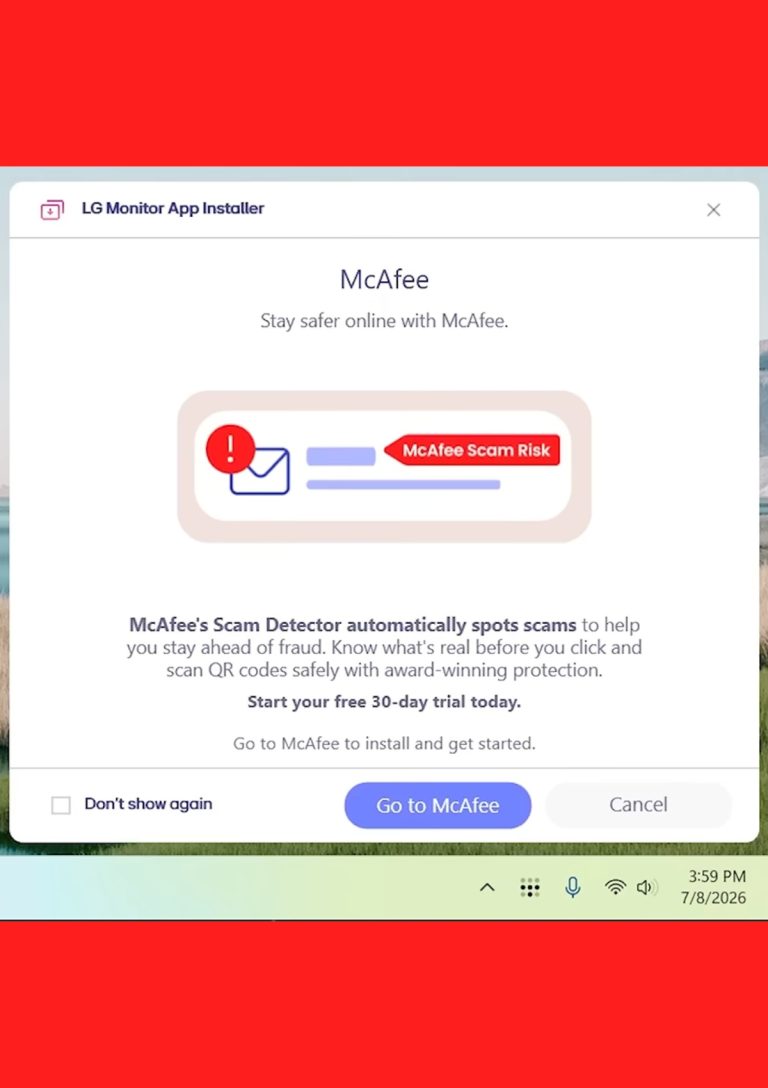
LG Monitors Auto-Install Adware Through Windows Device Metadata LG monitor adware pop-up promoting McAfee on a Windows desktop via device metadata
  • Malware

LG Monitors Auto-Install Adware Through Windows Device Metadata

Do Son July 21, 2026 0

LG monitor adware installs itself via Windows device metadata and pushes McAfee pop-ups. Learn how a Group Policy tweak blocks the unwanted software.
wp2shell: WordPress Core RCE Exploited in the Wild as Public PoC Code Circulates wp2shell exploit chain achieving WordPress Core RCE via CVE-2026-63030 and CVE-2026-60137 batch API abuse
  • Vulnerability Report

wp2shell: WordPress Core RCE Exploited in the Wild as Public PoC Code Circulates

Do Son July 21, 2026 0

wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.

Why Smart Logistics Needs Better Technology  tech
  • Technique

Why Smart Logistics Needs Better Technology 

Do Son July 21, 2026 0
The logistics industry has undergone an incredible change over the last decade. Increasing customer demand, global supply...
Read More Read more about Why Smart Logistics Needs Better Technology 
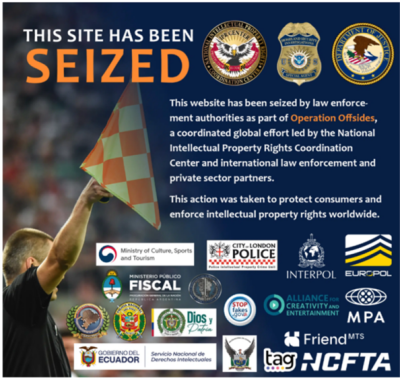
United States Seizes More Than 1,000 Domains Streaming World Cup 2026 Matches Website Seizure Graphic
  • Cybercriminals

United States Seizes More Than 1,000 Domains Streaming World Cup 2026 Matches

Do Son July 20, 2026 0

The US seized 1,000+ domains in an illegal World Cup streaming crackdown, part of global streaming domain seizures under Operation Offsides.
CVE-2026-58443: Gitea Flaw (CVSS 9.6) Details and PoC Exploit Code Publicly Disclosed Gitea vulnerability CVE-2026-58443 public-only token writing to private repository
  • Vulnerability Report

CVE-2026-58443: Gitea Flaw (CVSS 9.6) Details and PoC Exploit Code Publicly Disclosed

Do Son July 20, 2026 0

Gitea vulnerability CVE-2026-58443 (CVSS 9.6) lets public-only tokens write to private repos. Details and PoC code are public. Update to v1.27.0.
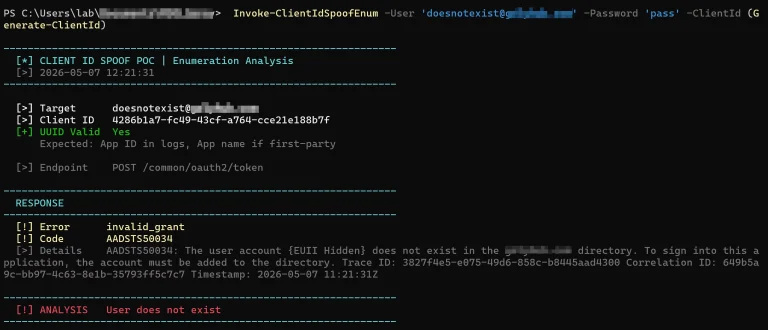
OAuth Client ID Spoofing Lets Attackers Enumerate Entra ID Accounts Without a Trace OAuth client ID spoofing enabling stealthy account enumeration against Microsoft Entra ID sign-in logs
  • Cybercriminals

OAuth Client ID Spoofing Lets Attackers Enumerate Entra ID Accounts Without a Trace

Do Son July 20, 2026 0

Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.
Critical Apache Doris Flaw (CVE-2026-58319) Exposes Admin APIs to Unauthenticated Attackers Apache Doris vulnerability CVE-2026-58319 improper authentication in Frontend HTTP API
  • Vulnerability Report

Critical Apache Doris Flaw (CVE-2026-58319) Exposes Admin APIs to Unauthenticated Attackers

Do Son July 20, 2026 0

Apache Doris vulnerability CVE-2026-58319 lets unauthenticated attackers hit FE HTTP admin APIs. Upgrade to Doris 3.1.0 now to close the flaw.
CVE-2026-56451: CVSS 10 Siemens Opcenter X Flaw Grants Full Unauthorized Access Siemens Opcenter X authentication bypass vulnerability CVE-2026-56451 JWT forgery
  • Vulnerability Report

CVE-2026-56451: CVSS 10 Siemens Opcenter X Flaw Grants Full Unauthorized Access

Do Son July 20, 2026 0

Siemens Opcenter X authentication bypass (CVE-2026-56451, CVSS 10) lets attackers forge JWTs for full unauthorized access. Update to V2604 now.
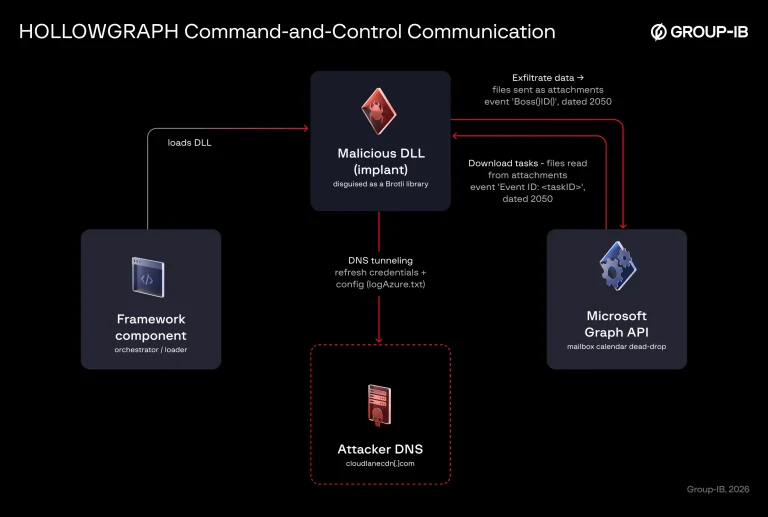
HOLLOWGRAPH Malware Hides Command-and-Control in Microsoft 365 Calendars HOLLOWGRAPH malware using Microsoft Graph API abuse to hide command-and-control inside a Microsoft 365 calendar event dated 2050
  • Malware

HOLLOWGRAPH Malware Hides Command-and-Control in Microsoft 365 Calendars

Do Son July 20, 2026 0

HOLLOWGRAPH malware turns Microsoft 365 calendars into covert C2 through Microsoft Graph API abuse. Group-IB links it to the Cavern framework.
CrashStealer: New macOS Infostealer Poses as Apple Crash Reporter to Steal Wallets and Passwords CrashStealer macOS infostealer posing as Apple crash reporter to steal browser and crypto wallet data
  • Malware

CrashStealer: New macOS Infostealer Poses as Apple Crash Reporter to Steal Wallets and Passwords

Do Son July 20, 2026 0

CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.

Operation ShadowRecruit Uses Fake Government Job Ads to Plant SheetAgent RAT on Indian Systems Salt Typhoon Teleco Hack, Cisco Academy Link CVE-2025-0282 PoC exploit
  • Cybercriminals

Operation ShadowRecruit Uses Fake Government Job Ads to Plant SheetAgent RAT on Indian Systems

Do Son July 20, 2026 0

Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.

LabubaRAT Poses as NVIDIA Software to Hand Operators Full Control of Windows Hosts Exploited VMware
  • Malware

LabubaRAT Poses as NVIDIA Software to Hand Operators Full Control of Windows Hosts

Do Son July 20, 2026 0

LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.
Codex Cuts Its Context Window to 272K and Forbids rm -rf $HOME After Home-Directory Deletions Codex context window change: OpenAI lowers the limit to 272K and forbids rm -rf $HOME in the system prompt after deletions
  • Technology

Codex Cuts Its Context Window to 272K and Forbids rm -rf $HOME After Home-Directory Deletions

Do Son July 20, 2026 0

OpenAI trims the Codex context window from 372K to 272K and adds a system-prompt rule banning rm -rf $HOME after GPT-5.6 Sol wiped user home directories.
Microsoft Ships KB5121767 Out-of-Band Update to Fix a Dell USB-C Compatibility Fault KB5121767 out-of-band update: Microsoft fix for the Dell USB-C driver compatibility fault on affected Precision and XPS laptops
  • Windows

Microsoft Ships KB5121767 Out-of-Band Update to Fix a Dell USB-C Compatibility Fault

Do Son July 20, 2026 0

Microsoft's KB5121767 out-of-band update fixes a Dell USB-C driver fault from the July 2026 patch that caused shutdowns, overheating, and battery drain.
The Mac Pro That Never Shipped: Apple Secretly Built a New Intel Model and Killed Its “Extreme” Chips Mac Pro discontinuation: Apple's cheese-grater tower retired as the Mac Studio and Apple Silicon take over professional workflows
  • Technology

The Mac Pro That Never Shipped: Apple Secretly Built a New Intel Model and Killed Its “Extreme” Chips

Do Son July 20, 2026 0

Gurman reveals a secret new Intel Mac Pro (J170) and cancelled M2/M3 Extreme chips behind the Mac Pro discontinuation, as Mac Studio takes the crown.
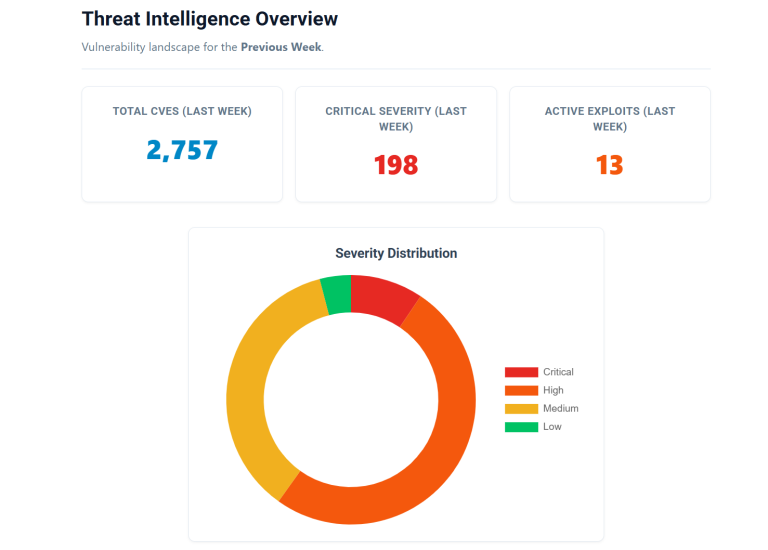
Mid-July 2026: Weekly Threat Intelligence Report actively exploited vulnerabilities
  • Weekly Recap

Mid-July 2026: Weekly Threat Intelligence Report

Do Son July 20, 2026 0

Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
CVE-2026-52824: Default Docker Secret in Kimai Enables Account Takeover of Super Admin Accounts Kimai vulnerability CVE-2026-52824 account takeover via default Docker APP_SECRET
  • Vulnerability Report

CVE-2026-52824: Default Docker Secret in Kimai Enables Account Takeover of Super Admin Accounts

Do Son July 20, 2026 0

Kimai vulnerability CVE-2026-52824 (CVSS 9.1) lets attackers forge cookies for account takeover via a default Docker APP_SECRET. Update to 2.58.0 now.
Why Network Teams Are Pulling Routing Intelligence Back In-House why
  • Technique

Why Network Teams Are Pulling Routing Intelligence Back In-House

Do Son July 20, 2026 0

External routing lookups carry hidden costs: rate limits, data exposure and availability coupling. Here is why teams are moving to self-hosted routing intelligence.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120307CVSS 9.9
    The Beta9 worker serves the sandbox file API from outside the container. getHostPathFromContainerPath turns the tenant's container path...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120306CVSS 9.9
    Beta9 turns each shell command in a tenant image definition into a Dockerfile RUN line and executes it...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120227CVSS 9.4
    A vulnerability was detected in WAVLINK WN701AE M01AE_V260105. This affects the function del_staticrule of the file static_route_setting.sh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-39738CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Aman FunnelKit Automations wp-marketing-automations allows Object Injection.This issue affects FunnelKit Automations: from...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120225CVSS 9.4
    A weakness has been identified in Oray Pugongying X5 Pro up to 7.6.1. Affected by this vulnerability is...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120224CVSS 9.4
    A security flaw has been discovered in Oray Pugongying X5 Pro up to 7.6.1. Affected is the function...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.