
 Do Son
CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now.

CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.

Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.

ASUS security advisories cover seven flaws. CVE-2026-13385 (CVSS 9.5) lets MITM attackers run commands on CN SKU routers. Update firmware now.

A public PoC for CVE-2026-42980 details a Windows privilege escalation flaw in the kernel WMI code. It grants SYSTEM on unpatched builds.

Three Apache Fineract SQL injection flaws (CVE-2026-57821, CVE-2026-56287, CVE-2026-35152) let authenticated users exfiltrate data. Upgrade to 1.15.0.

Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.
CVE-2026-50522, a critical SharePoint RCE flaw, is exploited in the wild. A public PoC exploit is out, so admins should patch SharePoint now.

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.
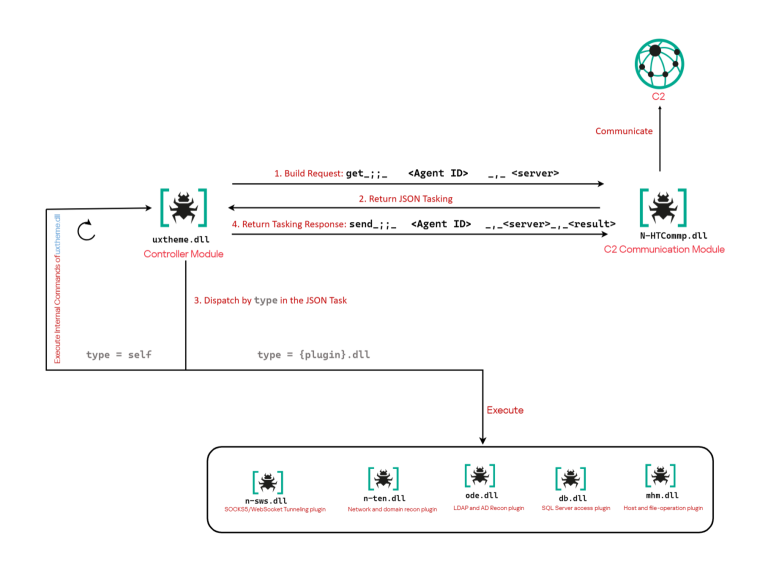
Kaspersky details Project CAV3RN, an OilRig-linked cyberespionage framework. Its new module hides C2 in Outlook calendar events, with DNS AAAA fallback.

Discover the major challenges IT admins face with the UEFI CA 2023 update. Learn why Microsoft, HP, and other OEMs cause BitLocker recovery loops.
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.

Unit 42 exposed TuxBot v3 Evolution, an IoT botnet built with LLM help. AI-written bugs left the malware only 70% functional. See the full analysis.

Discover the details behind the Nextcloud website hacked incident. Hackers exploited a vulnerability to redirect users to a dangerous phishing domain.

Anthropic cut the Claude Team plan minimum from five seats to two. See the new requirements, upgrade paths, and data migration warnings.

An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.
The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.

LG monitor adware installs itself via Windows device metadata and pushes McAfee pop-ups. Learn how a Group Policy tweak blocks the unwanted software.
wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.