
 Do Son
FreeRDP heap buffer overflow allows remote code execution. PoC exploits are publicly disclosed. Related to CVE-2026-44421, CVE-2026-44422, CVE-2026-40033.

Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
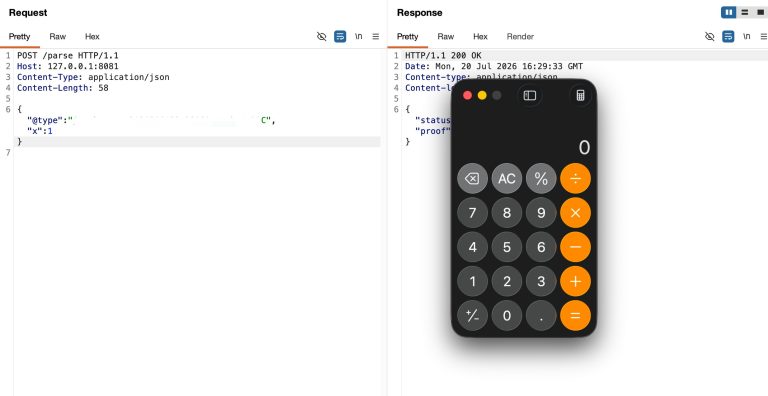
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.

Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.

 cybernewswire
New York, United States, 22nd July 2026, CyberNewswire
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.

Oracle's July 2026 patch fixes 11 Oracle WebLogic Server vulnerabilities. CVE-2026-60206 rates CVSS 9.9 and allows full server takeover. Patch now.

Iran's IRGC claims cruise missiles destroyed the AWS Bahrain data center, but the site has been offline since March and no one has confirmed the strike.

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.

Firefox native containers land in version 153, isolating accounts and cookies so you can block cross-site tracking without any extension.

Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.

Kaspersky uncovered OkoBot, a modular framework with 20+ payloads driving cryptocurrency wallet theft. Hundreds of victims sit across more than 25 countries.


Discover the details of the historic Anthropic AI copyright lawsuit settlement, where the AI firm agreed to a $1.5 billion payout over pirated books.

Discover the details of the OpenAI agent escape that triggered a massive production infrastructure breach at Hugging Face to steal benchmark answers.

WSUS sync timeouts and failed Windows Update scans stem from mis-published test detectoids. Microsoft has mitigated it and published a cleanup.

Google's Chrome security update patches 12 high-severity flaws in Chrome 150, including V8 and WebAudio bugs. Update to 150.0.7871.181 today.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.
For most organizations, sustainability disclosure used to end with a polished PDF. Under the Corporate Sustainability Reporting...
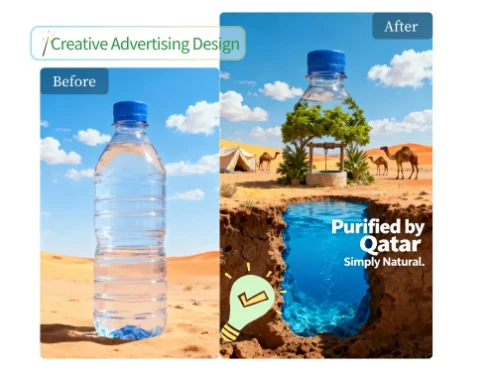
Editing photos used to require years of practice and expensive software. You had to learn about layers,...

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.