Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
TA488 and TA458 Steal Government Email Using Half-Click Webmail Exploits Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Cyber Security

TA488 and TA458 Steal Government Email Using Half-Click Webmail Exploits

Do Son July 23, 2026 0

Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.

JetBrains Patches 18 Flaws, Including Two CVSS 10 Bugs in IntelliJ IDEA Remote Development JetBrains vulnerabilities across IntelliJ IDEA, WebStorm and TeamCity, including CVE-2026-64812 remote development flaws enabling arbitrary code execution
  • Vulnerability Report

JetBrains Patches 18 Flaws, Including Two CVSS 10 Bugs in IntelliJ IDEA Remote Development

Do Son July 23, 2026 0

JetBrains patched 18 vulnerabilities across its IDEs. CVE-2026-64812 and CVE-2026-64813 reach CVSS 10, and most of the rest allow arbitrary code execution.

Apache Syncope Patches SQL Injection and Privilege Escalation Flaws Apache Syncope vulnerabilities including a privilege escalation flaw fixed in CVE-2026-57308 and CVE-2026-62183
  • Vulnerability Report

Apache Syncope Patches SQL Injection and Privilege Escalation Flaws

Do Son July 23, 2026 0

Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.
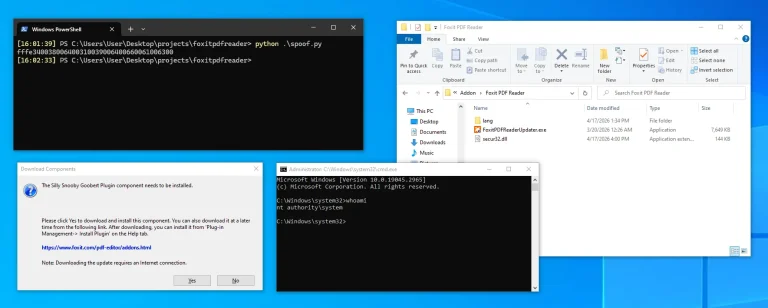
CVE-2026-57239: Public PoC Exploits Foxit PDF Reader Vulnerability for SYSTEM Privileges Foxit PDF Reader vulnerability CVE-2026-57239 exploited for SYSTEM privileges via local privilege escalation
  • Vulnerability Report

CVE-2026-57239: Public PoC Exploits Foxit PDF Reader Vulnerability for SYSTEM Privileges

Do Son July 23, 2026 0

A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.

Next.js Patches Three CVSS 8.3 Flaws in Rewrites, Server Actions, and Middleware Next.js vulnerabilities diagram showing Server-Side Request Forgery through rewrites and Server Actions in CVE-2026-64645 and CVE-2026-64649
  • Vulnerability Report

Next.js Patches Three CVSS 8.3 Flaws in Rewrites, Server Actions, and Middleware

Do Son July 23, 2026 0

Three Next.js vulnerabilities (CVE-2026-64645, CVE-2026-64649, CVE-2026-64642) enable Server-Side Request Forgery and middleware bypass. Patch now.
Unpatched SGLang Flaw CVE-2026-14890 Allows Unauthenticated Remote Code Execution SGLang vulnerability CVE-2026-14890 enabling unauthenticated remote code execution via pickle deserialization
  • Vulnerability Report

Unpatched SGLang Flaw CVE-2026-14890 Allows Unauthenticated Remote Code Execution

Do Son July 23, 2026 0

CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.

Canonical Launches the Enterprise Store for Air-Gapped Networks Canonical Enterprise Store architecture diagram showing software distribution in air-gapped enterprise environments
  • Linux

Canonical Launches the Enterprise Store for Air-Gapped Networks

Do Son July 23, 2026 0

Canonical has introduced the Canonical Enterprise Store for Ubuntu Pro users, enabling software distribution across air-gapped and enterprise networks.

New 10-Inch Raspberry Pi Touch Display 2 Costs $80 Raspberry Pi Touch Display 2 in the 10-inch size showing its 1200x1920 portrait panel connected to a Raspberry Pi 5
  • Technology

New 10-Inch Raspberry Pi Touch Display 2 Costs $80

Do Son July 23, 2026 0

The new 10-inch Raspberry Pi Touch Display 2 brings 1200x1920 resolution and ten-finger touch for $80, but requires a Raspberry Pi 5 or newer.
Dolphin X Stealer Sold on a Cybercrime Forum Uses an AI Profiler to Rank Victims Trojanized streaming site causing Packagist themes iOS spyware infections
  • Cybercriminals

Dolphin X Stealer Sold on a Cybercrime Forum Uses an AI Profiler to Rank Victims

Do Son July 23, 2026 0

Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.

Google’s Nuvem Subsea Cable Links US and Portugal Nuvem subsea cable route linking Myrtle Beach South Carolina to Sines Portugal via Bermuda and the Azores with 384 Tbps capacity
  • Technology

Google’s Nuvem Subsea Cable Links US and Portugal

Do Son July 23, 2026 0

Google's Nuvem subsea cable spans 6,900 km from South Carolina to Portugal via Bermuda, delivering 384 Tbps of transatlantic capacity.

Apple Patches Hide My Email Vulnerability at Last Hide My Email vulnerability in Apple iCloud+ exposing real email addresses behind randomly generated forwarding aliases
  • Vulnerability Report

Apple Patches Hide My Email Vulnerability at Last

Do Son July 23, 2026 0

Apple says a July 3 patch fully closes the Hide My Email vulnerability that exposed real iCloud+ addresses for over a year after disclosure.

GitHub Overhauls Bug Bounty Program with New VIP Tier GitHub bug bounty program restructuring flowchart, VIP security researcher reward tiers
  • Technology

GitHub Overhauls Bug Bounty Program with New VIP Tier

Do Son July 23, 2026 0

Discover how the new GitHub bug bounty program impacts researchers. The platform replaces floating ranges with fixed payouts and a lucrative VIP tier.

GST Phishing Campaign Distributes Remcos RAT Malware DPRK IT Workers, APT38 Crypto Forfeiture
  • Malware

GST Phishing Campaign Distributes Remcos RAT Malware

Do Son July 23, 2026 0

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.

Google Enhances iOS to Android Migration Tool Upgraded Google iOS to Android migration tool interface displaying eSIM data transfer options
  • Android

Google Enhances iOS to Android Migration Tool

Do Son July 23, 2026 0

Discover Google's upgraded iOS to Android migration tool featuring seamless eSIM transfer, saved passwords, Wi-Fi credentials, and WhatsApp data.
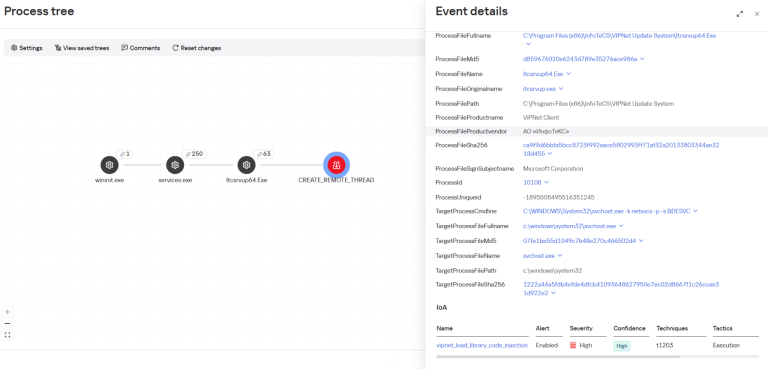
HelloNet Campaign Abuses ViPNet Update System to Hit Russian Firms HelloNet campaign malware delivered through the ViPNet update system on a Russian workstation
  • Cybercriminals

HelloNet Campaign Abuses ViPNet Update System to Hit Russian Firms

Do Son July 23, 2026 0

The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.

DoNot APT Targets Bangladesh Military With a Fake Officer Biography CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cybercriminals

DoNot APT Targets Bangladesh Military With a Fake Officer Biography

Do Son July 23, 2026 0

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.

GitHub Actions Abuse Powers a Distributed cPanel and WHM Attack Campaign WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

GitHub Actions Abuse Powers a Distributed cPanel and WHM Attack Campaign

Do Son July 23, 2026 0

A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.

ISC Patches 9 BIND 9 Vulnerabilities, Including a DNSSEC Cache Poisoning Flaw BIND vulnerability advisory chart listing nine DNSSEC flaws including CVE-2026-13321 cache poisoning fixed in BIND 9.20.26 and 9.21.24
  • Vulnerability Report

ISC Patches 9 BIND 9 Vulnerabilities, Including a DNSSEC Cache Poisoning Flaw

Do Son July 23, 2026 0

ISC fixed 9 BIND vulnerabilities in 9.20.26 and 9.21.24. The top BIND vulnerability, CVE-2026-13321, enables DNSSEC cache poisoning. Patch now.

600K Sites at Risk: Ninja Forms Stored XSS Flaw CVE-2026-65048 Hits CVSS 9.3 Ninja Forms vulnerability dashboard showing CVE-2026-65048 unauthenticated stored XSS with a CVSS 9.3 score across 600K WordPress sites
  • Vulnerability Report

600K Sites at Risk: Ninja Forms Stored XSS Flaw CVE-2026-65048 Hits CVSS 9.3

Do Son July 23, 2026 0

A Ninja Forms vulnerability chain hits 600K+ sites. CVE-2026-65048 is an unauthenticated stored XSS rated CVSS 9.3. Update to 3.14.10 now.

RefluXFS CVE-2026-64600: XFS Root Privilege Escalation Hits 16.4M Systems RefluXFS CVE-2026-64600 XFS privilege escalation to root diagram showing a reflink direct-I/O race overwriting a protected file across 16.4 million Linux systems
  • Vulnerability Report

RefluXFS CVE-2026-64600: XFS Root Privilege Escalation Hits 16.4M Systems

Do Son July 22, 2026 0

Qualys discloses CVE-2026-64600 (RefluXFS), an XFS privilege escalation to root affecting 16.4M+ Linux systems. Patch the kernel and reboot now.

Check Point SmartConsole Auth Bypass CVE-2026-16232 Exploited in the Wild Check Point SmartConsole authentication bypass CVE-2026-16232 exploited in the wild against internet-exposed Management servers
  • Vulnerability Report

Check Point SmartConsole Auth Bypass CVE-2026-16232 Exploited in the Wild

Do Son July 22, 2026 0

Check Point confirms CVE-2026-16232, a SmartConsole authentication bypass, is exploited in the wild. Apply the July 22 jumbo hotfix now.

Exim Directory Traversal Flaw Enables Privilege Escalation, Fixed in 4.99.5 Exim vulnerability diagram showing a directory traversal that escapes the spool area and leads to local privilege escalation
  • Vulnerability Report

Exim Directory Traversal Flaw Enables Privilege Escalation, Fixed in 4.99.5

Do Son July 22, 2026 0

A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.