Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs Chrome security update patching critical use-after-free vulnerabilities in version 150.0.7871.114
  • Vulnerability Report

Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs

Do Son July 9, 2026 0

Google's latest Chrome security update fixes 27 flaws, including two critical use-after-free bugs. Update to 150.0.7871.114 now.

Foxit PDF Reader Flaws Enable Arbitrary Code Execution Foxit PDF Reader arbitrary code execution vulnerability patched in version 2026.1.2
  • Vulnerability Report

Foxit PDF Reader Flaws Enable Arbitrary Code Execution

Do Son July 8, 2026 0

Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.

OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers OpenSSH 10.4 security fixes including a client use-after-free and SFTP SCP path flaws
  • Vulnerability Report

OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers

Do Son July 8, 2026 0

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.

Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts Ghost cache poisoning XSS via x-ghost-preview header advisory graphic
  • Vulnerability Report

Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts

Do Son July 8, 2026 0

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.
Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet Network UPS Tools RCE advisory showing upsmon command injection via ups.alarm
  • Vulnerability Report

Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet

Do Son July 8, 2026 0

A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.

pretix Patches Two Critical Session Takeover and SSRF Flaws pretix vulnerabilities advisory showing the session takeover and SSRF fix
  • Vulnerability Report

pretix Patches Two Critical Session Takeover and SSRF Flaws

Do Son July 8, 2026 0

New pretix vulnerabilities include a critical session takeover chain (CVE-2026-13602) and an SSRF API key leak. Update to 2026.5.3 now.

OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security Untitled_17_x_9_in_1782765623hTY1a9UzBA_1783448292rI4BiJQv9d
  • Press Release

OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security

cybernewswire July 8, 2026 0
Melbourne, Florida, United States, 8th July 2026, CyberNewswire
Read More Read more about OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security
Apache APISIX JWT Authentication Bypass, CVE-2026-39999 APISIX authentication bypass via JWT algorithm confusion, CVE-2026-39999
  • Vulnerability Report

Apache APISIX JWT Authentication Bypass, CVE-2026-39999

Do Son July 8, 2026 0

APISIX authentication bypass CVE-2026-39999 lets attackers forge JWTs via algorithm confusion. APISIX 3.16.0 is affected; upgrade to 3.16.1.

Claude Fable 5 Extension: Free Access Extended Claude Fable 5 extension announcement and API pricing details
  • Technology

Claude Fable 5 Extension: Free Access Extended

Do Son July 8, 2026 0

Anthropic extends the Claude Fable 5 complimentary window until July 12. Discover the 50% quota limit and upcoming transition to the Usage Credits system.

Google Voice Introduces Premium Paid Plans Google Voice paid plans subscription tiers and AI transcription features
  • Technology

Google Voice Introduces Premium Paid Plans

Do Son July 8, 2026 0

Google Voice introduced premium personal paid plans starting at $10 monthly. Discover new features like number retention and AI call transcription today.

Android Remote Root Exploit Chain Unveiled by Nebula Android remote root exploit chain PoC by Nebula
  • Vulnerability Report

Android Remote Root Exploit Chain Unveiled by Nebula

Do Son July 8, 2026 0

Nebula reveals a severe Android remote root exploit chain combining a Firefox vulnerability and a 15-year-old Linux kernel flaw.

SpaceXAI Grok 4.5 Launch: Global Public Release Set SpaceXAI Grok 4.5 launch and V9 foundation model metrics
  • Technology

SpaceXAI Grok 4.5 Launch: Global Public Release Set

Do Son July 8, 2026 0

SpaceXAI Grok 4.5 launch brings Claude Opus-tier intelligence with superior speed and efficiency to the global public.

OpenAI GPT-5.6 Rollout: Global Access Approved OpenAI GPT-5.6 rollout featuring Sol, Terra, and Luna models
  • Technology

OpenAI GPT-5.6 Rollout: Global Access Approved

Do Son July 8, 2026 0

The US government has approved the broad OpenAI GPT-5.6 rollout. Discover pricing, features, and release details for Sol, Terra, and Luna.
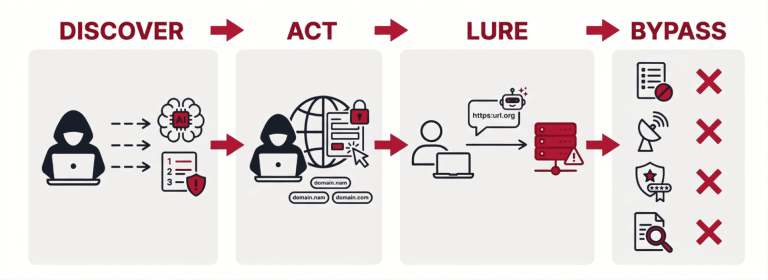
Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns Phantom squatting attacker registering AI hallucinated domains predicted by LLM chatbots
  • Cybercriminals

Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns

Do Son July 8, 2026 0

Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
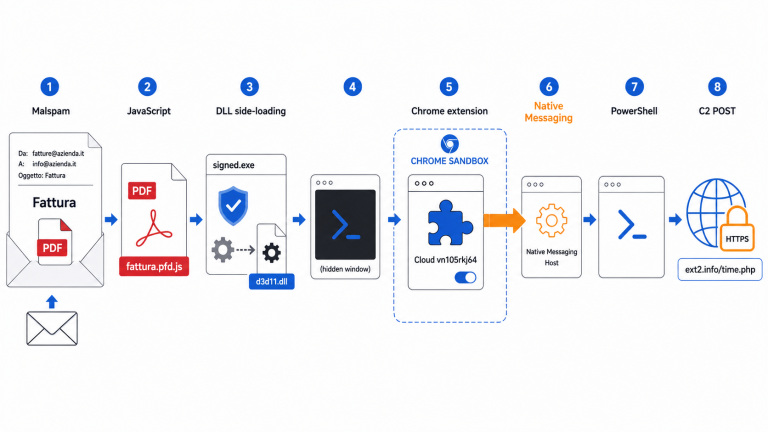
Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat Native Messaging backdoor malicious Chrome extension PowerShell Windows infection chain diagram
  • Malware

Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat

Do Son July 8, 2026 0

A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.

Ubuntu 25.10 End of Life: Prepare Your Upgrade Ubuntu 25.10 end of life warning and upgrade to Ubuntu 26.04 LTS screen
  • Linux

Ubuntu 25.10 End of Life: Prepare Your Upgrade

Do Son July 8, 2026 0

Ubuntu 25.10 end of life is July 9, 2026. Upgrade your system to Ubuntu 26.04 LTS today to maintain crucial security updates and system stability.

The FCC’s Rollback of Broadband Transparency Rules Broadband Consumer Labels transparency rule
  • Technology

The FCC’s Rollback of Broadband Transparency Rules

Do Son July 8, 2026 0

The FCC plans to roll back Broadband Consumer Labels, allowing ISPs to hide junk fees and reducing transparency for everyday internet users.
Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer China influence operations using banned ChatGPT accounts in OpenAI's June 2026 threat report targeting the US AI policy debate
  • Malware

Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer

Do Son July 8, 2026 0

Veil#Drop malware abuses Blogspot to run PowerShell loaders and deploy PureLog Stealer in memory, dodging antivirus and file-based detection.

WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs WordPress outdated PHP end-of-life security risk chart showing plugin and PHP version gaps
  • Vulnerability Report

WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs

Do Son July 8, 2026 0

Censys research finds 70% of WordPress sites run end-of-life PHP. Outdated plugins and defaults leave millions of sites wide open to attack.
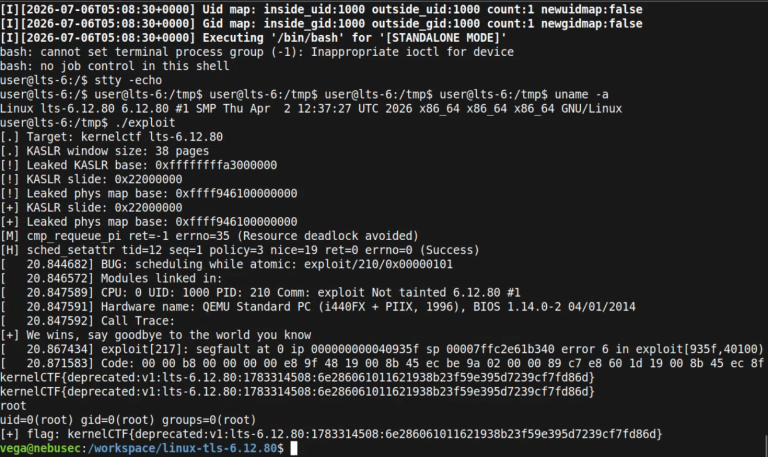
Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape GhostLock CVE-2026-43499 Linux kernel privilege escalation and container escape exploit chain
  • Vulnerability Report

Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape

Do Son July 8, 2026 0

Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
CISA Adds Four Actively Exploited Flaws to Its KEV Catalog CISA KEV Catalog update listing four actively exploited Joomla Langflow and Adobe ColdFusion vulnerabilities
  • Vulnerability Report

CISA Adds Four Actively Exploited Flaws to Its KEV Catalog

Do Son July 8, 2026 0

CISA added four actively exploited flaws to its KEV Catalog, including critical Joomla, Langflow, and ColdFusion bugs. Agencies must patch by July 10.
Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5) Control-M command injection vulnerability CVE-2026-10539 enabling unauthenticated remote command injection on the server
  • Vulnerability Report

Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5)

Do Son July 7, 2026 0

BMC patches Control-M command injection flaw CVE-2026-10539, an unauthenticated remote command injection bug rated CVSS 9.5.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119706CVSS 9.3
    InternLM LMDeploy 0.9.0 through 0.18.0 contains an unauthenticated remote code execution vulnerability that allows remote attackers to run...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105603CVSS 9.4
    Joomla Extension - dj-extensions.com - Authenticated arbitrary file upload in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds...
    📅 Updated: Nov 2, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.