Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public SharePoint remote code execution CVE-2026-33112 XmlValidator bypass proof-of-concept diagram
  • Vulnerability Report

SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public

Do Son July 7, 2026 0

A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.
Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities UniFi security advisory 066 covering 25 vulnerabilities including command injection
  • Vulnerability Report

Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities

Do Son July 7, 2026 0

Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.

Google Updates Android Backup Storage Policy Limits Android backup storage policy warning on a smartphone screen
  • Android

Google Updates Android Backup Storage Policy Limits

Do Son July 7, 2026 0

Discover how Google's new Android backup storage policy impacts your free cloud capacity. Learn to manage your data and avoid unexpected subscription costs.

SpaceXAI: Elon Musk’s Orbital Data Centers Vision SpaceXAI logo and orbital data centers concept in space
  • Technology

SpaceXAI: Elon Musk’s Orbital Data Centers Vision

Do Son July 7, 2026 0

Five months after merging his AI and space ventures, Elon Musk reveals SpaceXAI. Discover how the $2.1 trillion giant plans to build orbital data centers.
ARToken Phishing Platform Steals Microsoft 365 Tokens and Bypasses MFA phsi
  • Cybercriminals

ARToken Phishing Platform Steals Microsoft 365 Tokens and Bypasses MFA

Do Son July 7, 2026 0

Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.
Critical IBM Power HMC Vulnerability Exposes Systems IBM Power HMC vulnerability OS command injection diagram
  • Vulnerability Report

Critical IBM Power HMC Vulnerability Exposes Systems

Do Son July 7, 2026 0

A critical IBM Power HMC vulnerability (CVE-2026-12943) allows unauthenticated attackers to execute commands. Patch your systems immediately.
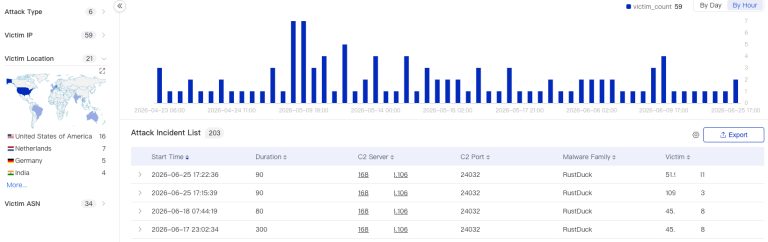
RustDuck Botnet: A Two-Stage DDoS Threat Shifting From C to Rust RustDuck botnet two-stage DDoS malware loader core architecture analysis diagram
  • Malware

RustDuck Botnet: A Two-Stage DDoS Threat Shifting From C to Rust

Do Son July 7, 2026 0

The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.

Windows 11 Cloud Rebuild: Reinstall Without USB Windows Recycle Bin bug showing an internal $Rxxxxx filename in the delete confirmation dialog after the June 2026 update
  • Windows

Windows 11 Cloud Rebuild: Reinstall Without USB

Do Son July 7, 2026 0

Microsoft tests Windows 11 cloud rebuild in WinRE, letting users reinstall via the internet without USB drives when the system fails to boot.
Linux Kernel Vulnerability CVE-2024-26582: Public PoC Reaches Root Shell Linux kernel vulnerability CVE-2024-26582 TLS use-after-free root shell exploit diagram
  • Vulnerability

Linux Kernel Vulnerability CVE-2024-26582: Public PoC Reaches Root Shell

Do Son July 7, 2026 0

A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
DeepSeek AI Generates Browser Native Ransomware GMO Internet ransom demand diagram illustrating cloud security misconfiguration and breach leak
  • Cybercriminals

DeepSeek AI Generates Browser Native Ransomware

Do Son July 7, 2026 0

Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.

CVE-2026-11405: Tenda Undocumented Authentication Backdoor Diagram showing the Tenda authentication backdoor and CVE-2026-11405 attack flow.
  • Vulnerability Report

CVE-2026-11405: Tenda Undocumented Authentication Backdoor

Do Son July 7, 2026 0

CVE-2026-11405 is a Tenda authentication backdoor. It allows full administrative access without valid credentials. Protect your network with these steps.

Cloudflare Workers Cache: Edge Caching for Workers Cloudflare Workers Cache two-layer edge caching architecture with upper and lower cache tiers
  • Technology

Cloudflare Workers Cache: Edge Caching for Workers

Do Son July 7, 2026 0

Cloudflare Workers Cache adds a two-layer edge caching system to Workers, cutting CPU costs, boosting SSR performance, and enabling Cache-Tag invalidation.

Ubuntu 26.04 LTS Elevates Arm64 to First-Class Status Ubuntu Arm64 support logo with Canonical first-class features for Snapdragon and Livepatch
  • Linux

Ubuntu 26.04 LTS Elevates Arm64 to First-Class Status

Do Son July 7, 2026 0

Canonical elevates Ubuntu Arm64 support to first-class in the 26.04 LTS release. Explore Livepatch updates, Snapdragon compatibility, and FEX gaming.

Microsoft Xbox Layoffs: Profound Corporate Restructuring Microsoft Xbox layoffs affecting the gaming division and resulting in studio divestments
  • Technology

Microsoft Xbox Layoffs: Profound Corporate Restructuring

Do Son July 7, 2026 0

The recent Microsoft Xbox layoffs impact 4,800 employees as the gaming division restructures, divests studios, and aims for financial independence.

Windows 11 Storage Bug Causes Massive Log File Bloat Windows 11 storage bug filling drive space alongside CAM log file errors
  • Windows

Windows 11 Storage Bug Causes Massive Log File Bloat

Do Son July 7, 2026 0

A recent Windows 11 storage bug causes the Capability Access Manager log file to consume hundreds of gigabytes. Learn how to verify and fix this issue quickly.
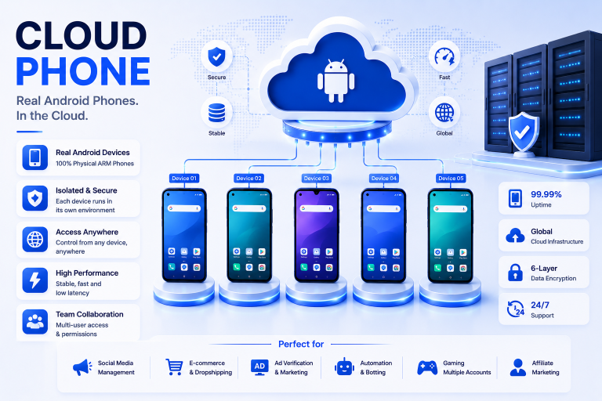
5 Best Cloud Phone Tools in 2026 for Multi-Account Teams cloud
  • Technique

5 Best Cloud Phone Tools in 2026 for Multi-Account Teams

Do Son July 7, 2026 0

Compare 5 cloud phone tools in 2026, including MoreLogin, Hubstudio, VMOS, DuoPlus, and Multilogin for Android workflows and account teams.
CVE-2026-40138 & CVE-2026-40139: BeyondTrust Pre-Auth Flaws (CVSS 9.2) BeyondTrust Remote Support diagram showing pre-authentication vulnerability CVE-2026-40138
  • Vulnerability Report

CVE-2026-40138 & CVE-2026-40139: BeyondTrust Pre-Auth Flaws (CVSS 9.2)

Do Son July 6, 2026 0

BeyondTrust patched two critical pre-authentication vulnerabilities (CVE-2026-40138, CVE-2026-40139, CVE-2026-40140). Update Remote Support instances now.

Public Exploit Disclosed for Januscape KVM Escape and LPE (CVE-2026-53359) Januscape KVM escape architectural diagram showing CVE-2026-53359 use-after-free KVM bug exploitation
  • Vulnerability Report

Public Exploit Disclosed for Januscape KVM Escape and LPE (CVE-2026-53359)

Do Son July 6, 2026 0

Researchers disclosed a PoC for the Januscape KVM escape (CVE-2026-53359). This use-after-free KVM bug impacts public clouds, allowing host panics and LPE.
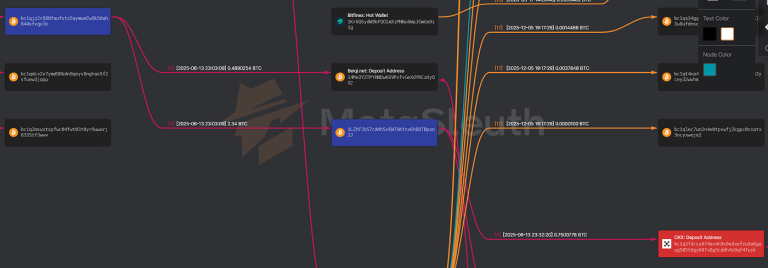
The Illusion of Security: Kairos Ransomware and the Rise of Data Extortion Without Encryption Kairos ransomware data extortion case study showing cyber extortion risks without encryption
  • Cybercriminals

The Illusion of Security: Kairos Ransomware and the Rise of Data Extortion Without Encryption

Do Son July 6, 2026 0

A case study on Kairos ransomware data extortion highlights the futility of paying a $1 million ransom without data encryption.

Critical Cursor IDE RCE Vulnerability Exposes Workspaces Diagram of the DuneSlide attack and Cursor IDE RCE vulnerability mechanism.
  • Vulnerability Report

Critical Cursor IDE RCE Vulnerability Exposes Workspaces

Do Son July 6, 2026 0

Discover the new Cursor IDE RCE vulnerability called DuneSlide. This critical sandbox escape flaw assigned CVE-2026-50548 threatens developer environments.
OpenSSL Error Handling Defect Breaks apt HTTPS Access in FIPS Mode OpenSSL error handling diagram showing a stale error queue entry misread by apt in FIPS mode
  • Vulnerability Report

OpenSSL Error Handling Defect Breaks apt HTTPS Access in FIPS Mode

Do Son July 6, 2026 0

A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.

Microsoft GDID Tracking: How Windows Caught a Hacker Microsoft GDID tracking visualization identifying Scattered Spider hacker Peter Stokes
  • Cybercriminals

Microsoft GDID Tracking: How Windows Caught a Hacker

Do Son July 6, 2026 0

Discover how Microsoft GDID tracking helped the FBI apprehend a Scattered Spider hacker, revealing the hidden power of Windows device telemetry.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119706CVSS 9.3
    InternLM LMDeploy 0.9.0 through 0.18.0 contains an unauthenticated remote code execution vulnerability that allows remote attackers to run...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105603CVSS 9.4
    Joomla Extension - dj-extensions.com - Authenticated arbitrary file upload in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds...
    📅 Updated: Nov 2, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.