Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk insignary_logo_highres_17830044308uQUsWZ4Y3
  • Press Release

Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk

cybernewswire July 6, 2026 0
Toronto, Canada, 6th July 2026, CyberNewswire
Read More Read more about Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk
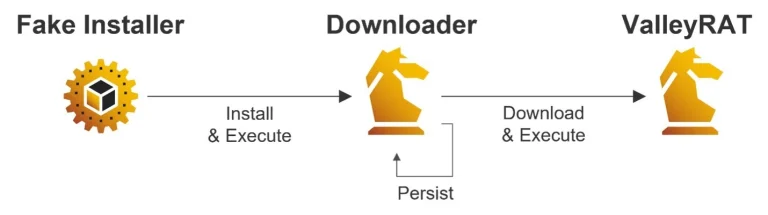
ValleyRAT Malware Hits Japanese and Chinese Users Through Email Attacks ValleyRAT malware email campaign delivering DLL sideloading payload to Japanese and Chinese users
  • Malware

ValleyRAT Malware Hits Japanese and Chinese Users Through Email Attacks

Do Son July 6, 2026 0

LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
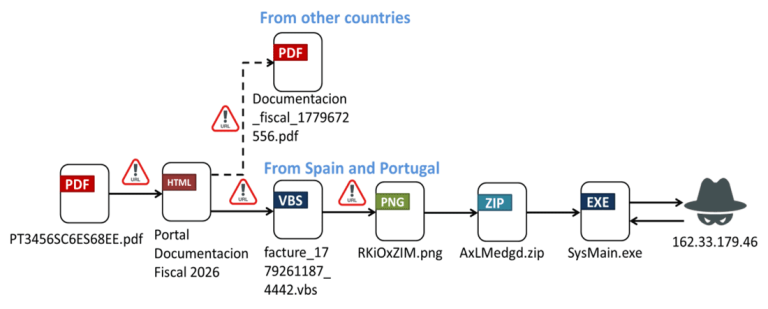
Ousaban Banking Trojan Targets Spain and Portugal Ousaban banking trojan infection chain diagram showing malware delivery methods.
  • Malware

Ousaban Banking Trojan Targets Spain and Portugal

Do Son July 6, 2026 0

FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.

TAG-182 Threat Cluster Spreads MarkiRAT Malware Diagram of TAG-182 threat cluster spreading MarkiRAT malware
  • Cybercriminals

TAG-182 Threat Cluster Spreads MarkiRAT Malware

Do Son July 6, 2026 0

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

The Fall of HiAnime: Vietnamese Police Arrest Piracy Ring Vietnamese police conduct HiAnime piracy arrests, dismantling a massive illegal anime streaming syndicate.
  • Cybercriminals

The Fall of HiAnime: Vietnamese Police Arrest Piracy Ring

Do Son July 6, 2026 0

Vietnamese police made several HiAnime piracy arrests, dismantling a massive anime streaming network that generated over $12 million in illegal revenue.

PHP Patches Remote DoS Flaw CVE-2026-12184 and an OpenSSL Memory Corruption Bug PHP remote DoS advisory graphic showing a PHP-FPM crash and openssl memory corruption
  • Vulnerability Report

PHP Patches Remote DoS Flaw CVE-2026-12184 and an OpenSSL Memory Corruption Bug

Do Son July 6, 2026 0

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.
Multiple IBM WebSphere Vulnerabilities Expose Systems IBM WebSphere vulnerabilities CVE-2026-11712 CVE-2026-11595
  • Vulnerability Report

Multiple IBM WebSphere Vulnerabilities Expose Systems

Do Son July 6, 2026 0

IBM WebSphere vulnerabilities like CVE-2026-11712 expose servers to severe XSS and path traversal attacks. Patch systems immediately.

Weekly Threat Intelligence: The July 2026 Breaches Weekly Threat Intelligence Active Vulnerability Report
  • Weekly Recap

Weekly Threat Intelligence: The July 2026 Breaches

Do Son July 6, 2026 0

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and critical CISA KEV additions.
FreeBSD Security Advisories Detail Critical Vulnerabilities Diagram of system vulnerabilities detailed in FreeBSD security advisories including CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422
  • Vulnerability Report

FreeBSD Security Advisories Detail Critical Vulnerabilities

Do Son July 6, 2026 0

Recent FreeBSD security advisories detail severe flaws like CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422. Patch immediately to stop attacks.
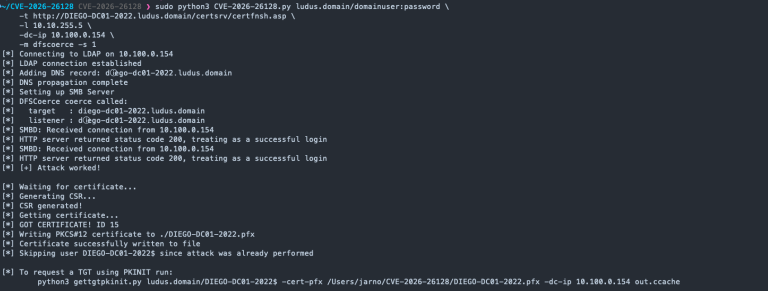
Kerberos Reflection Bypass CVE-2026-26128 Gets Public PoC Exploit Kerberos reflection CVE-2026-26128 SMB SYSTEM privilege escalation Windows Unicode SPN PoC exploit
  • Vulnerability Report

Kerberos Reflection Bypass CVE-2026-26128 Gets Public PoC Exploit

Do Son July 6, 2026 0

Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.

ModSecurity Vulnerabilities Let Attackers Bypass WAF Rules ModSecurity vulnerabilities enabling WAF bypass via multipart parser and utf8toUnicode flaws (CVE-2026-52747, CVE-2026-52761)
  • Vulnerability Report

ModSecurity Vulnerabilities Let Attackers Bypass WAF Rules

Do Son July 6, 2026 0

Two ModSecurity vulnerabilities let attackers slip past WAF rules via a multipart parser bug (CVE-2026-52747). Update to ModSecurity v3.0.16 now.

FBI Warns of TeamPCP Supply Chain Attack TeamPCP supply chain attack and software supply chain compromise alert
  • Cybercriminals

FBI Warns of TeamPCP Supply Chain Attack

Do Son July 4, 2026 0

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.
Critical Security Flaws Found in Langflow OSS Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Vulnerability Report

Critical Security Flaws Found in Langflow OSS

Do Son July 4, 2026 0

Multiple Langflow OSS vulnerabilities, including the critical CVE-2026-10134 flaw, expose servers to code execution. Patch immediately.
DCMTK Vulnerabilities Expose Medical Imaging Systems to File Write and DoS DCMTK vulnerabilities enabling path traversal file write in the DICOM toolkit (CVE-2026-50003)
  • Vulnerability Report

DCMTK Vulnerabilities Expose Medical Imaging Systems to File Write and DoS

Do Son July 4, 2026 0

Five DCMTK vulnerabilities hit the DICOM toolkit, including a CVSS 9.8 path traversal file write (CVE-2026-50003). Update DCMTK now.

GitHub CD-ROM Repository: Physical Code Discs GitHub CD-ROM repository physical code disc campaign commemoration
  • Technology

GitHub CD-ROM Repository: Physical Code Discs

Do Son July 3, 2026 0

GitHub launches a limited-edition campaign to burn your public code into a physical GitHub CD-ROM repository, mocking Sony's physical media exit.

Claude Fable 5 Subscription: Credits Required for Access Claude Fable 5 subscription model and credit purchase prompt interface
  • Technology

Claude Fable 5 Subscription: Credits Required for Access

Do Son July 3, 2026 0

Anthropic's Claude Fable 5 subscription policy requires additional credits due to capacity limits, sparking double-billing concerns among developers.

Chrome Prepares to Auto-Pin Extensions to Toolbar Google Chrome settings page showcasing the new auto-pin extensions option for toolbars
  • Technology

Chrome Prepares to Auto-Pin Extensions to Toolbar

Do Son July 3, 2026 0

Google Chrome introduces a new option to auto-pin extensions to the toolbar by default, addressing user forgetfulness and enhancing browser security.

Claude Fable 5 Auto-Downgrades Tasks It Deems Too Simple Logs Prove It Claude Fable 5 model classifier downgrade log showing TOO_DUMB_TO_NEED_FABLE flag
  • Technology

Claude Fable 5 Auto-Downgrades Tasks It Deems Too Simple Logs Prove It

Do Son July 3, 2026 0

Claude Fable 5 auto-downgrades tasks it flags as too simple, logging a blunt internal label that has sparked outrage among developers.

Lazarus-Linked npm Malware Masquerades as Rollup Polyfills Lazarus npm malware masquerading as Rollup polyfill packages in a supply chain attack
  • Cybercriminals

Lazarus-Linked npm Malware Masquerades as Rollup Polyfills

Do Son July 3, 2026 0

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.
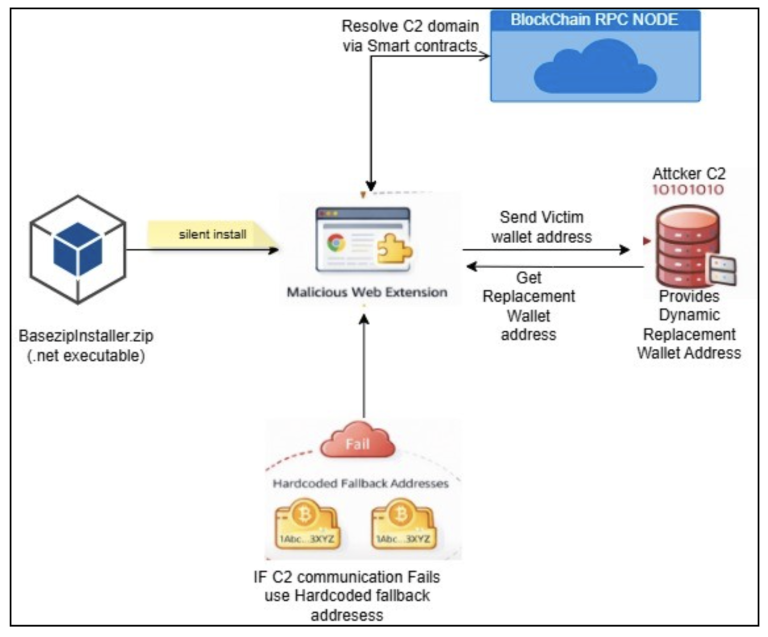
Silent Swap Crypto Clipper Hides in Google Notes Extension Diagram showing the Silent Swap crypto clipper and Google Notes extension infection chain
  • Malware

Silent Swap Crypto Clipper Hides in Google Notes Extension

Do Son July 3, 2026 0

The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.

kernel.org Outage: Config Error Wipes All Linux Kernel Files kernel.org outage HTTP 404 error caused by Linux Foundation mirror configuration failure
  • Technology

kernel.org Outage: Config Error Wipes All Linux Kernel Files

Do Son July 3, 2026 0

A configuration error at kernel.org deleted all Linux kernel archives. The Linux Foundation confirmed the outage and began recovery efforts.

EU Court Upholds €4.1 Billion Google Android Antitrust Fine EU Court upholds Google Android antitrust fine of 4.1 billion euros in landmark ruling
  • Technology

EU Court Upholds €4.1 Billion Google Android Antitrust Fine

Do Son July 3, 2026 0

The EU's top court upholds the €4.1 billion Google Android antitrust fine, confirming illegal monopoly conduct and setting a powerful precedent.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119706CVSS 9.3
    InternLM LMDeploy 0.9.0 through 0.18.0 contains an unauthenticated remote code execution vulnerability that allows remote attackers to run...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105603CVSS 9.4
    Joomla Extension - dj-extensions.com - Authenticated arbitrary file upload in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds...
    📅 Updated: Nov 2, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.