Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
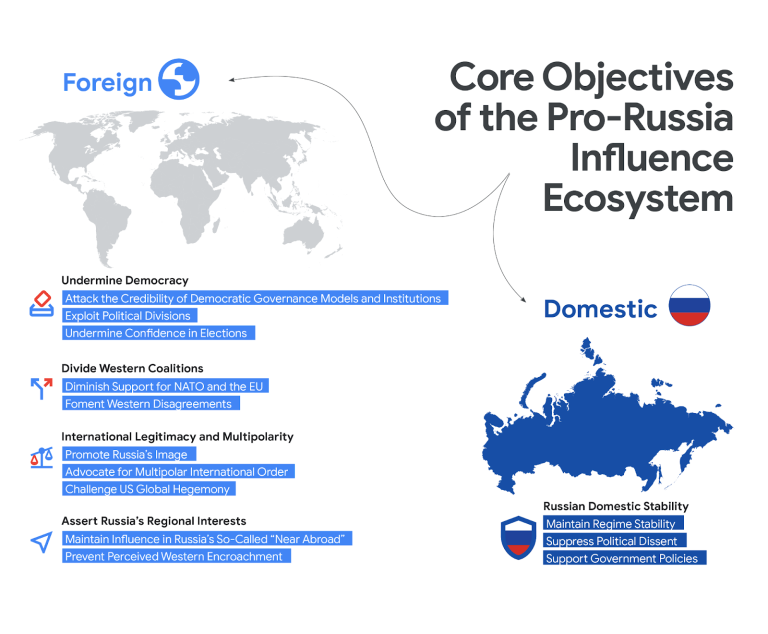
Pro-Russia Influence Ecosystem Expands Global Reach Diagram showing the pro-Russia influence ecosystem and information operations
  • Cybercriminals

Pro-Russia Influence Ecosystem Expands Global Reach

Do Son July 2, 2026 0

The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.
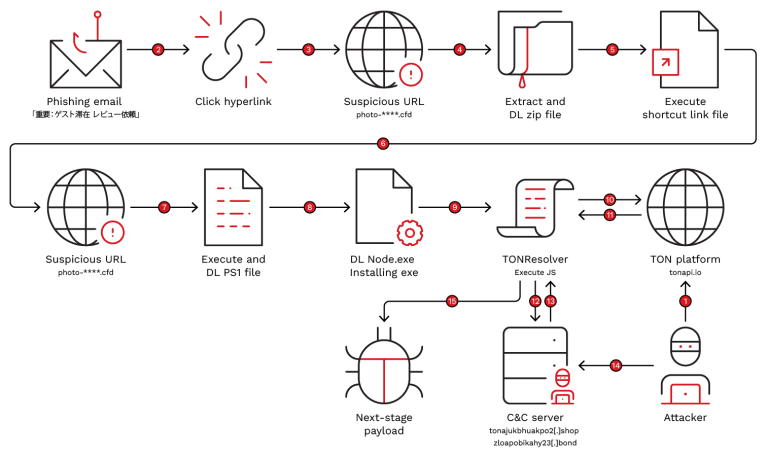
TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners TONResolver malware infection chain using a TON blockchain dead drop resolver against Booking.com hotel partners
  • Malware

TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners

Do Son July 2, 2026 0

Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.

Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution IBM Db2 RCE flaw CVE-2026-10109 from pre-auth DRDA handshake remote code execution
  • Vulnerability Report

Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution

Do Son July 2, 2026 0

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

Actively Exploited SharePoint Vulnerability Added to CISA KEV Catalog Actively exploited SharePoint vulnerability CVE-2026-45659 enabling remote code execution, added to CISA KEV
  • Vulnerability Report

Actively Exploited SharePoint Vulnerability Added to CISA KEV Catalog

Do Son July 2, 2026 0

CISA flags an actively exploited SharePoint vulnerability (CVE-2026-45659) enabling remote code execution. Patch SharePoint Server 2016 now.
Scattered Spider Arrest: Teen Extradited in $100M Scheme Scattered Spider arrest suspect Peter Stokes extradition
  • Cybercriminals

Scattered Spider Arrest: Teen Extradited in $100M Scheme

Do Son July 2, 2026 0

Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.

Cisco Patches Catalyst Center File Read Flaw and Seven ClamAV DoS Bugs Cisco Catalyst Center vulnerability and ClamAV vulnerabilities July 2026 patch advisory
  • Vulnerability Report

Cisco Patches Catalyst Center File Read Flaw and Seven ClamAV DoS Bugs

Do Son July 2, 2026 0

Cisco fixes a Cisco Catalyst Center vulnerability (CVE-2026-20191, CVSS 7.5) and seven ClamAV vulnerabilities causing DoS in Secure Endpoint Connectors.
Poweradmin Host Header Injection Lets Attackers Hijack DNS Accounts Poweradmin host header injection flaw CVE-2026-54588 enabling DNS admin account takeover
  • Vulnerability Report

Poweradmin Host Header Injection Lets Attackers Hijack DNS Accounts

Do Son July 2, 2026 0

A critical Poweradmin host header injection flaw (CVE-2026-54588) lets attackers hijack DNS admin accounts. Update to 4.2.4 or 4.3.3 now.

OpenAM WebAuthn Flaw Allows Remote Code Execution via Deserialization OpenAM WebAuthn RCE flaw CVE-2026-45051 from Java deserialization in access management
  • Vulnerability Report

OpenAM WebAuthn Flaw Allows Remote Code Execution via Deserialization

Do Son July 2, 2026 0

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.

Hardcoded Key Enables Authentication Bypass in NetComm NF20MESH Routers NetComm authentication bypass using a hardcoded AES key to forge admin cookies
  • Vulnerability Report

Hardcoded Key Enables Authentication Bypass in NetComm NF20MESH Routers

Do Son July 2, 2026 0

A NetComm authentication bypass (CVE-2026-35019, CVSS 9.2) uses a hardcoded AES key to forge admin session cookies. Update to firmware R6B032 now.
WinRAR Vulnerability Causes Heap Overflow in RAR5 Recovery Volumes WinRAR vulnerability CVE-2026-14191 causing a heap overflow in the RAR5 recovery volume parser
  • Vulnerability Report

WinRAR Vulnerability Causes Heap Overflow in RAR5 Recovery Volumes

Do Son July 2, 2026 0

A WinRAR vulnerability (CVE-2026-14191) causes a heap overflow via crafted .rev recovery files. Update WinRAR and UnRAR to version 7.23 now.

JetBrains Patches CVSS 10 Authentication Bypass Affecting 15 Million Developers JetBrains authentication bypass vulnerability CVE-2026-50242 affecting JetBrains Hub developers
  • Vulnerability Report

JetBrains Patches CVSS 10 Authentication Bypass Affecting 15 Million Developers

Do Son July 2, 2026 0

JetBrains patched a CVSS 10 authentication bypass and two more flaws (CVE-2026-50242). Its tools reach 15M developers. Update JetBrains Hub now.
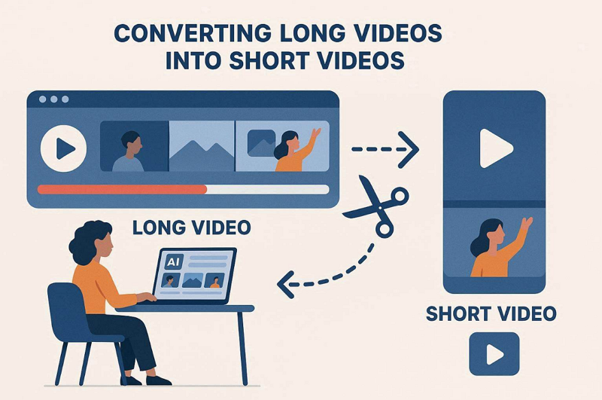
How to Convert a Long Video to a Short Video Guide long
  • Technique

How to Convert a Long Video to a Short Video Guide

Shahid Latif July 2, 2026 0
Sometimes, a story lasts for hours, but many viewers prefer only a short highlight. Therefore, turning a...
Read More Read more about How to Convert a Long Video to a Short Video Guide
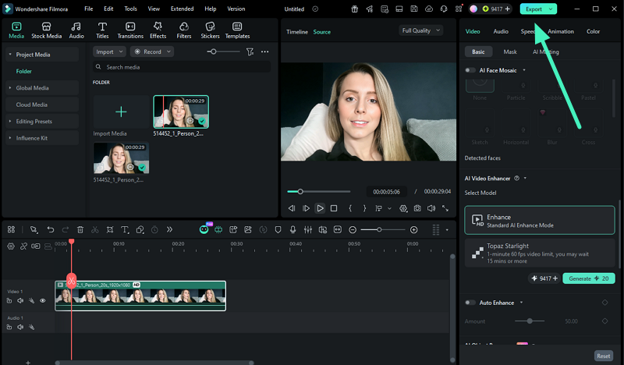
[Top Rated] AI Video Enhancer For Video Upscale step3
  • Technique

[Top Rated] AI Video Enhancer For Video Upscale

Shahid Latif July 2, 2026 0
A content creator opens an old project file, only to find blurry footage and pixelated clips that...
Read More Read more about [Top Rated] AI Video Enhancer For Video Upscale
The Rise of the CCTV Tower: How Elevated Surveillance Is Reshaping Modern Security Clearway-inView-CCTV-Tower
  • Technique

The Rise of the CCTV Tower: How Elevated Surveillance Is Reshaping Modern Security

Do Son July 2, 2026 0
Walk through any city center, industrial park, or large residential complex today, and you’ll likely notice tall,...
Read More Read more about The Rise of the CCTV Tower: How Elevated Surveillance Is Reshaping Modern Security
NVIDIA Security Updates Fix Critical Device Vulnerabilities NVIDIA security updates for ConnectX mitigating CVE-2025-23351
  • Vulnerability Report

NVIDIA Security Updates Fix Critical Device Vulnerabilities

Do Son July 1, 2026 0

Recent NVIDIA security updates address critical vulnerabilities, including CVE-2025-23351. Apply patches to secure your ConnectX and BlueField devices.
Kemp LoadMaster RCE Vulnerability Exploited in the Wild After Public PoC Release Kemp LoadMaster RCE vulnerability CVE-2026-8037 warning graphic
  • Vulnerability Report

Kemp LoadMaster RCE Vulnerability Exploited in the Wild After Public PoC Release

Do Son July 1, 2026 0

Attackers now target the Kemp LoadMaster RCE vulnerability (CVE-2026-8037) using a public PoC. Patch to 7.2.63.2 or 7.2.54.18 immediately.

Turning Indicators into Intelligence in OpenCTI with Criminal IP OpenClaw_Part_II_The_Growing_Security_Risks_Behind_1782355030QoWU2e1jD5
  • Press Release

Turning Indicators into Intelligence in OpenCTI with Criminal IP

cybernewswire July 1, 2026 0
Torrance, California, USA, 1st July 2026, CyberNewswire
Read More Read more about Turning Indicators into Intelligence in OpenCTI with Criminal IP
Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection 04_NetworkDDoS_1782900896ZXxW8F2biG
  • Press Release

Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection

cybernewswire July 1, 2026 0
Frankfurt am Main, Deutschland, 1st July 2026, CyberNewswire
Read More Read more about Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection
Android 17 Rate Limiting Blocks PIN Guessing Android 17 rate limiting PIN lockout screen Google I/O 2026 highlights
  • Android

Android 17 Rate Limiting Blocks PIN Guessing

Do Son July 1, 2026 0

Android 17 rate limiting drastically cuts PIN attempts, making stolen phones far harder to unlock by guesswork.

Anthropic Overcomes Export Restrictions: Mythos and Fable Models Restored Anthropic AI export ban lifted for Mythos and Fable models
  • Technology

Anthropic Overcomes Export Restrictions: Mythos and Fable Models Restored

Do Son July 1, 2026 0

The US Commerce Department lifts the Anthropic AI export ban, restoring access to Mythos and Fable models after sweeping national security compromises.
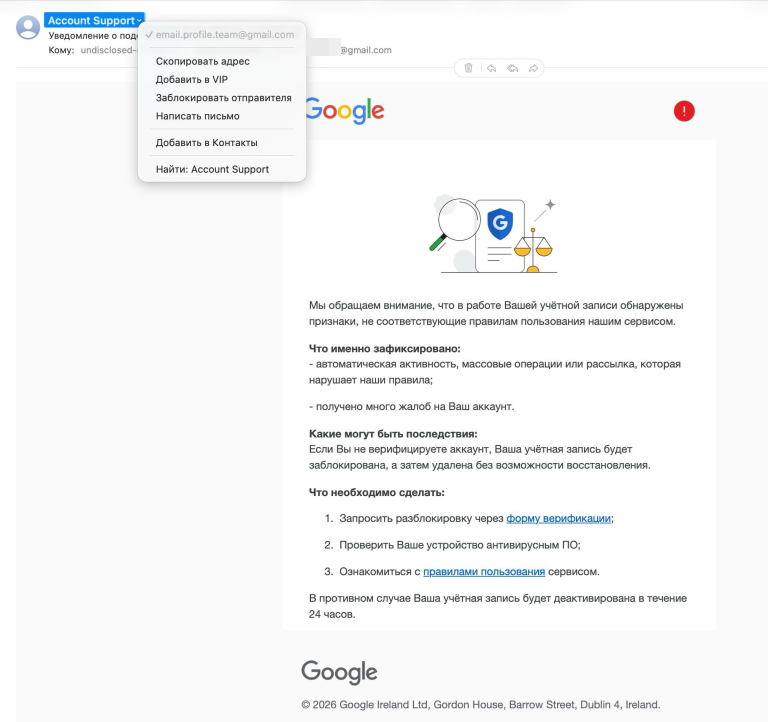
UNC1151 Phishing Campaign Targets Belarus and Ukraine UNC1151 phishing campaign login page created by the Ghostwriter threat actor.
  • Cybercriminals

UNC1151 Phishing Campaign Targets Belarus and Ukraine

Do Son July 1, 2026 0

A suspected UNC1151 phishing campaign targets Belarusian politicians and Ukrainian portals to steal credentials using deceptive login pages.

Claude Code Telemetry Rollback: Anthropic Responds to Backdoor Allegations Anthropic Claude Code telemetry rollback response and developer community controversy Claude Code human error Claude AI Data Wipe, Constraining AI Tools Anthropic lawsuit, AI copyright Claude Code, web editor
  • Technology

Claude Code Telemetry Rollback: Anthropic Responds to Backdoor Allegations

Do Son July 1, 2026 0

Anthropic announces a Claude Code telemetry rollback following intense developer backlash over hidden location tracking and proxy detection code.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120447CVSS 9.2
    HotGo 2.8.4 through 2.15.1 contains an authentication bypass vulnerability that allows unauthenticated attackers to choose the SMS login...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29073CVSS 9.8
    A maliciously crafted MODEL file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29074CVSS 9.8
    A maliciously crafted CATPART file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2026-77526CVSS 9.9
    ## Summary `FacturaScripts\Core\UploadedFile::move($destiny, $destinyName)` concatenates `$destiny` and `$destinyName` without normalizing the resulting path. Every caller in the codebase...
    📅 Updated: Nov 2, 2026
  • CVE-2026-45262CVSS 9.9
    ## Summary > **Live PoC verified 2026-04-30** against a stock FacturaScripts master at `127.0.0.1:8081`. A scoped `ApiKey` with...
    📅 Updated: Nov 2, 2026
  • CVE-2026-86596CVSS 9.8
    The s2Member plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including,
    📅 Updated: Nov 2, 2026
  • CVE-2026-76407CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
  • CVE-2026-76528CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.