Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
DirtyClone Linux Kernel Flaw Lets Local Users Get Root DirtyClone Linux kernel privilege escalation flaw CVE-2026-43503 page cache exploit
  • Vulnerability Report

DirtyClone Linux Kernel Flaw Lets Local Users Get Root

Do Son June 28, 2026 0

DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.

GPT-5.6 Sol Model Launched Amid Strict Security Reviews GPT-5.6 Sol model capabilities and AI cybersecurity impact
  • Technology

GPT-5.6 Sol Model Launched Amid Strict Security Reviews

Do Son June 28, 2026 0

Discover the GPT-5.6 Sol model launch. OpenAI introduces Terra and Luna tiers while navigating strict US cybersecurity reviews and a restricted preview.

Claude Mythos 5 Returns: US Government Lifts AI Ban Claude Mythos 5 AI cybersecurity model unbanned by US government
  • Technology

Claude Mythos 5 Returns: US Government Lifts AI Ban

Do Son June 28, 2026 0

Anthropic's powerful Claude Mythos 5 cybersecurity AI model returns following a strict US government ban. Discover the impact on Silicon Valley.
libssh2 Vulnerability CVE-2026-58050 Gets Public PoC Exploit libssh2 vulnerability CVE-2026-58050 publickey subsystem heap buffer overflow PoC exploit
  • Vulnerability Report

libssh2 Vulnerability CVE-2026-58050 Gets Public PoC Exploit

Do Son June 28, 2026 0

Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
CPython Tarfile Vulnerability Exposes Systems Diagram explaining the CPython tarfile vulnerability and CVE-2026-11940 bypass
  • Vulnerability Report

CPython Tarfile Vulnerability Exposes Systems

Do Son June 28, 2026 0

A new CPython tarfile vulnerability (CVE-2026-11940) allows directory escape attacks. Learn how this extraction filter bypass exposes systems.

US Seizes Domains to Stop Illegal World Cup Streaming Law enforcement officials announce domain seizures to stop illegal World Cup streaming.
  • Cybercriminals

US Seizes Domains to Stop Illegal World Cup Streaming

Do Son June 27, 2026 0

US authorities halted illegal World Cup streaming via nearly 400 domain seizures. Discover how Operation Offsides protects viewers from malware.
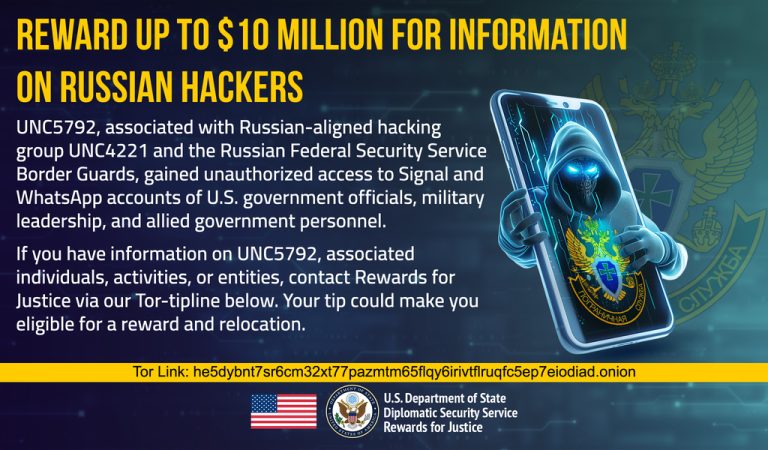
US Offers $10 Million Reward for Russian Hacker Group UNC5792 UNC5792 Rewards for Justice $10 million reward Russian Signal phishing group
  • Cybercriminals

US Offers $10 Million Reward for Russian Hacker Group UNC5792

Do Son June 27, 2026 0

The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
Mistic Backdoor Linked to Ransomware Access Broker Mistic backdoor malware and ransomware access broker diagram
  • Malware

Mistic Backdoor Linked to Ransomware Access Broker

Do Son June 27, 2026 0

A new Mistic backdoor malware campaign linked to a ransomware access broker targets multiple sectors. Learn how this stealthy threat evades detection.
Langflow Cryptominer Malware Exploits CVE-2026-33017 Trojanized streaming site causing Packagist themes iOS spyware infections
  • Malware

Langflow Cryptominer Malware Exploits CVE-2026-33017

Do Son June 27, 2026 0

A new Langflow cryptominer malware campaign exploits CVE-2026-33017 to deploy malicious payloads. Learn how this threat spreads and how to stay protected.
Cisco SD-WAN Zero-Day Exploited in Attacks Diagram explaining the Cisco SD-WAN zero-day and CVE-2026-20245 exploitation
  • Cybercriminals

Cisco SD-WAN Zero-Day Exploited in Attacks

Do Son June 26, 2026 0

A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.

Windows 10 Extended Security Updates Prolonged to 2027 Illustration of the Microsoft Windows 10 extended security updates timeline stretching to October 2027
  • Technology

Windows 10 Extended Security Updates Prolonged to 2027

Do Son June 26, 2026 0

Discover how Microsoft silently prolonged Windows 10 extended security updates for consumers to October 2027, mirroring Firefox's legacy support strategy.

WhatsApp Malware Campaign Spreads RMM Software Diagram showing the WhatsApp malware campaign and VBScript infection chain
  • Cybercriminals

WhatsApp Malware Campaign Spreads RMM Software

Do Son June 26, 2026 0

A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.

Fake Shop Campaigns Target Europe Fake shop campaigns selling counterfeit goods in Europe
  • Cybercriminals

Fake Shop Campaigns Target Europe

Do Son June 26, 2026 0

Researchers uncovered massive fake shop campaigns targeting Europe. Attackers sell counterfeit goods by impersonating major brands and exploiting World Cup.

FOSSBilling Template Injection Flaw Exploited in the Wild Nextcloud website hacked showing unauthorized Cloudbox phishing redirect and wp2shell vulnerability.
  • Vulnerability Report

FOSSBilling Template Injection Flaw Exploited in the Wild

Do Son June 26, 2026 0

A FOSSBilling template injection flaw (CVE-2026-28496, CVSS 9.4) is exploited in the wild. Patch to 0.8.0 now to stop server-side template injection.

OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads

Do Son June 26, 2026 0

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
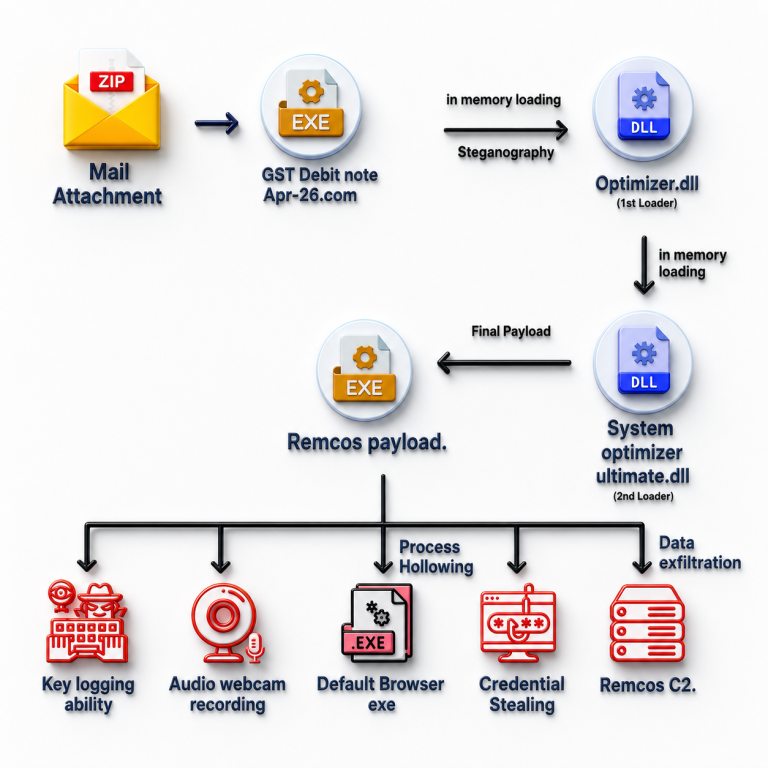
Remcos RAT Delivered by a Steganographic Loader in Phishing Emails Remcos RAT delivered by a steganographic loader hidden in a bitmap image
  • Malware

Remcos RAT Delivered by a Steganographic Loader in Phishing Emails

Do Son June 26, 2026 0

A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

Python Patches python.org API Authentication Bypass Flaw python.org authentication bypass affecting Python release metadata and download API
  • Vulnerability Report

Python Patches python.org API Authentication Bypass Flaw

Do Son June 26, 2026 0

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.

Curl v8.21.0 Release Fixes 18 Security Flaws Graphic illustrating the massive curl v8.21.0 release patching 18 security vulnerabilities globally
  • Vulnerability Report

Curl v8.21.0 Release Fixes 18 Security Flaws

Do Son June 26, 2026 0

Discover the massive curl v8.21.0 release featuring 18 security patches, many identified by AI models. Upgrade now for enhanced safety and HTTP/3 capabilities.

The Rumored Claude Fable 5 Return: UI Glitch or Reality? Claude Fable 5 return UI glitch interface on Anthropic platform
  • Technology

The Rumored Claude Fable 5 Return: UI Glitch or Reality?

Do Son June 26, 2026 0

Discover the truth behind the Claude Fable 5 return rumors. Learn how a recent UI glitch and AWS updates hint at an imminent launch for this powerful AI.

Apple Price Increase Hits Macs, iPads, and Vision Pro Apple price increase chart showing higher Mac iPad and Vision Pro prices driven by the AI memory shortage Vision Pro M5, Dual Knit Band
  • Technology

Apple Price Increase Hits Macs, iPads, and Vision Pro

Do Son June 26, 2026 0

The Apple price increase raises Mac, iPad, HomePod, Apple TV, and Vision Pro prices on the memory shortage. iPhone, Watch, and AirPods are spared.
CISA Adds Cisco Unified CM and PTC Windchill Flaws to KEV Catalog CISA KEV Catalog adding CVE-2026-20230 Cisco Unified CM and CVE-2026-12569 PTC Windchill vulnerabilities
  • Vulnerability Report

CISA Adds Cisco Unified CM and PTC Windchill Flaws to KEV Catalog

Do Son June 26, 2026 0

CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.

Public Exploits Released for Three Gogs RCE Flaws, CVSS Up to 10 Gogs RCE vulnerability with public proof-of-concept exploit code, CVSS up to 10
  • Vulnerability Report

Public Exploits Released for Three Gogs RCE Flaws, CVSS Up to 10

Do Son June 26, 2026 0

Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.