Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Chrome Security Update Patches Three High-Severity Browser Flaws Chrome security update patching CVE-2026-13281 and other Chrome 149 vulnerabilities
  • Vulnerability Report

Chrome Security Update Patches Three High-Severity Browser Flaws

Do Son June 26, 2026 0

Google's Chrome security update patches three high-severity flaws in Mojo, Payments, and AdFilter. Update to 149.0.7827.200 now to stay protected.
FFmpeg MagicYUV Vulnerability Exposes Media Applications Diagram explaining the FFmpeg MagicYUV vulnerability and CVE-2026-8461 exploit flow
  • Vulnerability Report

FFmpeg MagicYUV Vulnerability Exposes Media Applications

Do Son June 26, 2026 0

A critical FFmpeg MagicYUV vulnerability (CVE-2026-8461) allows attackers to achieve remote code execution via crafted media files. Patch systems quickly.
Langflow Security Vulnerabilities Expose AI Systems Diagram of Langflow security vulnerabilities CVE-2026-55255 CVE-2026-55447 CVE-2026-55450
  • Vulnerability Report

Langflow Security Vulnerabilities Expose AI Systems

Do Son June 26, 2026 0

Three critical Langflow security vulnerabilities (CVE-2026-55255, CVE-2026-55447, CVE-2026-55450) expose AI applications to RCE and DoS attacks. Patch now.

Critical Event-Driven Ansible Flaw Leaks Stored Credentials Event-Driven Ansible flaw causing credential disclosure of tokens and SSH keys
  • Vulnerability Report

Critical Event-Driven Ansible Flaw Leaks Stored Credentials

Do Son June 26, 2026 0

A missing authorization flaw in Event-Driven Ansible (CVE-2026-11807, CVSS 9.6) leaks credentials like OAuth tokens, vault passwords, and SSH keys.

Google Play Billing Structure Evolves for App Developers Illustration of the updated Google Play billing structure and alternative payment choices for app developers
  • Technology

Google Play Billing Structure Evolves for App Developers

Do Son June 25, 2026 0

Discover the new Google Play billing structure and fee changes. Learn how eligible developers can use alternative payment systems and reduce platform fees.

Siri Restricts External URL Summarization in iOS 27 Beta Siri AI system prompt Siri AI iOS 27 Apple Siri URL summarization restriction interface in the iOS 27 beta update
  • Technology

Siri Restricts External URL Summarization in iOS 27 Beta

Do Son June 25, 2026 0

Discover why Apple restricts Siri URL summarization in iOS 27. Learn about the new security controls, prompt injection protection, and web traffic impacts.

The True Cost of Artificial Intelligence: Enterprises Impose Restrictions Concept visualization illustrating skyrocketing enterprise AI tools operational costs and token restrictions
  • Technology

The True Cost of Artificial Intelligence: Enterprises Impose Restrictions

Do Son June 25, 2026 0

Discover why global enterprises are restricting enterprise AI tools due to soaring token costs and inefficient usage by non-technical staff.

Apache Kvrocks Vulnerabilities Fix Five Severe Flaws Diagram illustrating Apache Kvrocks vulnerabilities and NoSQL database flaws
  • Vulnerability Report

Apache Kvrocks Vulnerabilities Fix Five Severe Flaws

Do Son June 25, 2026 0

Five Apache Kvrocks vulnerabilities, including CVSS 10 NoSQL database flaws, expose servers to DoS and overflow attacks. Patch to version 2.16.0 now.

AutoJack AI Agent Exploit Unveiled code
  • Vulnerability Report

AutoJack AI Agent Exploit Unveiled

Do Son June 25, 2026 0

Discover the AutoJack AI agent exploit! We explore the AutoGen Studio vulnerability that allows remote code execution via local MCP WebSockets.

Windows Crypto Clipper Malware Exposed North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

Windows Crypto Clipper Malware Exposed

Do Son June 25, 2026 0

Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.

GitLab Security Updates Fix 13 Flaws GitLab security updates protecting repositories from vulnerabilities
  • Vulnerability Report

GitLab Security Updates Fix 13 Flaws

Do Son June 25, 2026 0

GitLab released critical security updates addressing 13 vulnerabilities, including severe cross-site scripting and information disclosure flaws.

Jenkins Patches 22 Plugin Vulnerabilities, Five Flaws Remain Unfixed Jenkins plugin vulnerabilities enabling sandbox bypass and remote code execution
  • Vulnerability Report

Jenkins Patches 22 Plugin Vulnerabilities, Five Flaws Remain Unfixed

Do Son June 25, 2026 0

A new Jenkins advisory fixes 22 plugin vulnerabilities, including a Script Security sandbox bypass that enables RCE. Five flaws have no fix yet.
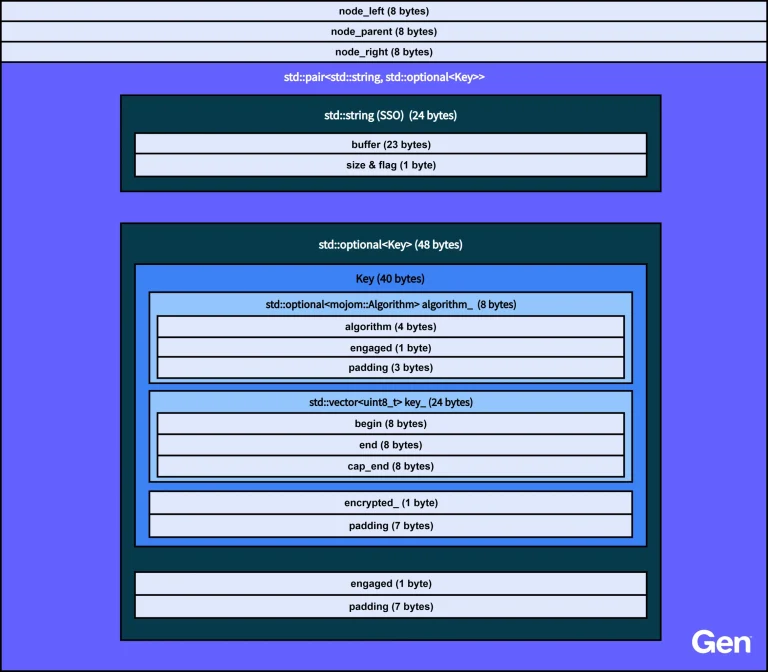
Vidar ABE Bypass Technique Steals Browser Keys Vidar ABE bypass technique flowchart showing how Vidar infostealer malware extracts keys
  • Malware

Vidar ABE Bypass Technique Steals Browser Keys

Do Son June 25, 2026 0

Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.
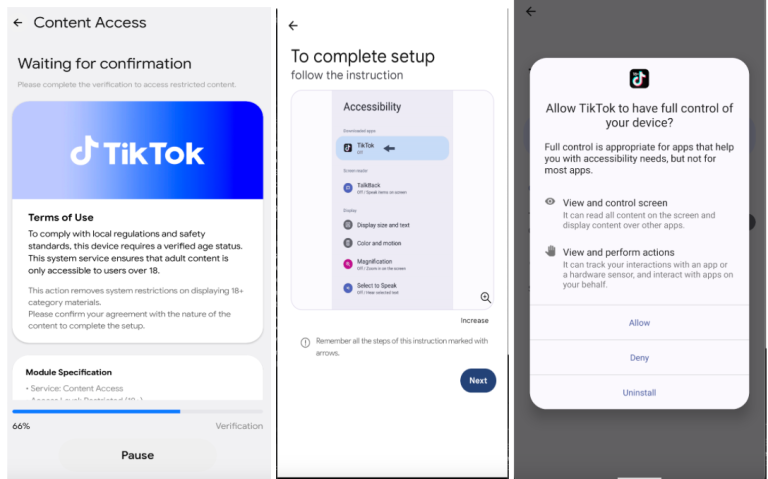
Rokarolla Android Banking Trojan Steals Financial Data Rokarolla Android banking trojan executing a device takeover
  • Malware

Rokarolla Android Banking Trojan Steals Financial Data

Do Son June 25, 2026 0

The Rokarolla Android banking trojan executes a complete device takeover. It targets 217 apps and steals credentials through fake overlays and keyloggers.

Gemini for Chrome Adds Select from Screen to Read the Page Gemini for Chrome Select from Screen tool highlighting text and images on a webpage to attach to a prompt
  • Technology

Gemini for Chrome Adds Select from Screen to Read the Page

Do Son June 25, 2026 0

Gemini for Chrome adds Select from Screen, letting you box specific text or images on a page and attach them straight to your prompt.

Google Gemini 3.5 Flash Introduces Computer Use Capabilities Google Gemini 3.5 Flash executing the Computer Use tool to automate graphical interface tasks
  • Technology

Google Gemini 3.5 Flash Introduces Computer Use Capabilities

Do Son June 25, 2026 0

Explore Google Gemini 3.5 Flash introducing the Computer Use feature for developers. Learn about GUI automation capabilities and adversarial safety controls.

ManageEngine Account Takeover Flaw CVE-2026-11374 ManageEngine account takeover diagram explaining CVE-2026-11374 SSO ticket prediction
  • Vulnerability Report

ManageEngine Account Takeover Flaw CVE-2026-11374

Do Son June 25, 2026 0

A critical ManageEngine account takeover vulnerability (CVE-2026-11374) exposes AD360 integrated deployments to unauthenticated attacks. Update systems now.
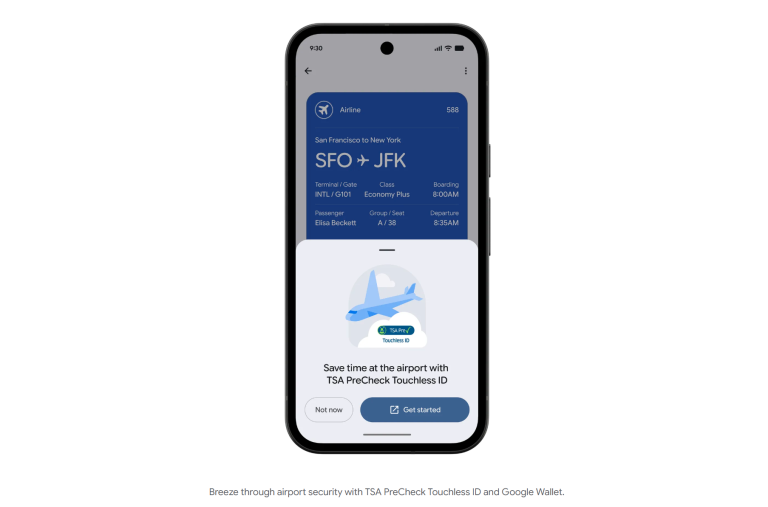
Google Wallet TSA PreCheck Touchless ID Now Covers 100 Airlines Google Wallet TSA PreCheck Touchless ID boarding pass badge for facial comparison at airport security lanes
  • Technology

Google Wallet TSA PreCheck Touchless ID Now Covers 100 Airlines

Do Son June 25, 2026 0

Google Wallet TSA PreCheck Touchless ID now covers 100+ airlines with a one-time opt-in. Skip the document check at 65 airports nationwide.

Ubuntu Livepatch Now Supports Arm64 for Rebootless Kernel Updates Ubuntu Livepatch Arm64 support applying rebootless Linux kernel security updates on Ubuntu Core 26 servers Ubuntu 26.10 release
  • Linux

Ubuntu Livepatch Now Supports Arm64 for Rebootless Kernel Updates

Do Son June 25, 2026 0

Ubuntu Livepatch now supports Arm64, applying critical kernel security updates with no reboot on Ubuntu Core 26 and Ubuntu 26.04 LTS.

The Evolution of Collaboration: Anthropic’s Claude Tag in Slack Anthropic Claude Tag in Slack interface demonstrating proactive AI colleague interactions
  • Technology

The Evolution of Collaboration: Anthropic’s Claude Tag in Slack

Do Son June 25, 2026 0

Explore how Anthropic's Claude Tag in Slack transforms AI from a passive tool into a proactive, memory-equipped virtual colleague for enterprise teams.

Laravel Livewire Vulnerability Exposes Over 6,000 Apps Diagram showing the Laravel Livewire vulnerability and CVE-2025-54068 exploit flow
  • Cybercriminals

Laravel Livewire Vulnerability Exposes Over 6,000 Apps

Do Son June 25, 2026 0

A suspected Indonesian threat actor exploited the Laravel Livewire vulnerability (CVE-2025-54068) to steal credentials from over 6,000 web applications.

Operation Endgame Takes Down SocGholish, Amadey, and StealC Malware Operation Endgame takedown disrupting the SocGholish malware network
  • Cybercriminals

Operation Endgame Takes Down SocGholish, Amadey, and StealC Malware

Do Son June 25, 2026 0

Operation Endgame disrupts the SocGholish malware network, seizing EUR 41M in crypto and 326 servers. WordPress site owners must act now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.