 Do Son
GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
AI security
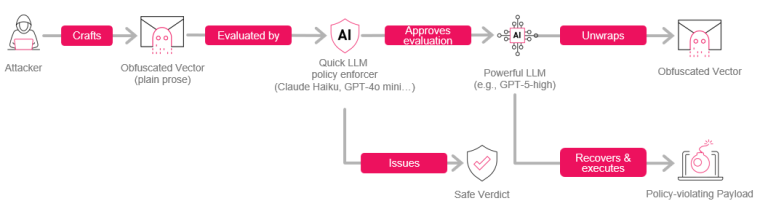
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
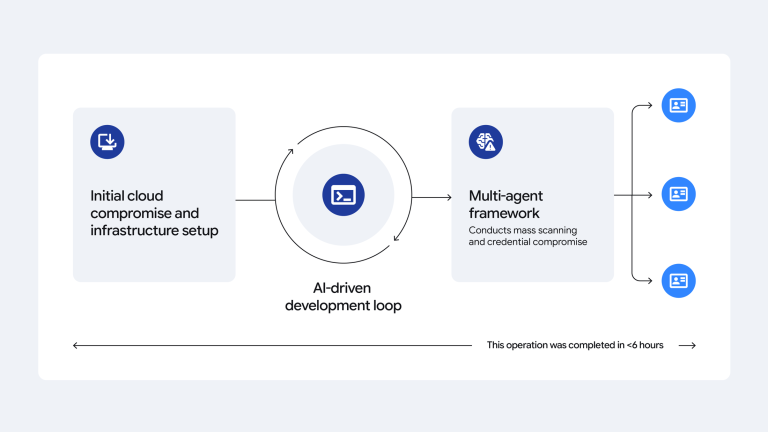
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
A METR security breach saw a stolen API key burn about $600K in AI credits after a vibe-coded dashboard failed open and exposed an agent panel online.

NVIDIA Triton vulnerability CVE-2026-47627 scores CVSS 9.8. Learn how the denial of service flaw works and why you must update to 26.06 now.

A public PoC for CVE-2026-64849, an unauthenticated MLflow SSRF (CVSS 9.3), is now live. watchTowr reports exploitation attempts. Patch to 3.15.0.
Unit 42 exposed an autonomous AI cyberattack by a Chinese threat actor using DeepSeek to scan, pivot, and exploit targets on its own.
Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.

Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.

An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".

Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.

The Hugging Face breach was driven end-to-end by an autonomous AI agent attack. Internal datasets and service credentials were exposed.

Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.
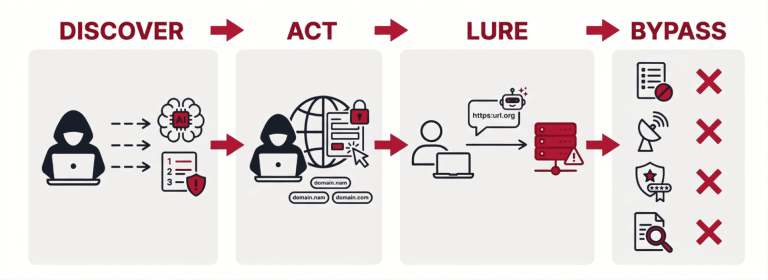
Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

Apple and Google form a rare alliance to block an EU mandate. Discover why Apple is fighting to stop third-party AI from accessing Android’s core architecture.
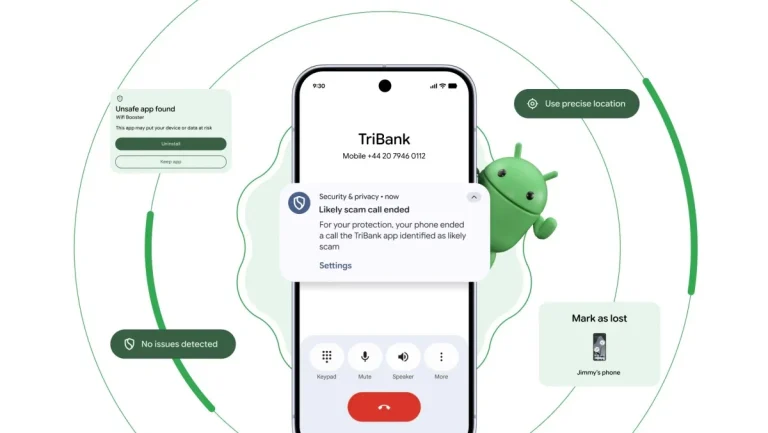
Google’s 2026 Android roadmap turns AI into a "Live Threat Detection" sentinel. Explore Android 17’s new anti-theft biometrics and banking fraud intercepts.
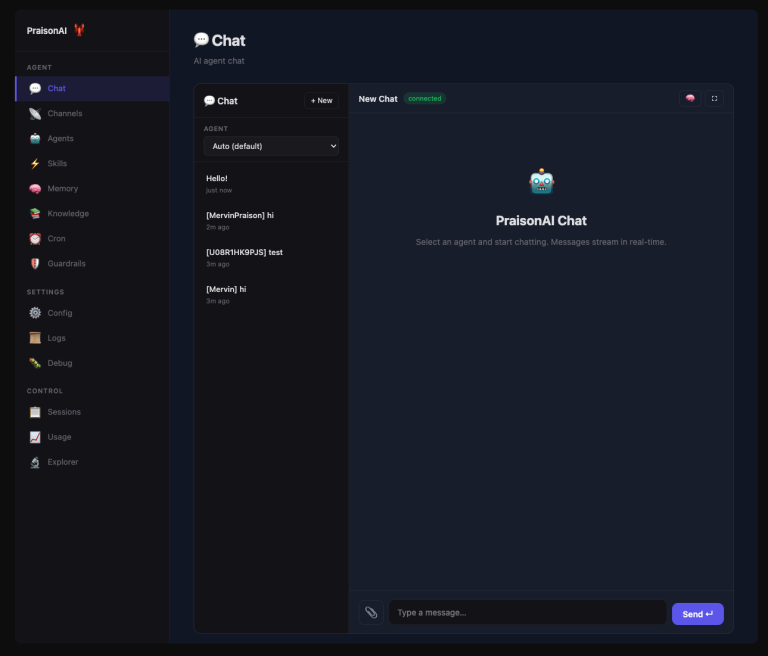
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
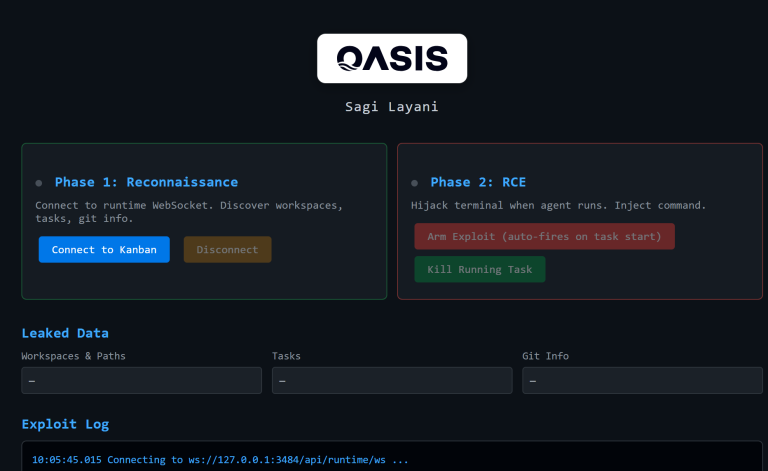
Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
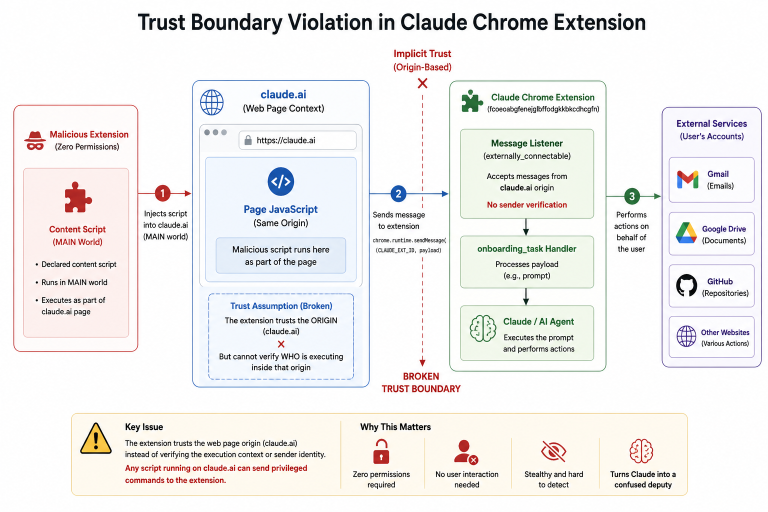
LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.