
 Do Son
Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.
AI security

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.

Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.

DomainTools unmasks a malicious "ChatGPT Ad Blocker" Chrome extension that steals private conversations and sends them to Discord. Check your extensions now!

The UK CMA is launching a "Strategic Market Status" probe into Microsoft in May 2026. Discover how AI and cloud bundling are under the regulatory microscope.

NVIDIA fixes high-severity flaws (CVE-2026-24164) in BioNeMo. Attackers could execute code or disrupt AI drug discovery. Update to commit e5e58c8 now.

Anthropic strikes back after the Claude Code leak, nuking 8,100 GitHub repos. But can you ever truly delete the internet's most wanted source code?
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.

Google Drive's AI now detects 14x more ransomware. Learn how to use the new "infallible temporal anchor" for one-click file restoration in March 2026.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

NVIDIA issues critical updates for Megatron-LM, Triton, and NeMo to fix RCE and DoS flaws. Upgrade now to secure your AI development and inference servers.

GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...

NVIDIA patches a critical 9.0 CVSS vulnerability (CVE-2025-33244) in the Apex library. Protect your AI models from RCE—upgrade to PyTorch 2.6+ now.
Mark Zuckerberg is building a "CEO Agent" to bypass corporate layers. Discover how Meta's new AI-to-AI conclaves are reshaping the future of management in 2026.
Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.

Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.

Critical 9.8 CVSS unpatched RCE flaws in the SGLang AI framework (CVE-2026-3059 & CVE-2026-3060) expose servers via unsafe Python pickle deserialization.
Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.
Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture

Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture
OpenAI has acquired AI security vanguard Promptfoo. Discover how this $86M deal will automate red-teaming and protect AI agents from prompt injection in 2026.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.
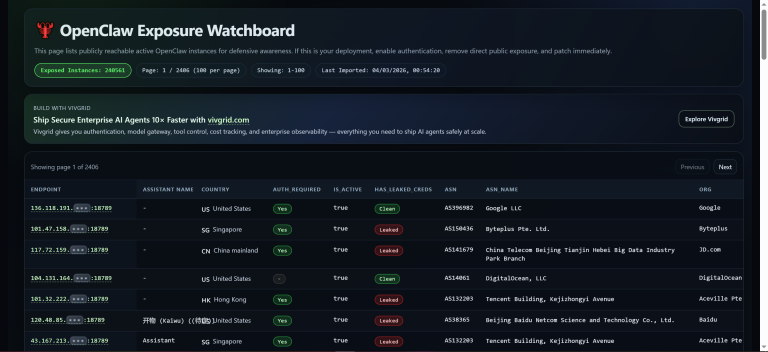
240,000 OpenClaw AI instances are currently exposed to the public internet. Learn how to secure your personal assistant before it becomes a portal for hackers.