
 Do Son
An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
AI security
Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft
Anthropic claims DeepSeek and other Chinese AI firms used 24,000 accounts to "pilfer" Claude's data. Inside the high-stakes battle for LLM training secrets.

Google's VP Vijaya Kaza reveals 1.75M bad apps blocked in 2025. Android 16 introduces one-line tapjacking protection to fight AI-powered cyber threats.

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.
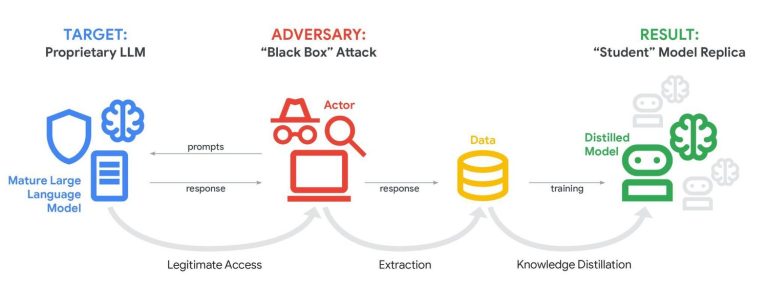
Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.
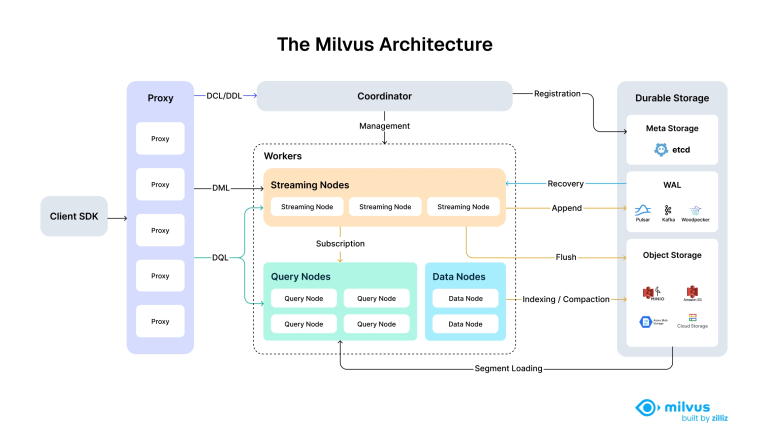
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

Microsoft warns of critical flaw CVE-2026-25592 (CVSS 10.0) in Semantic Kernel SDK. AI agents can overwrite system files. Update to v1.70.0 now.

Critical vLLM bug CVE-2026-22778 (CVSS 9.8) lets attackers hijack servers using malicious videos. Affects video model deployments. Patch to v0.14.1 now.

VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.

PyTorch patches CVE-2026-24747 (CVSS 8.8). The "weights_only" safety flag failed, allowing RCE via malicious models. Update to v2.10.0 now.

New Android anti-theft updates use AI to detect "snatch-and-run" theft and instantly lock your screen. Identity Check adds biometric layers to stop thieves.

A critical flaw in Clawdbot’s auth logic allows hackers to bypass security via reverse proxies. Over 1,000 instances are already exposed—is yours one of them?

Researchers found a flaw in Google Gemini allowing "Indirect Prompt Injection" via calendar invites to steal private meeting data. The issue is now mitigated.

NVIDIA fixes high-severity code injection flaws in Nsight Graphics and Merlin (CVE-2025-33206/33). Update to v2025.5 immediately to prevent compromise.

Microsoft patches "Reprompt," a critical Copilot flaw. Attackers could steal sensitive data with just one click on a legitimate link.

Critical OpenCode flaws (CVE-2026-22813) allow drive-by RCE via malicious sites. Update to v1.0.216 immediately to stop unauthorized command execution.
Critical ServiceNow AI flaw (CVE-2025-12420) allows unauthenticated user impersonation. Self-hosted users: update Now Assist & Virtual Agent immediately.

CVE-2025-67732 unmasks a high-severity flaw in Dify that exposes plaintext API keys to frontend users. Upgrade to v1.11.0 to secure your AI quotas.

OpenAI patches a new class of prompt injection in ChatGPT Atlas. See how the Agent mode is being hardened against hidden hijacks on the open web.