 Do Son
Protect your AI apps. Spring AI issues urgent patches for three critical vulnerabilities causing data destruction, memory poisoning, and user data leaks.
AI security
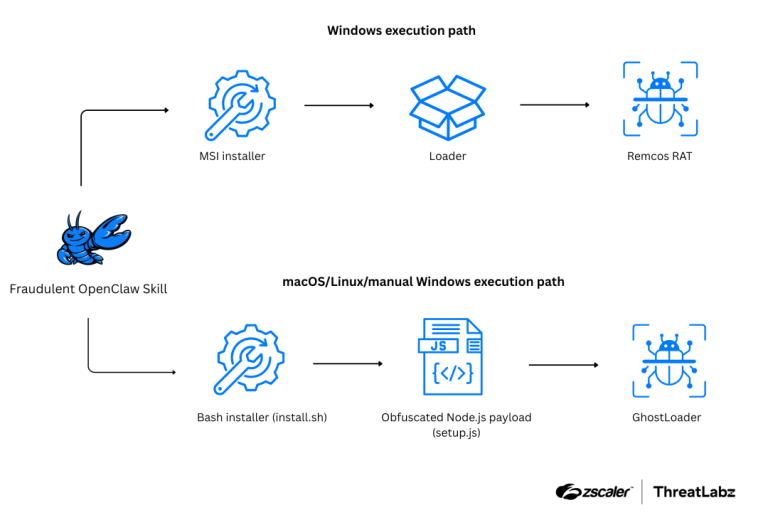
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.
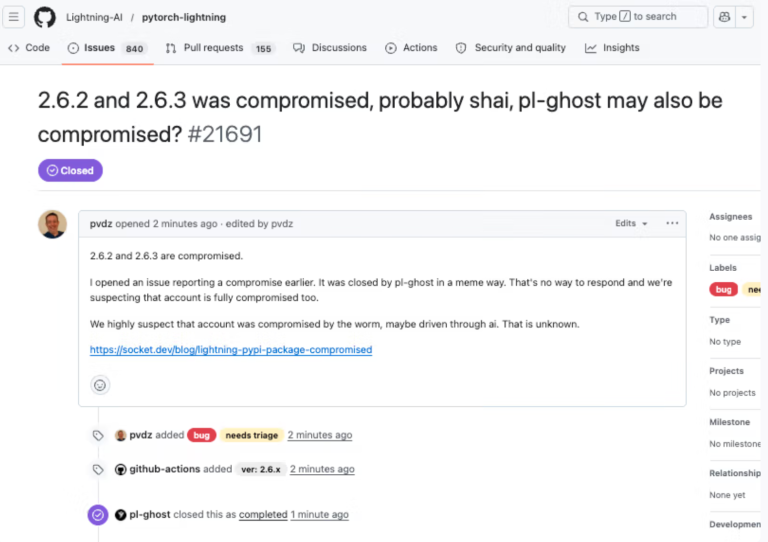
Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.

NVIDIA issued an urgent patch for a critical 9.8 CVSS flaw in the FLARE SDK. Stop unauthenticated RCE and data tampering. Upgrade to v2.7.2 immediately.
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.

Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.
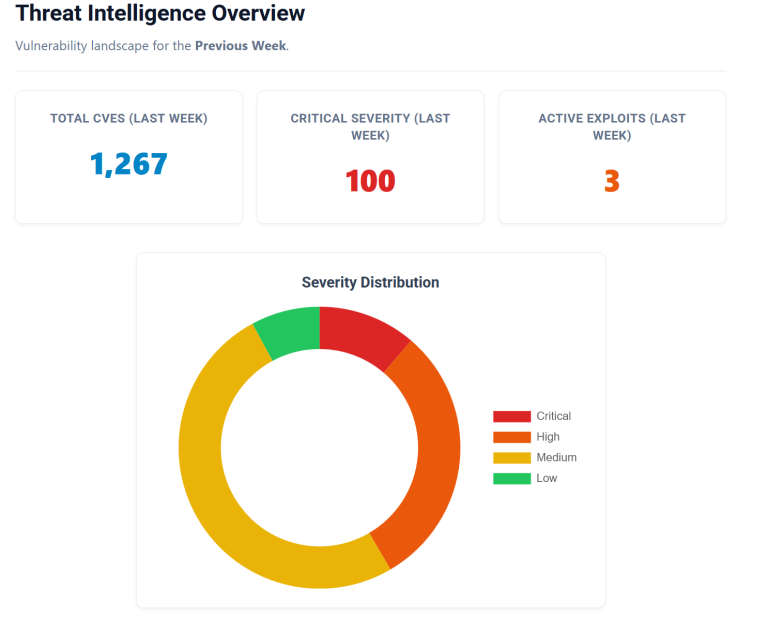
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.

Linux maintainers propose purging 27,646 lines of legacy network code to combat a flood of AI-generated vulnerability reports and focus on modern security.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.
CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.

SGLang faces a critical 9.8 CVSS RCE flaw (CVE-2026-5760). Malicious GGUF models can hijack AI servers via unsandboxed Jinja2 templates. Learn how to fix it.
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.
Google ADK (CVE-2026-4810) faces a critical 9.3 CVSS RCE flaw. Unauthenticated attackers can hijack AI agents on GKE & Cloud Run. Update and redeploy now!
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!
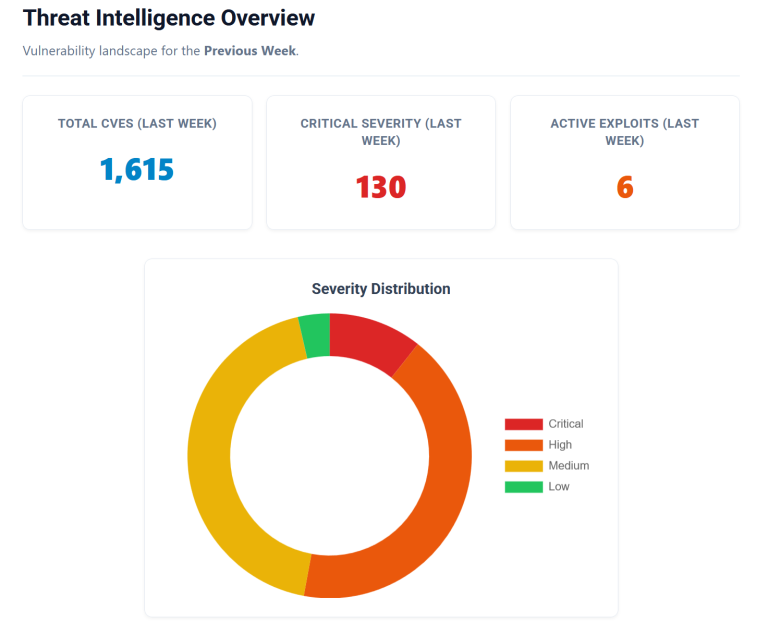
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.
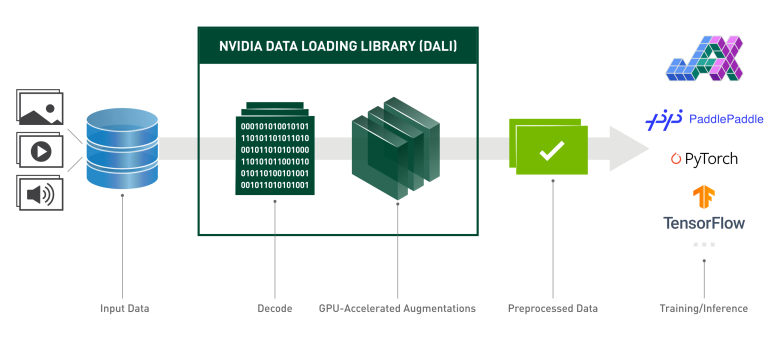
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.