 Do Son
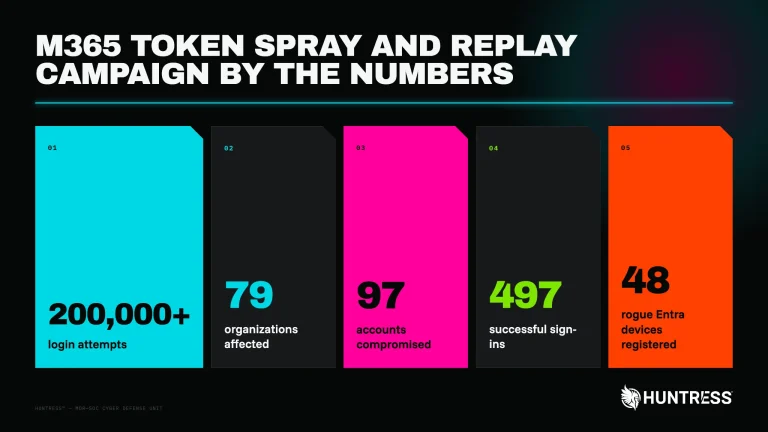
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
AitM Phishing
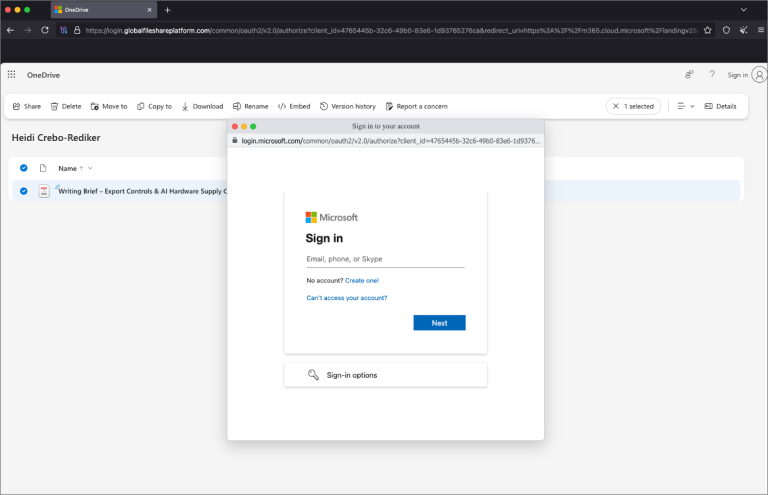
Proofpoint exposed China-aligned TA419 credential phishing targeting AI experts. This TA419 credential phishing campaign uses AitM lures to steal logins.
UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.
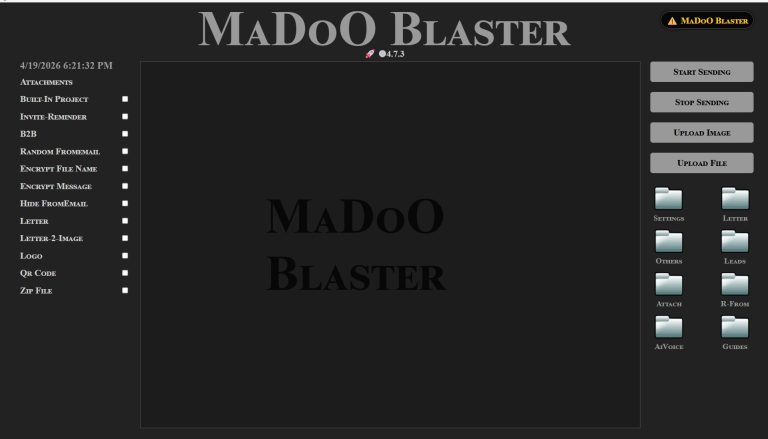
A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.
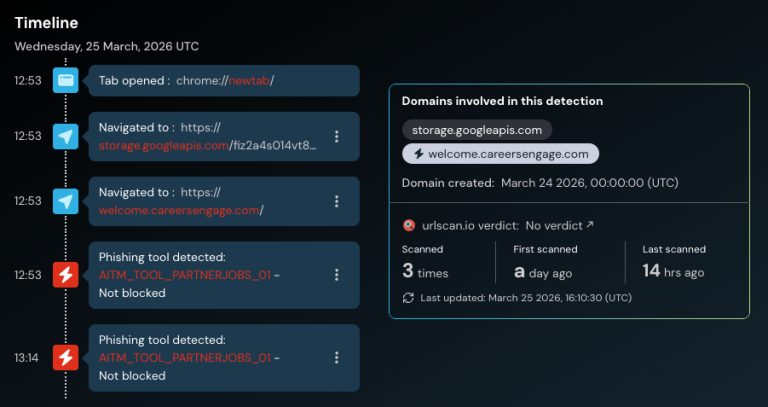
Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.
Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.
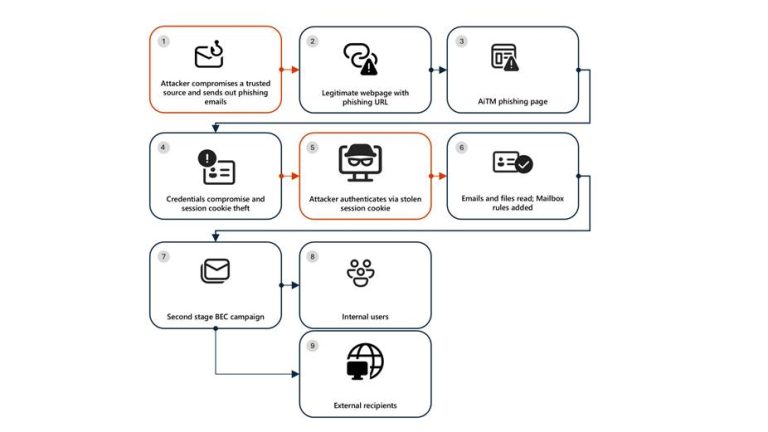
Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

Sekoia exposed Russian Calisto APT (FSB-linked) targeting RSF and NGOs with spear-phishing. The attack uses a custom AiTM kit and a "missing file" lure to steal credentials and 2FA codes.

A new Sekoia report reveals a surge in AitM phishing, leveraging industrialized PhaaS kits to bypass MFA and compromise Microsoft 365 and Google accounts.