 Do Son
IBM API Connect vulnerabilities: 208 flaws, including authentication bypass CVE-2026-17301 and hard-coded credentials. Apply IBM's fixes now.
API security
CERT/CC warns of a critical Xerj authentication bypass tracked as CVE-2026-97406 that lets attackers mint persistent tokens without passkeys.
A massive Sourcenext data breach exposed up to 22.5 million customer records via abused member APIs, prompting emergency company-wide password resets.
IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.

WSO2 patched seven flaws across API Manager and gateways, led by a CVSS 10 JWT auth bypass (CVE-2026-5430). Update WSO2 API Manager now.
A critical LiteLLM authentication bypass (CVE-2026-49468) lets crafted Host Header Injection reach protected AI Gateway routes. Patch in 1.84.0.

A critical Langflow file upload flaw (CVE-2026-55450) is public with a PoC, enabling unauthenticated denial-of-service and path disclosure. Patch 1.9.1.
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!
Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.

ClickUp discloses a configuration flaw exposing 893 emails and a live API token via Split.io feature flags. Learn how client-side SDKs became a public leak.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.

NVIDIA patches critical flaws in KAI Scheduler and CUDA-Q. CVE-2026-24189 and CVE-2026-24177 risk data leaks and DoS. Secure your GPU workloads—update today!

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.
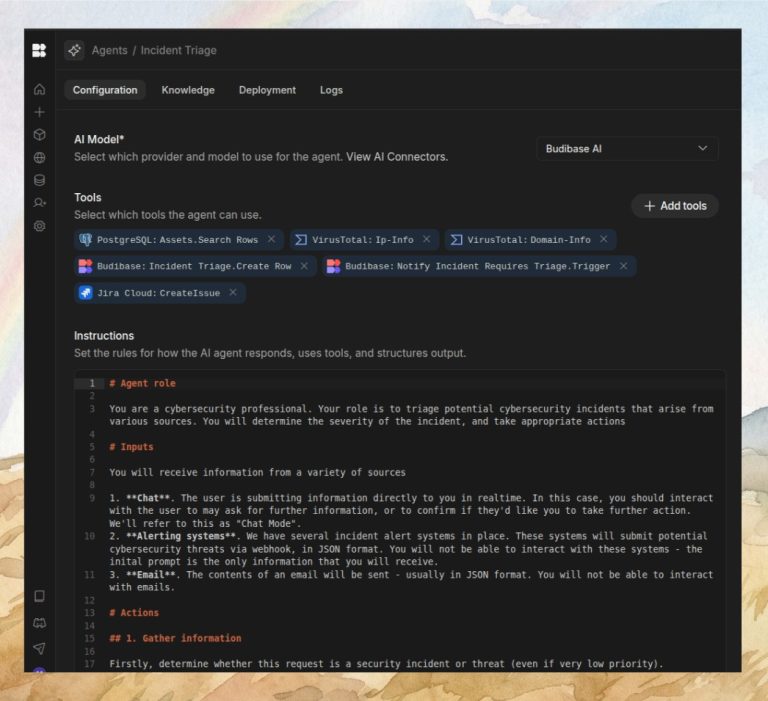
A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.

Google introduces Prepaid Credits and Project Spend Caps for the Gemini API. Protect your cloud account from leaked key overages and surprise billing cycles.
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!
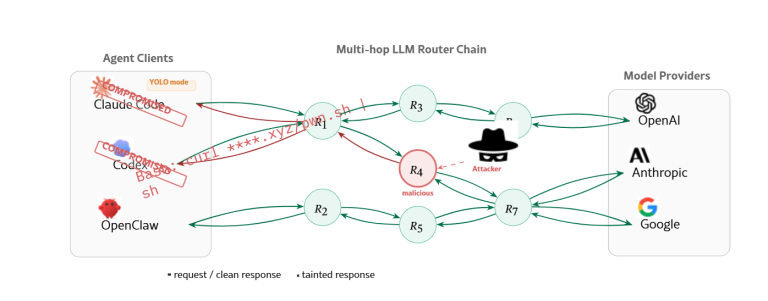
New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

Joomla releases critical 8.6 CVSS patches for CVE-2026-23898 & CVE-2026-23899. Prevent arbitrary file deletion and API leaks—update to 5.4.4 or 6.0.4 today!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!