
 Do Son
Kaspersky uncovered the BlackX UEFI bootkit APT41 campaign bypassing Secure Boot via Baton Drop to spy on Central Asian diplomatic agencies.
APT41
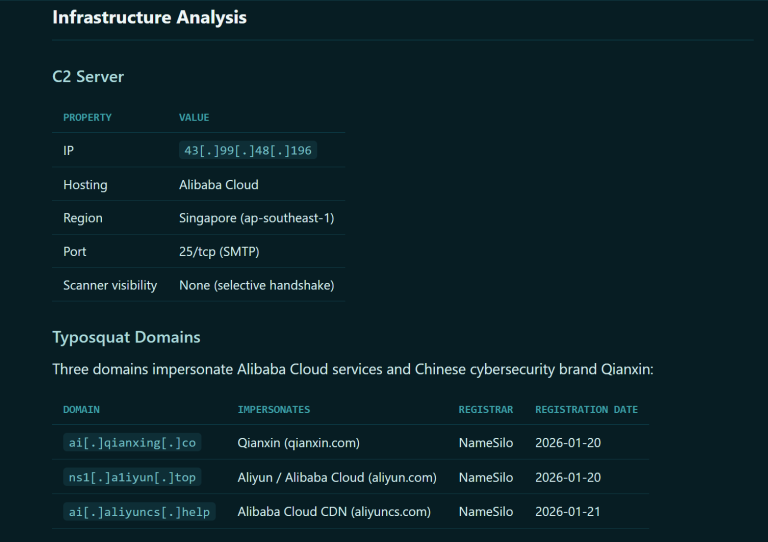
APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Taiwan's NSB reports 2.63M daily cyberattacks from China in 2025. Energy sector strikes spiked 1,000% as hybrid warfare intensifies.

Ink Dragon is weaponizing government servers in Europe using a relay-centric mesh. By hijacking IIS servers, they mask C2 traffic across global networks.

A China-linked APT targeted a U.S. policy nonprofit for weeks in April 2025. The group used DLL sideloading via a VipreAV binary and msbuild.exe scheduled tasks to achieve SYSTEM persistence for espionage.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.

Kaspersky uncovers a sophisticated APT41 cyberespionage campaign targeting African government IT, showcasing the Chinese group's full TTPs, including Impacket and Cobalt Strike.

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

APT41 is exploiting Google Calendar as a covert C2 channel in the TOUGHPROGRESS cyberespionage campaign, targeting government entities with stealthy malware.

A misconfiguration exposed APT41 tools targeting Shiseido, revealing Fortinet exploit scripts, webshells, and reconnaissance tactics.

Explore the evolving threat of ShadowPad malware, now facilitating ransomware attacks linked to Chinese threat actors.

Discover ScatterBrain, a powerful obfuscating compiler employed by APT41. Understand its role in protecting the advanced modular backdoor POISONPLUG.SHADOW.

Uncover the reality of cracked vulnerability scanning tools. Find out how cybercriminals are leveraging Acunetix Scanner for malicious purposes.

Get insights into APT41's DeepData framework, the latest revelation in the LightSpy espionage campaign. Discover its advanced surveillance capabilities and how it facilitates data theft across multiple communication platforms.

Uncover the sophisticated cyberattack campaign known as 'Pacific Rim.' Discover how China-based threat groups target high-value infrastructure and government organizations
Explore the evolving landscape of ransomware deployment by Chinese threat groups. Discover the motivations and tactics behind these attacks in this comprehensive report.

Discover the details of CVE-2018-0824, a critical Windows vulnerability being actively exploited. Stay protected and learn about the potential risks and impact.

Discover the details of a recent cyberattack targeting a Taiwanese research institute, believed to be carried out by the Chinese state-sponsored group APT41
Mandiant, has uncovered a widespread cyber espionage campaign orchestrated by the notorious advanced persistent threat group known as APT41