
 Do Son
CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.
Arctic Wolf
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
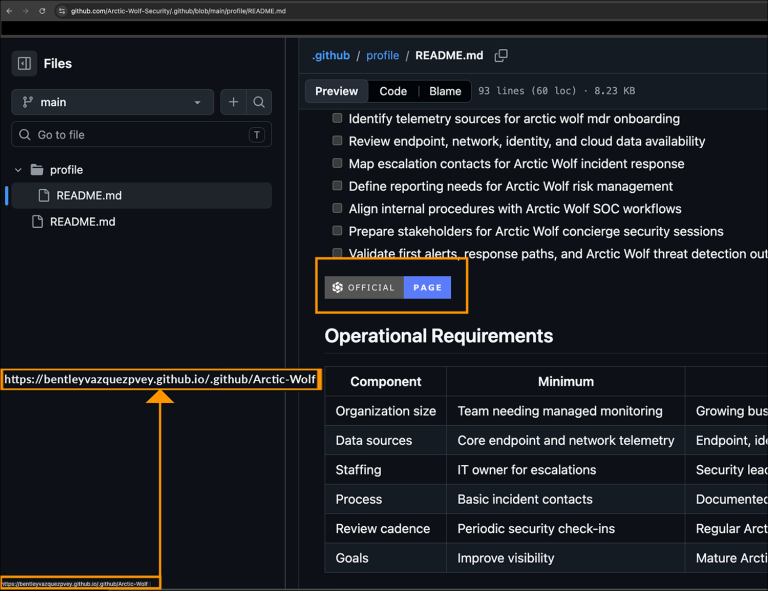
Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.

Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.

Arctic Wolf warns that hackers are actively exploiting a critical Quest KACE vulnerability (CVE-2025-32975) to completely take over enterprise networks.
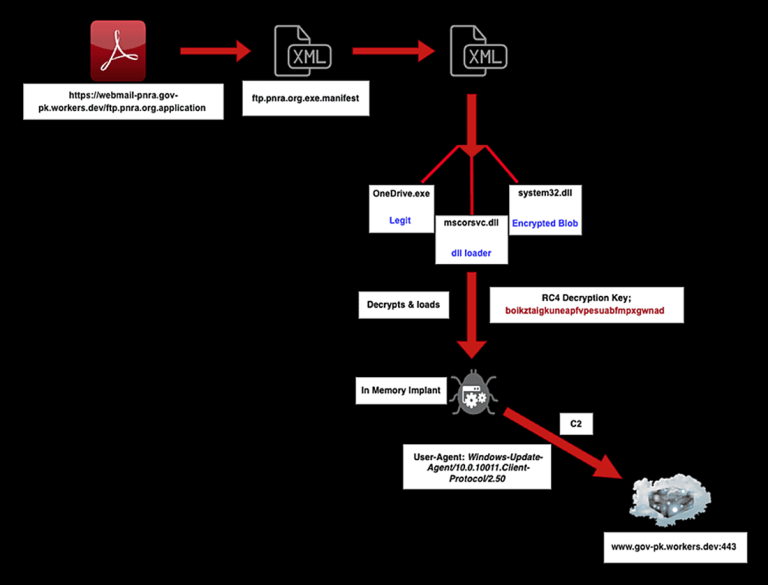
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.
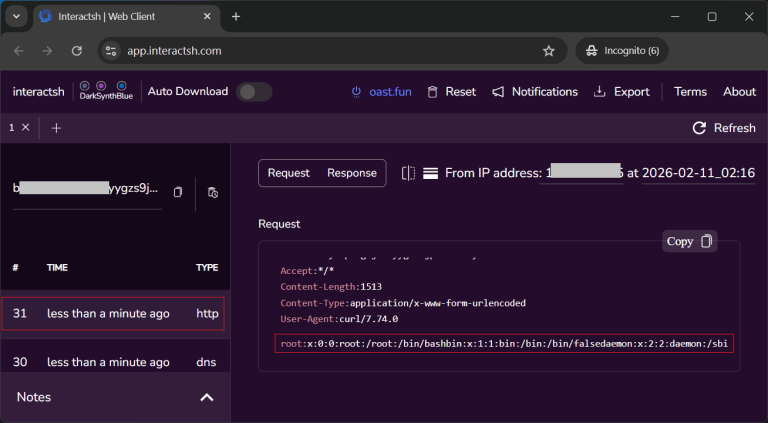
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.

CVE-2024-7399 vulnerability actively exploited in Samsung MagicINFO 9 Server allows remote code execution. Arctic Wolf reports in-the-wild attacks. Upgrade now!

Arctic Wolf exposes Venom Spider’s More_eggs campaign, where fake resumes and polymorphic JavaScript target HR to deploy a stealthy backdoor.