 Do Son
Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.
BRICKSTORM
Mandiant uncovers BRICKSTORM, a threat actor hiding in VMware vSphere for 393 days. Learn how to close the visibility gap and harden your ESXi infrastructure.

China-nexus WARP PANDA APT targets VMware/Azure with BRICKSTORM, a Golang backdoor using DoH for stealth. The group creates "ghost VMs" and conducts session replay attacks for long-term espionage.

CISA/NSA exposed BRICKSTORM, a Chinese state-sponsored backdoor targeting VMware vCenter/ESXi and ADFS servers. The self-restarting malware used DoH and nested TLS for 18 months of persistent espionage.

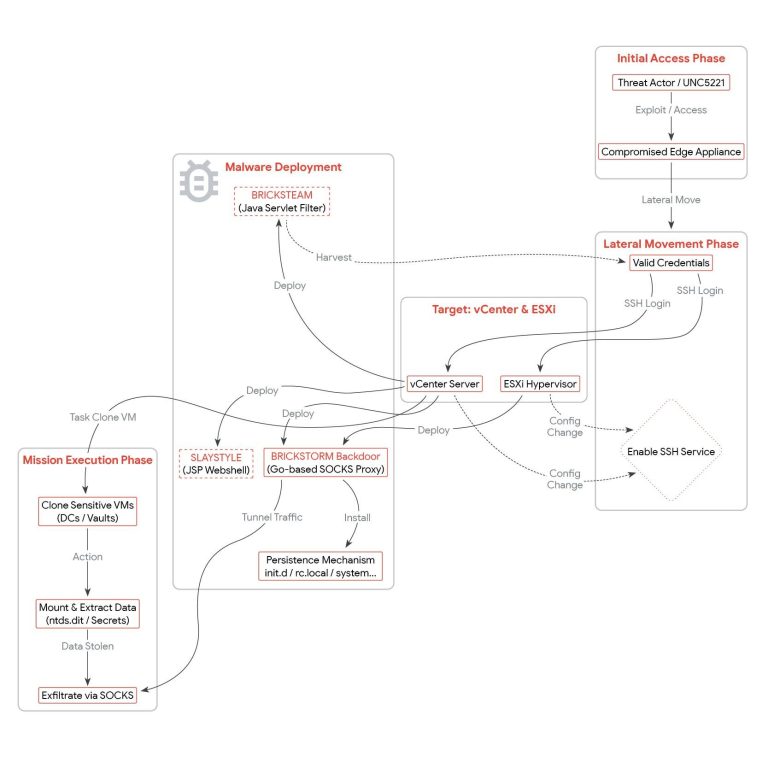
GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection