 Do Son
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
C2
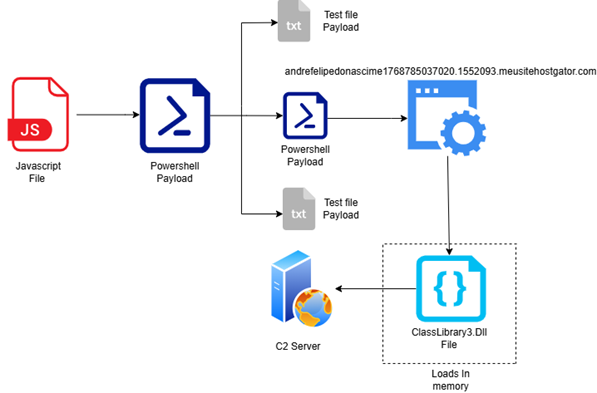
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.
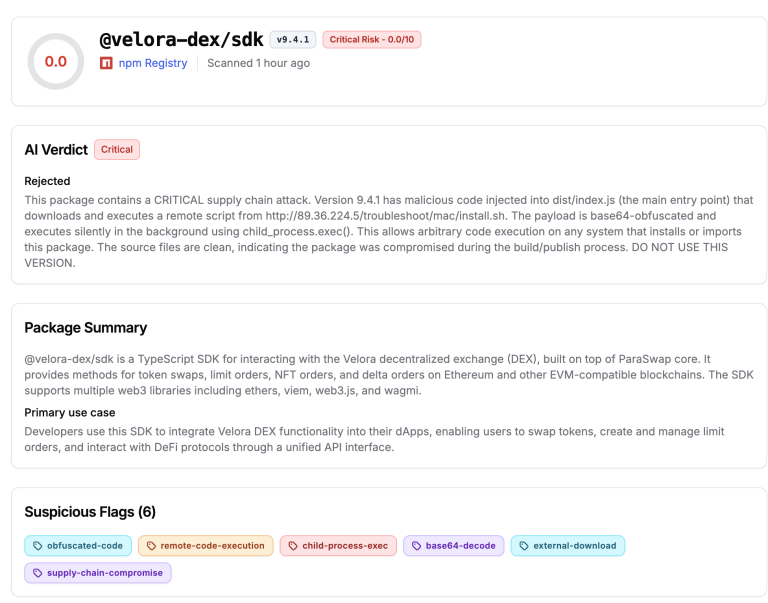
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.
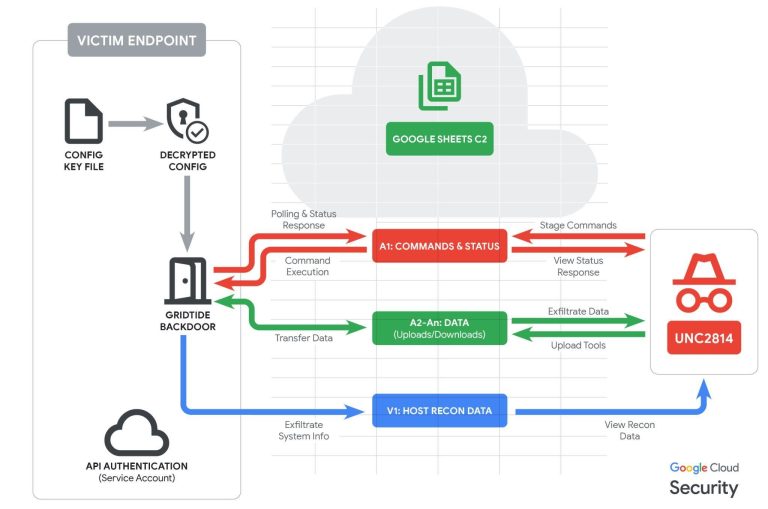
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

NANOREMOTE, a new Windows backdoor, leverages the Google Drive API for covert C2 and data exfiltration using OAuth 2.0 tokens. The malware shares a hard-coded AES key with the FINALDRAFT family, linking it to seasoned espionage actors.

Unit 42 exposed Airstalk, a suspected nation-state malware that abuses VMware AirWatch (MDM) APIs for a covert C2 dead drop. The tool is used to steal credentials and browser data in supply chain attacks.

Mandiant exposed UNC5142 for using EtherHiding—hiding malicious JavaScript in BNB Smart Chain smart contracts—to create a resilient C2 and distribute VIDAR/ATOMIC to 14,000+ sites.

Google exposed UNC5342 (DPRK APT) using EtherHiding—hiding JADESNOW/INVISIBLEFERRET malware in BNB/Ethereum smart contracts—for a resilient, nation-state C2 infrastructure.

eSentire discovered ChaosBot, a Rust-based malware deployed via DLL sideloading that uses Discord channels as a covert C2 platform to perform reconnaissance and command execution.

WARMCOOKIE has resurfaced post-Operation Endgame with new execution handlers, a MaaS model, and evasive techniques like disguised scheduled tasks using company names.

The Detour Dog campaign is using DNS TXT records for stealthy C2, infecting thousands of websites and quickly shifting infrastructure to evade sinkholing efforts.
Silent Push details how cybercriminals and APTs are misusing DDNS services for stealthy C2 servers, phishing, and malware delivery. Dozens of high-profile groups are involved.

A new report reveals TAG-150, a sophisticated new threat actor with evolving malware and a resilient multi-tiered infrastructure, including a new RAT called CastleRAT.

Socket uncovers 11 malicious Go packages, including 8 typosquats, on GitHub. The packages deliver stealthy, in-memory payloads that compromise developer machines and CI pipelines.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.

AhnLab uncovers SVF Bot, a Python-based DDoS botnet abusing Discord as its C&C channel to target misconfigured Linux servers and launch HTTP/UDP floods.

Unit 42 uncovers HazyBeacon, a novel backdoor using AWS Lambda URLs for stealthy C2. It's deployed via DLL sideloading, targeting Southeast Asian govts for trade documents.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

APT41 is exploiting Google Calendar as a covert C2 channel in the TOUGHPROGRESS cyberespionage campaign, targeting government entities with stealthy malware.
