 Do Son
OpenAI's June 2026 threat report exposes China influence operations that used banned ChatGPT accounts to target US AI and tariff debates.
china

The FCC is banning equipment testing data from China. Discover how this "security" mandate will force Apple, Google, and Samsung to hike prices and delay US launches.

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.

China's NDRC halts Meta’s $2B acquisition of Manus AI. Despite relocating to Singapore, the "agentic" startup faces the first-ever forced unwinding of a foreign AI deal.
PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
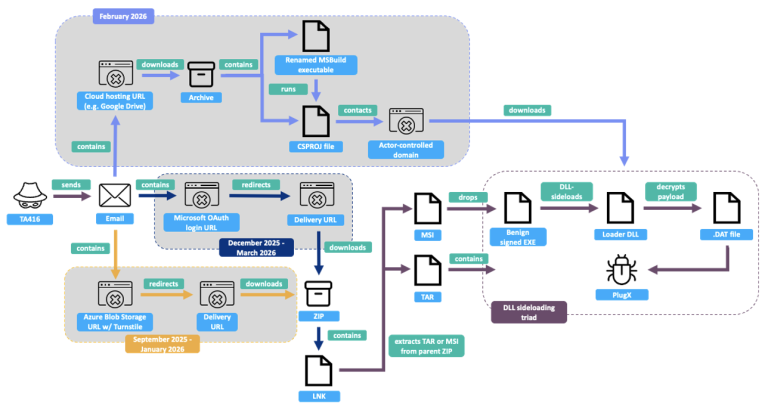
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Reuters: Meta executives tolerated $3B+ in scam/illegal ads from China due to revenue pressure, using "whitelisting" to protect top agencies and prioritizing profit over user safety.

In a major policy reversal, the U.S. will allow NVIDIA to export its H200 AI chips to China—but only with a mandatory 25% fee paid to the U.S. government.

XLab exposed RPX_Client, a new PolarEdge malware that turns IoT/router devices into a global ORB proxy network. The ELF binary uses XOR to encrypt config and spreads across 40 countries.

Qianxin exposed Bitter APT using a WinRAR path traversal flaw and malicious Office macros to deploy a C# backdoor against military/FinTech targets in Asia. The attack sets up scheduled persistence.

A Chinese APT, RedNovember, is using backdoors like Pantegana and SparkRAT to expand its global espionage, targeting U.S. defense, aerospace, and tech firms.
Trump signs an executive order to transfer TikTok's U.S. operations to American investors like Oracle, with ByteDance keeping a minority stake and the core algorithm.
After a call between U.S. and Chinese leaders, progress is being made on a deal for TikTok's U.S. operations. The deal still requires final approval.
A massive 600GB data leak from China's Great Firewall exposes its internal workings, source code, and proof of its export to other countries.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.

China's SAMR has launched a new probe into NVIDIA's 2019 Mellanox acquisition, alleging anti-monopoly violations and heightening tech tensions.
The Trump administration is expected to grant a fourth extension to the TikTok "sell-or-ban" deadline, providing the app with more time to find a U.S. buyer.

IBM X-Force reveals new findings on Hive0154, a China-aligned threat actor using an upgraded Toneshell backdoor and a new USB worm to target organizations.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.

A new report uncovers 45 previously unknown domains linked to the Chinese APT group Salt Typhoon. The findings reveal a long-term, multi-year espionage infrastructure.
NVIDIA's CFO has stated the company will not pay the U.S. government a 15% revenue share on China sales unless the agreement is formally codified into law.

A new Google report reveals a Chinese APT group is hijacking captive portals and disguised plugins to deliver malware for espionage against diplomats in Southeast Asia.