
 Do Son
Kaspersky GReAT uncovered OctLurk and SilkLurk, two new memory-resident backdoors targeting Central Asian governments since January 2025.
Chinese APT
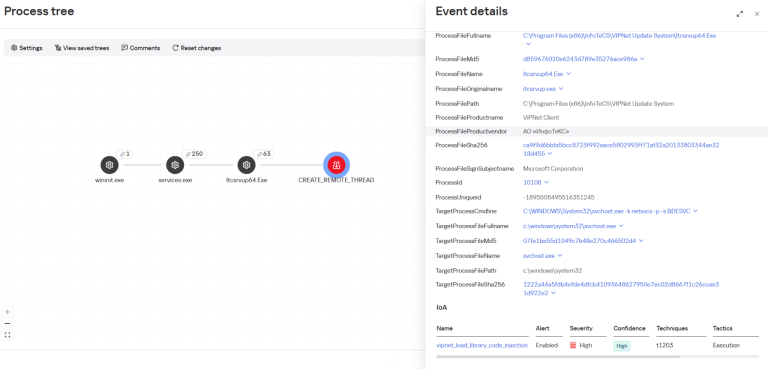
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.
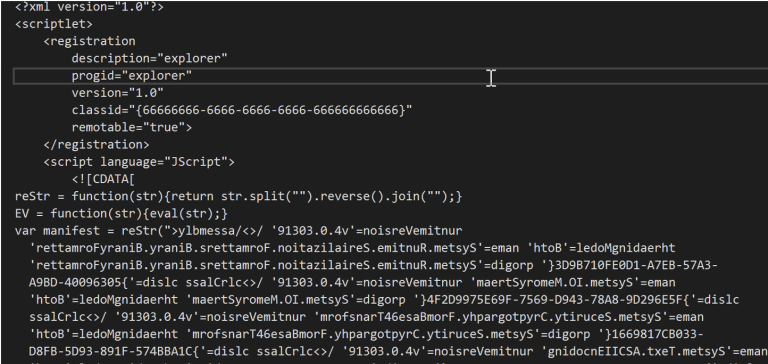
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.
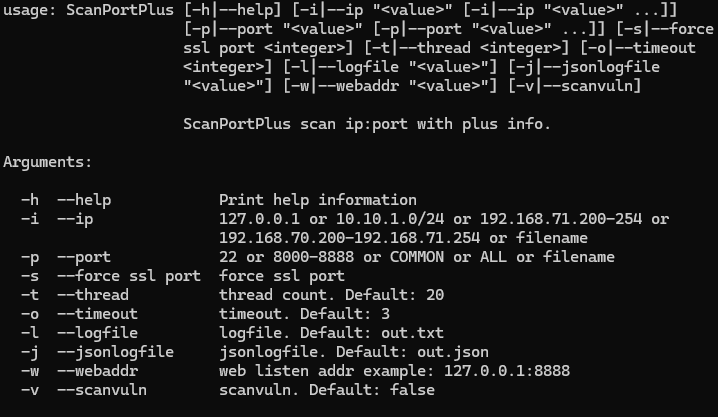
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

CISA adds a CVSS 10 Cisco zero-day and SonicWall exploit chains to its KEV catalog, warning of active exploitation by Chinese APTs and supply chain attacks.

Cisco warns of a CVSS 10 zero-day (CVE-2025-20393) exploited by Chinese APT UAT-9686 to backdoor Secure Email Gateways with the Aqua malware suite.

Arctic Wolf exposed Chinese APT UNC6384 exploiting the ZDI-CAN-25373 Windows LNK flaw to target European diplomats. The multi-stage attack uses DLL sideloading via a Canon binary to deploy the PlugX RAT.
Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage

Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage
Symantec exposed a complex Chinese APT network (Glowworm/UNC5221) deploying Zingdoor and ShadowPad across US/South American targets. The groups abuse DLL sideloading and PetitPotam for credential theft.

A Chinese APT used fake Cloudflare verification pages and malicious LNK files to inject PlugX via DLL sideloading into a Serbian aviation agency, aiming for long-term espionage.

Unit 42 uncovers Phantom Taurus, a new Chinese APT using the fileless NET-STAR backdoor to target SQL databases and IIS servers in global espionage campaigns.
A zero-day flaw in VMware Tools (CVE-2025-41244) allows local attackers to gain root privileges. NVISO confirmed exploitation by a Chinese APT. A public PoC is now available.

A new report reveals a Chinese APT group compromised a Philippine military company with a fileless malware framework called EggStreme, which uses DLL sideloading for stealth.

The NSA, CISA, and partners have released a joint advisory exposing how Chinese APT groups are compromising telecom and government networks for global espionage.
A new report from Cisco Talos details UAT-7237, a Chinese-speaking APT group targeting Taiwan's web infrastructure with customized open-source tools.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

A China-linked APT, UAT-6382, is actively exploiting a zero-day (CVE-2025-0994) in Cityworks to gain RCE and persistent access to government and utility systems.

Uncover the details of Operation Digital Eye, a sophisticated cyberespionage campaign targeting IT service providers in Southern Europe.

Uncover the tactics of Chinese APT groups in cyber espionage. Learn about zero-day exploits, LOTL techniques, and ORB networks in their evolving strategies.

Discover the latest tactic employed by the Chinese APT group Stately Taurus. Learn how they abuse Visual Studio Code to gain unauthorized access to sensitive networks.

In a shift of tactics that demonstrates their adaptability, Stately Taurus dispatched another malicious package, "Note PSO.scr," on March 5
A sophisticated espionage operation orchestrated by Chinese APT groups under the guise of innocuous cloud backup services