 Do Son
A Citrix security update fixes seven XenServer and UniconOS flaws, including guest-to-host and privilege escalation bugs. Patch hosts and thin clients.
Citrix
Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
Citrix NetScaler CVE-2026-88779 is exploited in the wild against NetScaler SAML authentication setups. Upgrade to 14.1-73.41 now.
Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
CVE-2026-19490 (CVSS 9.3) is a critical NetScaler authentication bypass in NetScaler Gateway and ADC. Patch now to block unauthenticated access.
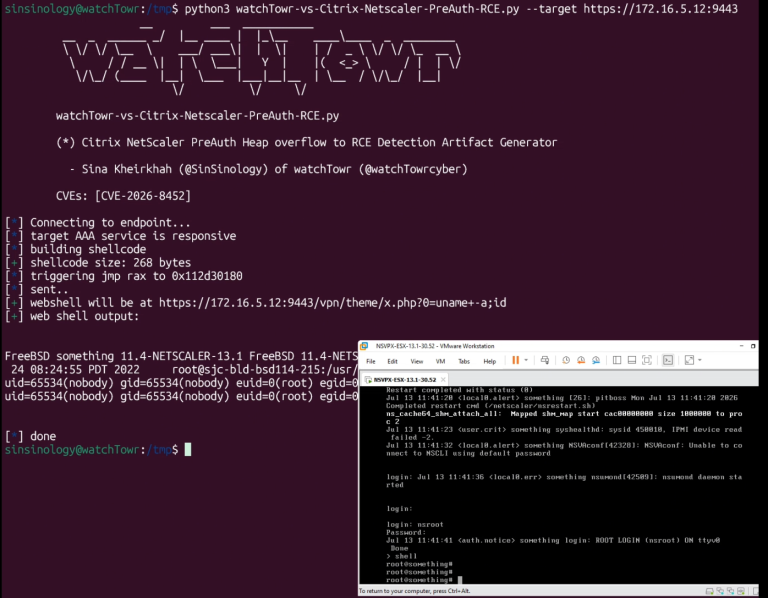
PoC exploit code for CVE-2026-8452, a Citrix NetScaler pre-auth RCE, is now public. The SAML heap overflow grants root. Patch now.
Citrix patched CVE-2026-53565, a Citrix Secure Access vulnerability letting local users gain SYSTEM, plus the CVE-2026-53566 out-of-bounds read bug.
Citrix NetScaler vulnerability CVE-2026-8451 is exploited in the wild after a public PoC exposed a pre-auth memory overread. Patch now.
Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.
Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.
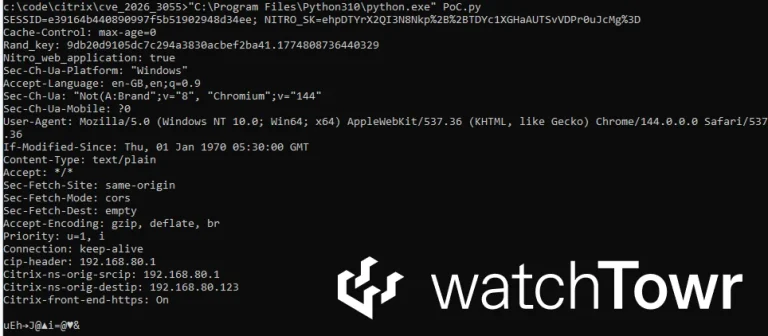
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
Cloud Software Group warns of a critical 9.3 CVSS memory overread in NetScaler. Patch now to prevent data exposure and session hijacking.

The Cloud Software Group has released urgent updates for NetScaler ADC and Gateway to patch a zero-day (CVE-2025-7775) being actively exploited in the wild.
CISA has added two Citrix and one critical Git vulnerability to its KEV Catalog, warning that all three flaws are being actively exploited by malicious actors.

CISA adds critical CitrixBleed 2 (CVE-2025-5777, CVSS 9.2) to KEV, confirming active exploitation. Attackers are extracting session tokens to bypass MFA and hijack sessions on NetScaler ADC/Gateway
Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)

Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)
Citrix warns of a high-severity local privilege escalation flaw (CVE-2025-6759, CVSSv4 7.3) in Windows VDA, allowing low-privileged users to gain SYSTEM access.

A critical flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway is actively exploited for DoS. Over 2,100 unpatched appliances remain susceptible. Update immediately!

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.
Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!
Cloud Software Group issues urgent patches for two critical NetScaler flaws allowing access bypass and memory overread. Update immediately.
Citrix has patched high-severity flaws in XenServer VM Tools for Windows that could allow attackers to compromise guest VMs. Update to version 9.4.1.
Learn about CVE-2024-12284, a high-severity vulnerability in the NetScaler Console that poses serious security risks.